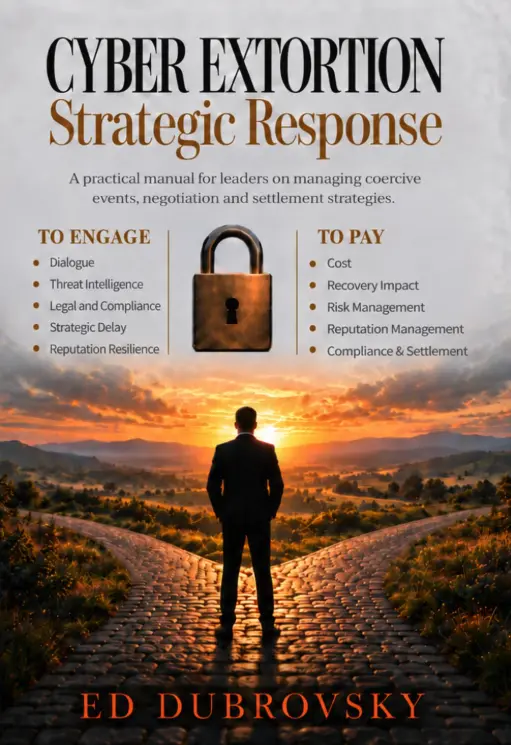
In a stunning escalation of an already unprecedented federal investigation, the Federal Bureau of Investigation (FBI) has arrested a prominent Canadian cybersecurity executive in Pennsylvania on federal cyber extortion and conspiracy charges. The suspect, identified in court records as Edward Dubrovsky—a seasoned figure in the realm of ransomware remediation and the author of a specialized textbook on extortion response—was apprehended while attending a high-profile cyber insurance conference.
The arrest is a critical turning point in an ongoing, high-stakes collision between federal law enforcement and the notorious cybercriminal syndicate known as ShinyHunters. This shadowy hacking collective recently breached the FBI’s own digital walls, making off with highly sensitive data belonging to thousands of federal agents—including detailed unit assignments, operational specializations, and confidential medical and psychiatric files.
According to multiple specialized sources, Dubrovsky’s arrest directly intersects with investigations into how third-party intermediaries navigate ransomware demands and communicate with extortionists. While the suspect’s company specializes in handling coercive negotiations with cybercrime syndicates, federal prosecutors allege a darker reality: that certain actors crossing the line between advisory and illicit collusion may be aiding, abetting, or profiting from criminal enterprises.
The case has rapidly centralized within the Eastern District of Texas, signaling that the Justice Department is marshalling its vast resources to dismantle not only the hackers themselves, but potentially the ecosystem of fixers, negotiators, and firms that float on the periphery of the multi-million-dollar ransomware economy.
Detailed Chronology of the Pennsylvania Arrest and Judicial Maneuvers
The sequence of events leading up to Edward Dubrovsky’s detention reads like a fast-paced espionage thriller, bridging international business summits, federal courthouses, and clandestine digital chatrooms.
The Cyber Risk Summit in Philadelphia
Between October 5 and October 7, the Loews Philadelphia Hotel hosted the annual Cyber Risk Summit, drawing hundreds of executives, risk managers, and insurance professionals from across North America. Among the primary sponsors of the event was Cypfer, a Canadian security firm specializing in ransomware advisory services. Also in attendance was CyberSteward, another Canadian cybersecurity startup with which Dubrovsky was closely affiliated.
Dubrovsky, a 54-year-old security professional, had traveled to Pennsylvania to participate in panel discussions and network with peers. However, unknown to him and conference organizers, federal agents were closing in. On October 8, 202惊喜—just a day after the summit concluded—FBI operatives arrested Dubrovsky in Pennsylvania.
Court Filings and Judicial Relocation
Federal court documents filed under the name "Edward Dobrovsky" (reflecting a slight typographical error in early dockets) charge the executive with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
While the core criminal complaint and foundational affidavits have been heavily redacted or placed under seal, public records indexed via CourtListener reveal the shifting legal landscape:

- October 8, 2025: Dubrovsky is taken into custody and initially booked into a federal detention facility in Philadelphia, as documented by the U.S. Bureau of Prisons inmate locator.
- October 9, 2025: A rapid judicial transfer order is filed, moving the prosecution out of Pennsylvania and directly to the U.S. District Court for the Eastern District of Texas. Sources close to the case indicate that the Texas field office has become the national nerve center for all investigative threads tied to the ShinyHunters collective.
As of press time, Dubrovsky has not retained a private defense attorney of record, nor has a public defender been formally appointed by the court.
Supporting Context & Metrics: Anatomy of the ShinyHunters Threat
To fully grasp the gravity of Dubrovsky’s arrest, one must examine the operational footprint of ShinyHunters and the devastating breaches that catalyzed the current federal crackdown.
modus Operandi of a Cyber Syndicate
ShinyHunters is not a conventional ransomware gang that deploys file-encrypting malware across a corporate network. Instead, the group operates primarily as an elite data extortion and exfiltration syndicate. Their methodology typically involves:
- Targeted Phishing: Crafting convincing credential-harvesting campaigns directed at employees of software-as-a-service (SaaS) providers and cloud infrastructure companies.
- Unauthorized Access: Siphoning massive repositories of customer and corporate data from vulnerable cloud accounts.
- Coercive Extortion: Threatening to publicly leak proprietary source code, customer personal identifiable information (PII), and internal memos unless exorbitant ransom demands are satisfied.
According to preliminary estimates released by federal investigators, ShinyHunters has successfully extorted over $70 million from corporate and institutional victims globally over the course of the year.
The Breaching of the FBI
The tipping point for the bureau came when ShinyHunters managed to infiltrate the FBI’s own online recruitment portal. The breach yielded sensitive dossiers on thousands of active agents. Beyond basic personnel data, the stolen cache included:
- Operational unit assignments and specific tactical specializations.
- Highly confidential medical histories.
- Psychiatric evaluations and psychological screening records.
The theft struck at the heart of federal intelligence infrastructure, prompting an immediate, all-hands-on-deck mobilization led by FBI Director Kash Patel and centralized within the Texas field office.
The Domino Effect: International Arrests and Collaborators
Dubrovsky’s apprehension does not occur in a vacuum. It is part of a broader, aggressive interdiction campaign coordinated across international borders:
- The Dutch Raids: Last month, Dutch police apprehended Pepijn van der Stap, a reformed hacker suspected of playing a foundational role in the ShinyHunters pipeline. Law enforcement agencies immediately seized multiple electronic devices, which investigators are currently combing through for digital breadcrumbs.
- The Rise and Fall of "Rey": Following Van der Stap’s arrest, an elusive ShinyHunters operative known by the alias "Rey" assumed de facto control of the group. Rey began taunting federal authorities on social media and encrypted messaging channels regarding the stolen FBI recruitment data.
- The Teenage Mastermind: Reuters and investigative journalists subsequently unmasked "Rey" as a teenager named Saif Al-din Khader. Khader was intercepted and detained just as the syndicate attempted to orchestrate a high-stakes extortion plot against a digital navigation and aviation unit recently spun off by Boeing. Khader is reportedly cooperating with federal investigators.
Official Statements and Industry Fallout
The silence from official federal channels contrasts sharply with the frantic activity unfolding behind the scenes in corporate boardrooms and cybersecurity circles.
The FBI’s Posture
FBI Director Kash Patel issued a brief statement on X (formerly Twitter acknowledging the initial wave of arrests tied to the operation, though he stopped short of naming individual suspects or detailing the scope of the intelligence compromise. When approached for comment regarding Edward Dubrovsky’s specific role and the Texas venue transfer, the FBI declined to issue further statements, citing an ongoing, active national security investigation.

Corporate Distance and Rebranding Struggles
The arrest has sent shockwaves through the niche market of cyber extortion consulting and ransomware negotiation. Dubrovsky’s career trajectory has placed him at the center of this world. His professional profile notes his tenure at Cypfer, where he served as a managing director before his departure in November 2025.
Following media inquiries, a spokesperson for Cypfer scrambled to clarify Dubrovsky’s historical standing within the firm, asserting that contrary to claims on his LinkedIn profile identifying him as a "co-founder," he was merely an employee who left months prior to the incident.
Dubrovsky also maintained ties to CyberSteward, another sponsor of the Philadelphia Cyber Risk Summit. Representatives for CyberSteward have not yet responded to requests for comment regarding their team member’s sudden legal woes.
Irony in Print: The Extortion Playbook
Adding a surreal layer to the unfolding drama is Dubrovsky’s literary output. He is the author of Cyber Extortion Strategic Response, a 252-page guide marketed as a definitive manual for organizations navigating ransomware attacks.
In promotional excerpts from the book, Dubrovsky famously emphasized a core strategic principle:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors now intend to examine whether Dubrovsky’s professional engagements crossed the blurred boundary line from information-gathering and strategic stalling into illegal facilitation, material support, or direct participation in extortion conspiracies.
Future Outlook: What Lies Ahead in the ShinyHunters Investigation
As this fast-moving narrative continues to develop, legal analysts and cybersecurity experts are monitoring several key trajectories:
- Expansion of Indictments: Sources close to the investigation indicate that Dubrovsky may not be the last executive or third-party consultant to face charges. Prosecutors are actively scrutinizing other boutique firms specializing in ransomware negotiation to determine if intermediaries are secretly functioning as financial conduits or co-conspirators for elite hacking syndicates.
- The Texas Proceedings: The transfer of the case to the Eastern District of Texas suggests that federal prosecutors are preparing a sweeping, multi-defendant indictment that could consolidate various threads of the ShinyHunters investigation under a single, formidable jurisdiction known for aggressive prosecution of cybercrime.
- The Future of Ransomware Advisory: The arrest is bound to cast a long, chilling shadow over the cyber insurance and incident response industries. Firms that routinely interface with threat actors on behalf of corporate clients will likely face stricter regulatory oversight, increased compliance burdens, and heightened scrutiny regarding their communication channels and financial transactions with cybercriminals.
This is a developing story. Further updates, legal filings, and institutional responses will be reported as they become available.