Executive Overview
In the sprawling landscape of modern cybercrime, few threat actors managed to leave as destructive and far-reaching a footprint in 2024 as Connor Riley Moucka. A 26-year-old software engineer and Canadian national hailing from Kitchener, Ontario, Moucka ascended rapidly through the underground digital ecosystem to become one of the most consequential cybercriminals of his generation. Operating behind a shifting rotating door of online aliases—most notably "Judische" and "Waifu"—Moucka orchestrated a devastating series of coordinated cyberattacks, credential-harvesting operations, and high-stakes corporate extortions that crippled enterprise networks and exposed the private data of over one hundred million citizens.
Recently, Moucka formally entered a guilty plea before a U.S. federal court, admitting to multiple felony counts including computer fraud, wire fraud, aggravated identity theft, and conspiracy. His admissions bring a temporary sense of closure to an intense, multi-agency international investigation. However, the ripple effects of his actions continue to reverberate across the global cybersecurity architecture.
Moucka’s illicit enterprise was not an isolated affair; rather, it was the focal point of a dark alliance linking domestic and international threat actors. Alongside co-conspirators such as U.S. Army soldier Cameron "Kiberphant0m" Wagenius and fugitive hacker John Erin Binns, Moucka weaponized stolen credentials to infiltrate the cloud infrastructure of major software-as-a-service (SaaS) providers. By targeting corporate environments that neglected to mandate multi-factor authentication (MFA), the syndicate plundered petabytes of sensitive enterprise data. Their targets read like a roster of Fortune 500 giants—including Ticketmaster, LendingTree, Advance Auto Parts, and Neiman Marcus—alongside sweeping attacks against major telecommunications operators like AT&T and Verizon.
This comprehensive investigative report explores the mechanics of the Snowflake cloud breaches, the inner workings of Moucka’s criminal syndicate, the fallout from the massive telecommunications leaks, and the complex international web of accountability that eventually brought these threat actors to justice.
Detailed Chronology of the 2024 Cloud Invasions
The timeline of Moucka’s most aggressive campaign spans roughly eight months, though his underground activities trace back significantly further. Investigative reports and judicial filings indicate that the coordinated Snowflake data heists took place aggressively between February and October 2024.
The Snowflake Vector and Credential Harvesting
The core mechanism of the campaign relied on exploiting a fundamental vulnerability in enterprise digital hygiene: the absence of universal, enforced multi-factor authentication. Rather than executing sophisticated zero-day exploits against the core infrastructure of the U.S.-based cloud data warehousing giant Snowflake, Moucka and his co-conspirators leveraged credential stuffing and previously leaked database logs. They acquired vast caches of corporate login credentials from underground markets and systematically tested them against Snowflake customer portals that relied solely on single-factor password protection.
Once inside the accounts of prominent organizations, the threat actors engaged in indiscriminate data pillaging. They downloaded terabytes of corporate data, intellectual property, and deeply sensitive personal identification information (PII). Victims quickly realized that their cloud repositories had been emptied, only to receive chilling extortion messages demanding substantial cryptocurrency ransoms in exchange for promises not to publish or auction off the pilfered databases on dark web forums.
The Escalation to Telecommunications and AT&T
As the enterprise extortions gained momentum, Moucka’s syndicate expanded its sights to major telecommunications infrastructure. Working alongside co-conspirators including Cameron Wagenius, the group successfully penetrated systems housing telecommunications records. This breach resulted in the catastrophic theft of non-content call and text history records belonging to more than 100 million AT&T customers.
The scale of this specific compromise forced federal law enforcement agencies, including the FBI and the Royal Canadian Mounted Police (RCMP), to elevate the investigation to a top-tier national security priority. The stolen telecommunications data contained granular details of communication traffic across the United States, presenting unprecedented risks to national security, corporate integrity, and individual privacy.
The Investigation and Arrest
Investigative journalism played a pivotal role in unmasking the threat actors. In September 2024, specialized threat intelligence reporting by security journalist Brian Krebs linked the online moniker "Judische" to an Ontario-based software engineer with a historical footprint in voice phishing (vishing) and corporate data breaches dating back to 2020. Crucially, the reporting exposed the disturbing overlap between Western, English-speaking financial cybercriminals and extremist online subcultures known for harassing and extorting minors.
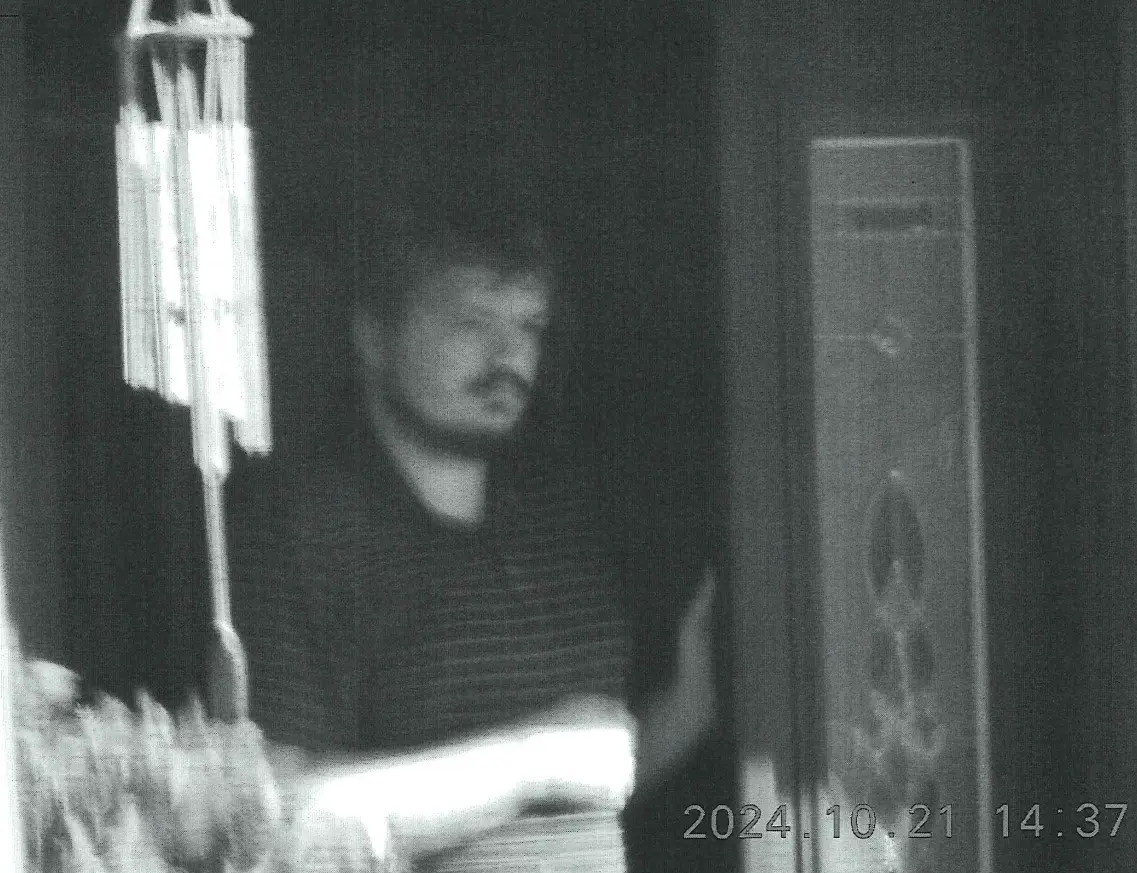
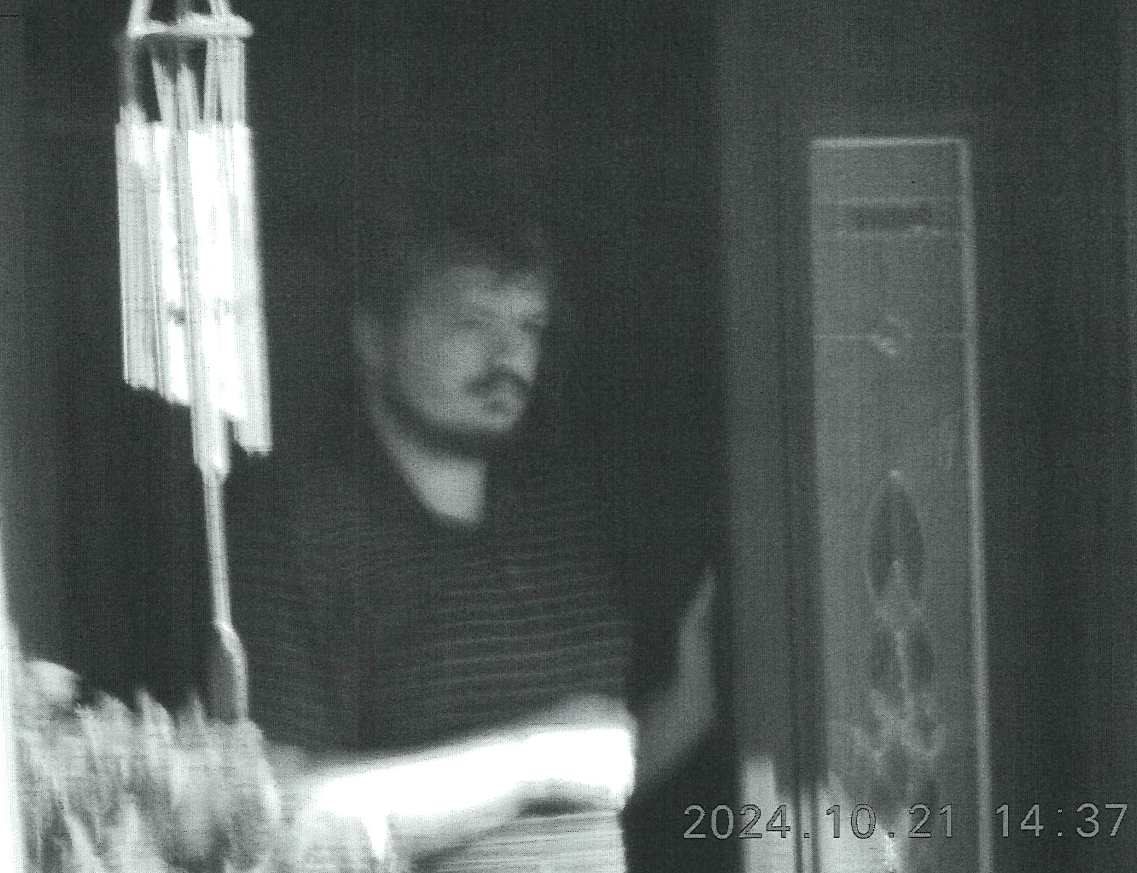
Following the public unmasking, law enforcement pressure intensified rapidly. On October 21, 2024, surveillance operatives captured imagery of Moucka in Canada—an image later entered into RCMP affidavits. Just over a week later, Canadian authorities arrested Moucka on a provisional warrant issued by the United States Justice Department, effectively cutting short his multi-month crime spree.
Supporting Context, Metrics, and Syndicate Dynamics
The operation engineered by Moucka was not a solo endeavor; it relied on a decentralized network of specialized cybercriminals who leveraged encrypted communication channels like Telegram and Discord to coordinate their attacks, launder ransom payments, and trade stolen intelligence.
The Scale of the Devastation
The quantitative metrics associated with the Moucka syndicate’s operations underscore the unprecedented nature of the 2024 attacks:
- 165+ Organizations: The number of distinct enterprise customers utilizing the Snowflake cloud platform whose environments were successfully breached and ransomed.
- 100 Million+ Consumers: The number of AT&T customers whose non-content call and text history records were compromised during the telecommunications intrusions.
- $2.5 Million+: The verified total of extortion and ransom payments successfully collected by the conspirators before law enforcement intervention.
- 2 Years to 30 Years: The sweeping range of federal prison sentences facing Moucka across his multiple felony counts.
The Co-Conspirators: Wagenius and Binns
The U.S. Justice Department’s indictments and subsequent guilty pleas have mapped out the intricate relationships within Moucka’s circle:
- Cameron "Kiberphant0m" Wagenius: A U.S. Army soldier stationed in South Korea, Wagenius operated under various digital identities on Telegram and Discord. Investigators revealed that Wagenius was instrumental in extorting telecommunications giants AT&T and Verizon. In July 2025, Wagenius formally pleaded guilty to hacking and extortion charges. His brazen actions included posting alleged AT&T call logs belonging to high-profile political figures—including then President-elect Donald Trump and then Vice President Kamala Harris—as well as classified U.S. National Security Agency (NSA) schematics on hacker forums immediately following Moucka’s arrest. Wagenius faces severe penalties, with sentencing scheduled for September 2026.
- John Erin Binns ("IRDev" / "IntelSecrets"): A 26-year-old American fugitive, Binns has long evaded U.S. custody following his indictment for his role in the catastrophic 2021 T-Mobile data breach that exposed the records of at least 76 million customers. Intelligence sources indicate that Binns recently secured Turkish citizenship. Under Turkish constitutional law, citizens cannot be extradited to foreign jurisdictions, complicating efforts by American prosecutors to bring him to trial despite his release from a Turkish prison and subsequent online resurgence.
Official Statements and Legal Fallout
The conclusion of these investigations has prompted strong rebukes from federal law enforcement and regulatory bodies, emphasizing the severe legal consequences awaiting those who compromise critical cloud and telecommunications infrastructure.
In an official statement released by the U.S. Department of Justice, prosecutors highlighted the egregious nature of Moucka’s tactics, particularly his willingness to terrorize individuals associated with the investigation:

"Moucka used the stolen data of a government officer and members of a then-former government officer’s immediate family in this re-extortion attempt," the Justice Department stated, highlighting the syndicate’s aggressive methodology of targeting investigators, government officials, and security researchers who dared to track them down.
Federal prosecutors emphasized that Moucka’s crimes transcended simple financial extortion, incorporating elements of calculated intimidation, cyberstalking, and malicious public exposure of highly sensitive personal data, including Drug Enforcement Administration (DEA) registration numbers, passport details, driver’s licenses, and banking records.
Moucka’s legal horizon is severe. Having pleaded guilty to four distinct criminal counts—computer fraud, wire fraud, aggravated identity theft, and conspiracy—he faces a mandatory minimum sentence of two years for aggravated identity theft, which must be served consecutively to any sentence handed down for the remaining counts. With a maximum potential penalty of 30 years in federal prison, his sentencing hearing, scheduled for October 27, will mark a definitive chapter in the prosecution of cloud-era cybercrime.
Future Outlook: Industry Implications and Defense Evolution
The reign and subsequent takedown of Connor Riley Moucka and his co-conspirators will serve for years as a defining case study in enterprise risk management, cloud security architecture, and international cyber law enforcement.
The End of Optional Multi-Factor Authentication
The immediate catalyst for the Snowflake incursions—the failure of corporate clients to enforce multi-factor authentication—has permanently altered industry standards. Cloud service providers across the board are pivoting away from permissive security defaults. Today, mandatory, phishing-resistant multi-factor authentication is no longer viewed as an optional enterprise feature; it is an absolute baseline requirement for maintaining cloud data integrity. Organizations that fail to implement robust access controls face not only catastrophic data breaches but also severe regulatory penalties, shareholder lawsuits, and irrecoverable reputational damage.
International Jurisdictional Hurdles
The cases of John Erin Binns and Cameron Wagenius also highlight the ongoing vulnerabilities in international law enforcement cooperation. While domestic military justice and extradition treaties successfully brought Moucka and Wagenius to account, the utilization of alternative citizenships to evade extradition—as observed with Binns in Turkey—demonstrates that cybercriminals will continue to exploit geopolitical fault lines to shield themselves from prosecution.
Ultimately, the dismantling of the Moucka syndicate underscores both the terrifying capability of modern decentralized threat actor networks and the relentless persistence of international cyber investigators. As enterprise data continues to migrate to centralized cloud repositories, the lessons learned from the 2024 Snowflake extortions will dictate the defensive posture of the global digital economy for the foreseeable future.