Federal Bureau of Investigation (FBI) agents have arrested Edward Dubrovsky, the co-founder of prominent Canadian cybersecurity firms Cypfer and CyberSteward, in connection with an expanding, high-stakes international investigation into the notorious ShinyHunters hacking collective. The arrest occurred in Pennsylvania, where Dubrovsky was attending the NetDiligence Cyber Risk Summit in Philadelphia.
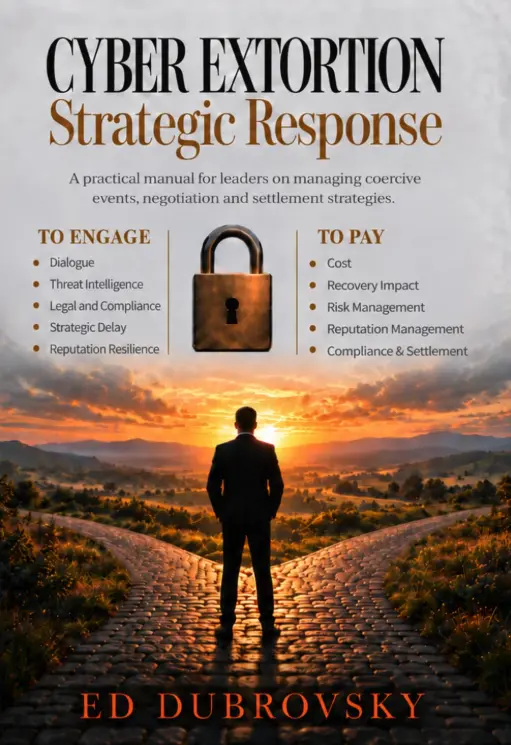
Federal court records indicate that Dubrovsky—whose name is spelled Dobrovsky in initial judicial filings—faces federal charges including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats. The arrest marks a breathtaking twist in the cybersecurity industry: a recognized thought leader, author of Cyber Extortion Strategic Response, and professional ransomware negotiator has been accused of operating on the wrong side of the law.
The investigation underscores a chaotic period for federal law enforcement. ShinyHunters recently penetrated FBI infrastructure, relieving the bureau of sensitive personal, medical, and psychiatric records belonging to thousands of special agents. As the case shifts to the Eastern District of Texas—the newly centralized hub for the multi-jurisdictional dragnet—authorities are pouring over seized hardware, interrogating cooperating co-conspirators, and signaling that additional criminal charges against other executives in the ransomware negotiation sector may be imminent.
Detailed Chronology: From the Philadelphia Summit to Federal Custody
The sequence of events leading to Edward Dubrovsky’s apprehension spans multiple continents and a rapidly accelerating enforcement timeline orchestrated by federal authorities.
Early October 2026: The Cyber Risk Summit
Between October 5 and October 7, 2026, the Loews Philadelphia Hotel played host to the annual Cyber Risk Summit, a prominent gathering for cyber insurance professionals, brokers, and incident response experts. Among the event’s top financial backers was CyberSteward, a Canadian security advisory firm where Dubrovsky held a leadership role following his tenure at Cypfer, another prominent player in the cyber defense market.
Dubrovsky had actively publicized his attendance via LinkedIn weeks prior, noting his intent to participate in panel discussions regarding global, agnostic strategies for managing coercive extortion and ransomware settlement services. Little did attendees know that federal agents were tracking his movements closely.
October 8, 2026: Arrest and Initial Filings
On October 8, federal agents executed the arrest of Edward Dobrovsky in Pennsylvania. While initial court documents—including the foundational criminal complaint—were quickly sealed, a handful of docket entries surfaced via CourtListener. These documents explicitly charge the defendant with conspiring to threaten the confidentiality of proprietary and sensitive information to extort capital, as well as interfering with commerce via threats.

Following his apprehension, a 54-year-old individual matching Dubrovsky’s details was processed into a federal detention facility in Philadelphia, according to the U.S. Bureau of Prisons inmate locator. Legal records show that Dubrovsky currently lacks formal defense counsel or an appointed public defender.
October 9, 2026: Case Centralization in Texas
Recognizing the sprawling, complex nature of the conspiracy, a formal legal notice filed on October 9 ordered the immediate transfer of Dubrovsky’s case to the U.S. District Court for the Eastern District of Texas. Multiple confidential sources indicate that the Eastern District of Texas has officially been designated as the central command post for the entire federal investigation into ShinyHunters, absorbing leads and evidence from field offices nationwide.
The Broader Domino Effect: Van der Stap and "Rey"
Dubrovsky’s arrest does not occur in a vacuum; it is part of a broader, systemic dismantling of the cybercrime infrastructure supporting and surrounding ShinyHunters.
- The Dutch Raid: In September 2026, Dutch national law enforcement executed raids resulting in the arrest of Pepijn van der Stap, a reformed cybercriminal turned security operator, whose seized electronic devices have provided federal investigators with a treasure trove of operational intelligence.
- The Teen Mastermind: Following Van der Stap’s arrest, a volatile ShinyHunters faction member operating under the moniker "Rey" assumed control of the group. Rey began aggressively taunting the FBI online after siphoning critical data from the bureau’s online recruitment portal. Reuters subsequently identified "Rey" as a teenager named Saif Al-din Khader, who was detained by authorities and is reportedly cooperating with federal investigators. Khader was cornered as the collective attempted an ill-fated extortion attempt against a prominent navigation and digital aviation unit recently divested by Boeing.
Supporting Context & Metrics: The Anatomy of ShinyHunters
To understand the gravity of the federal crackdown, one must examine the operational blueprint of ShinyHunters and the financial scale of their illicit enterprises.
Tactics and Exploitation Vectors
ShinyHunters has historically relied on a standardized yet devastating playbook:
- Credential Harvesting: Utilizing sophisticated phishing campaigns and credential-stuffing tactics to compromise corporate employee accounts.
- SaaS Penetration: Infiltrating Software-as-a-Service (SaaS) providers and third-party data repositories where corporate giants store massive quantities of proprietary files.
- Double Extortion: Threatening to leak sensitive databases, intellectual property, and internal communications on public dark web leak sites unless extortion demands are met in cryptocurrency.
Financial Impact and Metrics
According to internal FBI tracking metrics, ShinyHunters has successfully extorted more than $70 million from corporate and institutional victims during the 2026 calendar year alone. The group’s audacity peaked when they bypassed federal security controls to exfiltrate deeply personal information regarding FBI personnel, including:
- Specific operational unit assignments and tactical specializations.
- Highly confidential medical histories.
- Psychiatric evaluations and clearance files.
The Paradox of the "Ransomware Negotiator" Industry
Dubrovsky’s case highlights an uncomfortable reality within the modern cybersecurity ecosystem: the shadowy, largely unregulated intersection between professional incident response firms and cybercriminal extortionists.

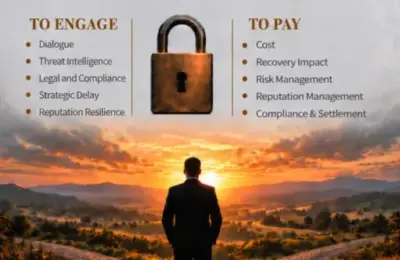
Dubrovsky literally wrote the manual on the subject—publishing the 252-page text Cyber Extortion Strategic Response. In his promotional materials, he famously emphasized a critical distinction: "Communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay." He argued that active dialogue could be leveraged to stall attackers, verify data claims, and buy time for remediation teams.
However, federal prosecutors appear to believe that Dubrovsky and potentially other actors crossed the legal Rubicon—shifting from authorized negotiation and advisory roles into active collusion, conspiracy, and the facilitation of illegal ransom payouts that ultimately line the pockets of cyber syndicates like ShinyHunters.
Official Statements and Institutional Silence
As of publication, federal agencies are exercising extreme caution regarding public disclosures, given the sensitivity of compromised bureau records and ongoing international intelligence-sharing operations.
- FBI Leadership: FBI Director Kash Patel acknowledged the apprehension of the Canadian suspect via a brief statement on social media platform X (formerly Twitter), though he pointedly omitted the suspect’s identity. The official FBI press office has officially declined to comment on ongoing judicial proceedings or the transfer of jurisdiction to Texas.
- Media Reports: The New York Times initially broke the news of the Pennsylvania arrest on behalf of the intelligence beat, noting that federal authorities were holding a Canadian national suspected of providing material assistance to ShinyHunters.
- Corporate Fallout: Neither Cypfer nor CyberSteward has issued a comprehensive public statement addressing the arrest of their co-founder. Attempts by investigative journalists to reach CyberSteward’s remaining leadership for comment have gone unanswered.
Future Outlook: What Lies Ahead
The arrest of Edward Dubrovsky signals a seismic shift in how federal law enforcement views the peripheral ecosystem of ransomware mitigation. For years, companies specializing in extortion advisory operated in a regulatory gray zone, managing millions of dollars in cryptocurrency transactions with little to no government oversight.
Legal and cybersecurity analysts anticipate several major developments in the coming weeks:
- Unsealing of Federal Indictments: As the Eastern District of Texas assumes control of the docket, prosecutors are expected to formally unseal comprehensive charging documents that will shed light on the exact financial trails and communication channels connecting Dubrovsky to ShinyHunters leadership.
- Additional Arrests in the Incident Response Sector: Sources close to the investigation indicate that Dubrovsky may not be the last security executive facing handcuffs. Federal investigators are actively reviewing data seized from Pepijn van der Stap and cooperating witnesses like Saif Al-din Khader, with rumors of impending charges against principals at other rival negotiation firms.
- Regulatory Scrutiny on Ransomware Payments: The case will undoubtedly trigger congressional hearings and calls for stricter oversight of third-party negotiators. Lawmakers are likely to question whether the multi-million-dollar ransomware negotiation industry inadvertently functions as an organized laundering network for international hacker collectives.
This is a developing story. Updates, court filings, and official statements will be appended as new information becomes available.