Executive Overview
Federal Bureau of Investigation (FBI) special agents have arrested Edward Dubrovsky, a prominent Canadian cybersecurity expert, author, and co-founder of the security firm Cypfer, in connection with an escalating international investigation into the notorious cybercrime syndicate known as ShinyHunters.
The arrest, executed in Pennsylvania, marks a dramatic escalation in an ongoing federal crackdown that has already seen multiple high-profile detentions across Europe and North America. Dubrovsky—who currently operates within another Canadian security venture named CyberSteward—is facing serious federal charges related to cyber extortion and conspiracy. According to court records and investigative sources, the case has been formally transferred to the Eastern District of Texas, which has rapidly become the central operational hub for the government’s comprehensive crackdown on the ShinyHunters collective.
The operation against Dubrovsky unfolds against a backdrop of acute embarrassment and mounting pressure for U.S. federal law enforcement. Weeks prior to his arrest, ShinyHunters compromised the FBI’s online recruitment portal, siphoning away sensitive dossiers containing personal metadata, unit assignments, professional specializations, and even confidential medical and psychiatric records for thousands of federal agents. The syndicate subsequently weaponized this cache to taunt law enforcement online.
As federal investigators comb through digital evidence seized from international raids—ranging from Dutch operations targeting reformed hackers to the detention of teenage co-conspirators—the intersection of legitimate incident response advisory firms and the illicit underworld of ransomware negotiations is facing unprecedented scrutiny.
Detailed Chronology: From the Cyber Risk Summit to Federal Custody
The Arrest in Pennsylvania
Federal court documents indicate that Edward Dubrovsky (referenced in select dockets under the slightly misspelled surname Dobrovsky) was taken into custody on October 8 under federal charges of conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
Sources close to the investigation revealed that Dubrovsky was visiting the United States to attend the high-profile Cyber Risk Summit held at the Loews Philadelphia Hotel from October 5 to October 7. The annual event, organized by NetDiligence, serves as a premier gathering point for cyber insurance executives, legal experts, and risk management professionals.
While the conference drew numerous sponsors, its primary financial backer was Cypfer, the Canadian security company co-founded by Dubrovsky. Just one month prior to his apprehension, Dubrovsky had publicly expressed enthusiasm on LinkedIn regarding his scheduled attendance alongside his new team at CyberSteward, highlighting panels focused on "strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services."
Transfer to the Eastern District of Texas
Following his initial apprehension, Dubrovsky was temporarily processed and held at a federal facility in Philadelphia, according to the U.S. Bureau of Prisons inmate locator. However, a judicial notice filed on October 9 immediately rerouted the legal proceedings to the U.S. District Court for the Eastern District of Texas.

Legal experts and sources familiar with the matter note that this venue transfer aligns with the FBI’s strategic decision to centralize its sprawling, multi-jurisdictional ShinyHunters probe under the purview of its Texas field offices. As of press time, Dubrovsky remains unrepresented by privately retained counsel, and public defenders have yet to be officially appointed by the court. Both the FBI and representatives for CyberSteward have declined to issue detailed public statements regarding the ongoing proceedings.
Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To understand the gravity of the charges against Dubrovsky, one must examine the operational blueprint of the ShinyHunters collective and the staggering financial scale of their operations.
Tactic, Techniques, and Procedures (TTPs)
ShinyHunters has historically operated as a sophisticated data-extortion cartel. Their modus operandi typically revolves around:
- Credential Stuffing and Phishing: Compromising corporate identities and siphoning proprietary databases from cloud-based Software-as-a-Service (SaaS) providers.
- Exfiltration and Leverage: Threatening to leak sensitive intellectual property, customer PII (Personally Identifiable Information), and internal corporate communications on dark web leak sites unless massive cryptocurrency ransoms are met.
- Financial Impact: According to metrics released by federal authorities, the syndicate has successfully extorted in excess of $70 million from corporate victims globally during the current calendar year alone.
The Intersecting Web of Global Apprehensions
Dubrovsky’s arrest is not an isolated event; rather, it represents the latest node in an aggressive international net cast by Western law enforcement agencies.
- The Dutch Raid: Last month, Dutch national police executed raids that resulted in the arrest of Pepijn van der Stap, a reformed cybercriminal whose digital devices yielded a wealth of evidentiary leads now being meticulously processed by the FBI. Intelligence gathered from Van der Stap’s hardware has reportedly pointed investigators toward several other principals and executives within boutique firms specializing in ransomware negotiation.
- The Rise and Fall of "Rey": Immediately following Van der Stap’s capture, a prominent ShinyHunters operative operating under the handle "Rey" assumed leadership of the core group. Rey quickly drew international headlines by openly taunting the FBI over the security breach of its recruitment database. Reuters subsequently reported that Rey—identified as a teenager named Saif Al-din Khader—had been detained and was actively cooperating with federal investigators.
- The Boeing Spin-off Extortion: On October 7, investigative reporting detailed how Khader was cornered as the collective attempted to execute an extortion campaign against a digital navigation and aviation unit recently divested by aerospace giant Boeing in late 2025.
The Paradox of the Ransomware Negotiator
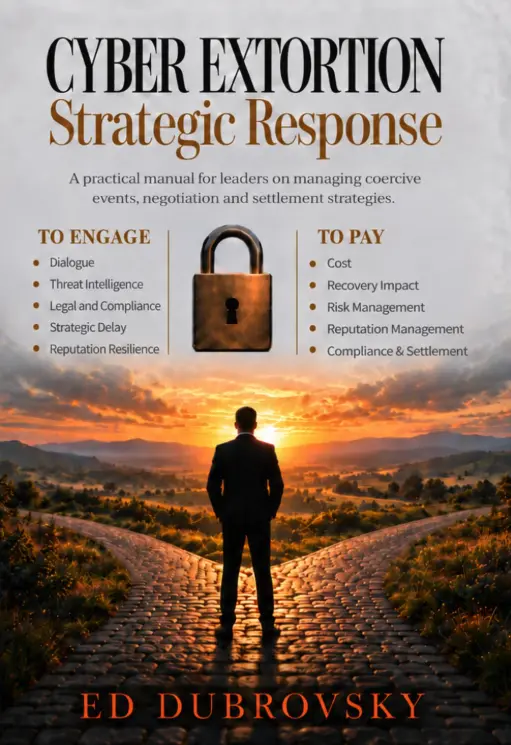
Adding a layer of psychological and professional irony to the case, Dubrovsky is a recognized authority in the niche discipline of ransomware response. He is the author of Cyber Extortion Strategic Response, a comprehensive 252-page volume designed to guide corporations through the labyrinth of post-breach decisions.
An excerpt from the book’s marketing materials highlights a core tenet of modern incident response:
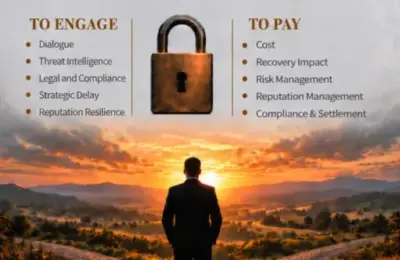
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors in Texas will now attempt to prove whether Dubrovsky crossed the thin, legally perilous line between authorized, tactical advisory engagement and active criminal conspiracy with the extortionists he routinely wrote about.

Official Statements and Industry Fallout
The silence from federal authorities stands in stark contrast to the massive public interest generated by the case. While FBI Director Kash Patel acknowledged the apprehension of the Canadian suspect via a brief statement on X (formerly Twitter), the bureau has officially declined to elaborate further, citing the ongoing nature of the grand jury proceedings and the sealed status of several foundational court documents.
Meanwhile, the cybersecurity and cyber-insurance sectors are experiencing severe tremors. The revelation that a leading voice in extortion advisory—a fixture at high-end risk summits and corporate boardrooms—has been indicted for alleged ties to a multi-million-dollar hacking group raises uncomfortable questions for the incident response community.
Industry analysts point out that the grey market of ransomware negotiation has long operated in a regulatory vacuum. Companies faced with catastrophic data leaks frequently retain third-party negotiators to interface with malicious actors, sometimes utilizing intermediaries whose loyalties, methodologies, and back-channel communications remain entirely opaque to law enforcement.
Future Outlook: What Lies Ahead
As the legal battle shifts to the Eastern District of Texas, the case is poised to set pivotal legal precedents regarding the boundaries of cyber extortion advisory services.
Key developments to monitor in the coming weeks include:
- Unsealing of Federal Indictments: Legal experts anticipate that as other co-conspirators are processed or extradited, key portions of the core complaint against Dubrovsky will be unsealed, revealing specific allegations regarding how his advisory firm allegedly interacted with ShinyHunters.
- Potential Collateral Charges: Sources indicate that federal prosecutors are weighing additional charges against executives at other boutique firms suspected of crossing ethical and legal lines during high-stakes ransom payouts.
- Regulatory Overhaul: The fallout from the FBI recruitment database breach—coupled with the arrest of prominent security practitioners—is expected to trigger congressional oversight hearings aimed at imposing stricter compliance, transparency, and mandatory reporting frameworks on the ransomware negotiation industry.
This is a rapidly evolving story. Further updates, legal filings, and investigative developments will be appended with timestamps as new information emerges.