Executive Overview
Federal Bureau of Investigation (FBI) agents have apprehended a high-ranking executive from a prominent Canadian cybersecurity firm in connection with a sprawling, high-priority federal investigation into the ShinyHunters cybercrime syndicate. The arrest marks a dramatic escalation in an ongoing international crackdown against the elite hacking collective, which recently targeted the FBI itself, absconding with sensitive personnel and medical records belonging to thousands of federal agents.
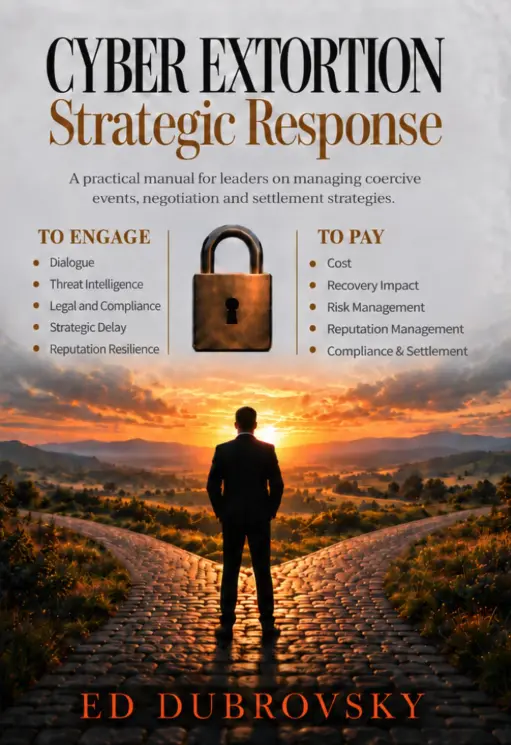
The suspect, identified in federal court records as Edward Dubrovsky (with the surname occasionally spelled Dobrovsky), was taken into custody in Pennsylvania while attending a prominent cyber insurance and risk management conference. Dubrovsky is a recognized figure in the digital defense community, a specialist in ransomware negotiations, and the author of the text Cyber Extortion Strategic Response.
According to sources familiar with the matter, federal investigators are probing whether certain corporate intermediaries operating within the booming cyber-extortion negotiation sector crossed legal boundaries, transitioning from authorized advisors and negotiators into co-conspirators who allegedly assisted malicious actors in laundering illicit proceeds or facilitating extortion schemes.
The arrest underscores a turbulent period for the Bureau, which has faced immense public scrutiny following audacious retaliatory data breaches orchestrated by ShinyHunters. As the investigation’s focal point shifts to federal courts in Texas, cybersecurity professionals and legal experts alike are watching closely to see how far the fallout from this operation will extend across the global cyber-incident response industry.
Detailed Chronology of the Pennsylvania Arrest and Judicial Shift
The sequence of events leading to Edward Dubrovsky’s arrest unfolded rapidly during the first week of October during the annual Cyber Risk Summit held at the Loews Philadelphia Hotel between October 5 and October 7. The conference, organized by NetDiligence, drew hundreds of cyber insurance brokers, legal counsel, risk managers, and threat-response executives from across North America.
Among the primary sponsors of the event was CyberSteward, a Canadian cybersecurity venture with which Dubrovsky has been closely associated. According to a professional announcement posted to LinkedIn roughly a month prior to the summit, Dubrovsky stated his intention to attend the Philadelphia event alongside his team to discuss global strategies around coercive cyber extortion response, negotiations, and compliant settlement services.
Federal court dockets reveal that on October 8—just one day after the conclusion of the summit—a federal complaint was unsealed charging Dubrovsky with serious criminal counts, including “conspiracy to threaten to impair the confidentiality of information with the intent to extort money” and “interference with commerce by threats.”
Initially logged into a federal holding facility in Philadelphia under the U.S. Bureau of Prisons inmate management system, Dubrovsky’s legal file underwent an immediate administrative relocation. On October 9, federal authorities filed a transfer notice moving the case jurisdiction to the U.S. District Court for the Eastern District of Texas. Multiple investigative sources confirm that the Eastern District of Texas has become the centralized epicenter for the entire federal docket concerning the ShinyHunters syndicate.
As of reporting, Dubrovsky’s defense counsel remains unassigned, with court records indicating he has yet to retain private representation or be appointed a federal public defender. Representatives for CyberSteward and its predecessor firms have navigated complex public relations queries regarding Dubrovsky’s exact historical titles, distancing current operational leadership from the unfolding criminal liabilities.

The ShinyHunters Syndicate: Anatomy of a Global Extortion Enterprise
To understand the weight of the federal charges against Dubrovsky, one must examine the operational footprint of ShinyHunters. Operating with ruthless efficiency, the syndicate has established itself as one of the most prolific and destructive data-extortion enterprises targeting modern enterprise infrastructures.
Modus Operandi
ShinyHunters routinely targets Software-as-a-Service (SaaS) providers, cloud storage architectures, and corporate enterprise databases. Utilizing sophisticated social engineering campaigns, spear-phishing, and credential-stuffing techniques, the group gains unauthorized access to high-privilege corporate accounts. Once inside, they exfiltrate massive volumes of proprietary intellectual property, customer Personally Identifiable Information (PII), and sensitive corporate communications.
The group then leverages strict digital extortion tactics: if victims refuse to pay exorbitant cryptocurrency demands, the stolen databases are leaked publicly on underground cybercrime forums or commercial data-leak sites to inflict maximum reputational and regulatory damage.
The Attack on the FBI
The stakes of the current federal investigation escalated exponentially when ShinyHunters successfully breached an online recruitment portal maintained by the FBI itself. The breach compromised sensitive internal files containing granular data on thousands of federal agents, including their departmental units, specialized skill sets, and—most alarmingly—confidential medical and psychiatric records.
Immediately following subsequent international law enforcement raids, a high-ranking faction leader within ShinyHunters operating under the alias “Rey” assumed operational control of the syndicate. Utilizing stolen law enforcement data, Rey began publicly taunting federal authorities on social media and encrypted communication channels.
International Apprehensions and Law Enforcement Cohesion
The multi-jurisdictional net began tightening around ShinyHunters in late September when Dutch law enforcement authorities successfully apprehended Pepijn van der Stap, a reformed cybercriminal suspected of playing a foundational role in the syndicate’s operations. The seizure of digital hardware during the Dutch raids provided FBI cyber-task forces with a treasure trove of cryptographic evidence, financial trails, and communications logs.
Days after Van der Stap’s capture, international investigative journalism teams—including reports from Reuters—identified the elusive leader "Rey" as a teenager named Saif Al-din Khader. Khader was subsequently detained and began cooperating with federal authorities. Investigations later revealed that Khader and his cell were actively attempting to extort a major navigation and digital aviation unit recently divested by industrial giant Boeing before law enforcement intervened.
Supporting Context & Metrics: The Crisis in Ransomware Intermediaries
The arrest of a prominent cyber-extortion advisor sheds light on a contentious, gray-market sector within the broader cybersecurity ecosystem: ransomware negotiation and incident response firms.
The Financial Scale of Extortion
According to preliminary metrics released by federal law enforcement agencies, the ShinyHunters group alone has successfully extorted over $70 million in cryptocurrency payments from corporate and government victims throughout the calendar year. The massive influx of capital into the digital wallets of cybercriminal syndicates has fueled an industrial-scale underground economy.
The Ethical and Legal Gray Area of Negotiations
In his 252-page professional text, Cyber Extortion Strategic Response, Edward Dubrovsky emphasized the delicate mechanics of dealing with violent digital criminals, writing:

"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
While corporate boards and cyber insurers routinely hire specialized advisory firms to handle threat actors safely, legally navigate regulatory reporting, and protect shareholder value, federal prosecutors are increasingly scrutinizing whether certain operators overstep legal boundaries. Investigators are examining whether specific negotiation firms have facilitated illegal payments to sanctioned entities, engaged in money-laundering channels, or actively colluded with hackers to inflate ransom demands for financial kickbacks.
Official Statements and Industry Reactions
Official communications regarding the ongoing sweep have been closely guarded by the Department of Justice and the executive leadership of the FBI.
Following the initial breaking of the news, FBI Director Kash Patel issued a brief statement via social media addressing the aggressive posture of federal law enforcement against digital extortion networks, though specific names and direct linkages to the Pennsylvania arrest were initially omitted from the public decree.
Corporate responses from the private security sector have been swift and defensive. Following public interest in Dubrovsky’s professional background, a corporate spokesperson for Cypfer—a major Canadian cybersecurity firm and a top sponsor of the Cyber Risk Summit—released a clarifying statement addressing Dubrovsky’s historical ties to the company. The representative disputed claims made on professional networking profiles that Dubrovsky was a foundational co-founder, clarifying instead that he had served as a managing director prior to his resignation in November 2025.
Similarly, executives at CyberSteward—the firm Dubrovsky was representing during his fateful trip to Philadelphia—have maintained a tight-lipped stance, declining immediate comment as corporate legal counsel reviews the scope of the federal indictment.
Future Outlook: What Lies Ahead for the Extortion Response Industry?
The indictment and arrest of Edward Dubrovsky represent a watershed moment for the global cybersecurity and incident-response industry. Several critical developments are expected to unfold in the coming weeks and months:
- Expansion of Indictments: Sources close to the grand jury proceedings indicate that federal prosecutors in the Eastern District of Texas are preparing additional charges against principals and associates at other boutique companies that specialize in ransomware negotiation and alternative dispute resolution.
- Regulatory Scrutiny on Insurance and Advisory Firms: Insurance providers and regulatory bodies (such as the U.S. Department of the Treasury’s Office of Foreign Assets Control) are likely to implement stringent compliance frameworks regarding which negotiation firms can be retained by insured entities, aiming to shut down illicit financial channels.
- Heightened Federal Counter-Cyber Operations: The FBI, smarting from the public humiliation of having its own recruitment and medical portals breached by ShinyHunters, has demonstrated an unrelenting commitment to dismantling the infrastructure supporting modern corporate extortion networks.
As this fast-moving investigative narrative continues to develop, legal scholars and corporate risk officers will be monitoring the Dubrovsky docket closely. The outcome of the trial could fundamentally redefine the legal boundaries of how private corporations, insurance adjusters, and security advisors interact with malicious cybercrime syndicates in the digital age.