Executive Overview
Federal Bureau of Investigation (FBI) agents have arrested a prominent Canadian cybersecurity executive in Pennsylvania, marking a dramatic escalation in an ongoing, high-stakes international investigation into the notorious ShinyHunters cybercrime syndicate. The suspect, identified in federal court records as Edward Dubrovsky—a veteran figure in ransomware advisory and incident response—was taken into custody on October 8, 2026.
The arrest follows a catastrophic breach in which ShinyHunters infiltrated FBI systems, making off with sensitive personnel data—including specialized unit assignments, psychiatric evaluations, and medical histories—concerning thousands of federal agents. The incident has sent shockwaves through the United States intelligence and law enforcement apparatus.
According to multiple sources close to the investigation, Dubrovsky’s arrest ties directly into a sprawling multi-jurisdictional dragnet focusing not only on core hackers but also on intermediaries, negotiators, and firms operating within the shadowy ecosystem of cyber extortion response. While official statements from FBI Director Kash Patel and major media outlets initially reported the detention of a Canadian national in Pennsylvania without naming him, federal court filings and digital footprints quickly unspooled the identity of the executive, who was in the state to attend a prominent cyber insurance and risk conference.
The case has now been centralized within the U.S. District Court for the Eastern District of Texas, signaling that federal prosecutors are preparing a massive, coordinated prosecution against the infrastructure supporting modern ransomware operations. As international law enforcement agencies close in on the actors behind ShinyHunters, the intersection of legal ransomware negotiation and illicit cyber extortion is facing unprecedented federal scrutiny.
Detailed Chronology: From the Cyber Summit to Federal Custody
The Arrest in Pennsylvania
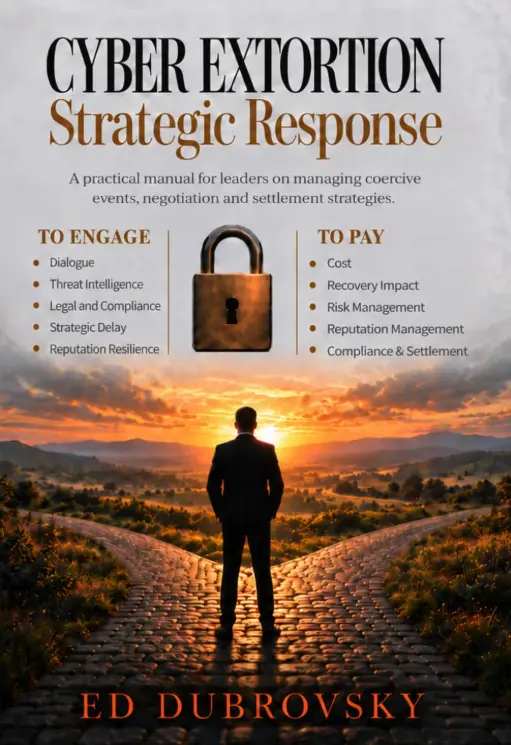
The sequence of events leading to Dubrovsky’s apprehension unfolded during the first week of October 2026 in Philadelphia. Dubrovsky, a 54-year-old security professional and author of the 252-page industry book Cyber Extortion Strategic Response, traveled to Pennsylvania to participate in the annual Cyber Risk Summit held at the Loews Philadelphia Hotel from October 5 to October 7.
The conference, sponsored heavily by top-tier cybersecurity and cyber insurance entities, served as a gathering point for risk managers, insurers, and incident response specialists. Among the primary corporate sponsors was Cypfer, a Canadian cybersecurity firm where Dubrovsky previously held leadership positions, and CyberSteward, a newer venture with which he was recently affiliated.
On October 8—just one day after the summit concluded—FBI agents executed the arrest. Federal court documents filed in Pennsylvania initially recorded the defendant under the slight misspelling "Edward Dobrovsky," charging him with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.

Centralization and Court Actions
Following his apprehension, Dubrovsky was briefly held at a federal detention facility in Philadelphia, according to the U.S. Bureau of Prisons inmate locator. However, the legal mechanics of the case shifted rapidly. On October 9, a formal notice was entered into the court docket transferring the proceedings to the Eastern District of Texas, which sources confirm has become the central command hub for the overarching federal investigation into ShinyHunters.
As of court filings reviewed shortly after his capture, Dubrovsky was unrepresented by legal counsel, with a public defender yet to be formally appointed by the court. Representatives for Cypfer clarified in an updated statement that Dubrovsky was never a founder or co-founder of the firm—despite historical claims on his LinkedIn profile—but rather served as a managing director prior to his resignation in November 2025. Neither Dubrovsky nor representatives from CyberSteward have been immediately reachable for public comment as the legal proceedings accelerate.
The Global Domino Effect
Dubrovsky’s arrest does not occur in a vacuum; it represents the latest domino to fall in an aggressively accelerating international law enforcement campaign against ShinyHunters and their associates:
- Late September 2026: Dutch national police apprehend Pepijn van der Stap, a reformed hacker suspected of playing a pivotal role in the ShinyHunters operation. Investigators immediately begin analyzing seized digital devices for intelligence linking back to broader syndicates.
- Early October 2026: Hot on the heels of Van der Stap’s arrest, a high-ranking ShinyHunters operator operating under the moniker "Rey" assumes control of the group, utilizing the persona to publicly taunt the FBI over the massive internal data breach.
- October 7, 2026: International reporting reveals that "Rey"—subsequently identified as a teenager named Saif Al-din Khader—has been detained by authorities and is actively cooperating with investigators. Khader’s apprehension occurred as the group attempted an extortion campaign against a digital aviation and navigation unit recently spun off from Boeing in late 2025.
- October 8, 2026: Edward Dubrovsky is arrested in Philadelphia, shifting the investigative lens toward the controversial intersection of corporate ransomware negotiation and criminal syndicates.
Supporting Context & Metrics: The Anatomy of ShinyHunters
Modus Operandi and Financial Impact
ShinyHunters has earned a reputation as one of the most destructive and agile cyber extortion rings operating globally. The group typically targets Software-as-a-Service (SaaS) providers and corporate repositories, utilizing advanced phishing campaigns and stolen credential sets to siphon proprietary data from enterprise environments. Once the data is secured, the group issues severe ultimatums: pay a multimillion-dollar ransom demand or watch sensitive intellectual property, customer lists, or internal records leak across public underground forums.
According to metrics released by federal law enforcement agencies, the syndicate’s financial footprint is staggering. In 2026 alone, ShinyHunters has successfully extorted over $70 million from corporate and institutional victims worldwide.
The Breach of the FBI
The tipping point for U.S. law enforcement came when ShinyHunters managed to breach the FBI’s own online recruitment portal. The stolen cache went far beyond routine administrative paperwork, encompassing highly sensitive details regarding federal personnel:
- Specific unit assignments and specialized operational roles.
- Detailed background checks and clearance records.
- Highly sensitive medical and psychiatric evaluations of active agents.
The humiliation of having federal law enforcement personnel compromised by a cybercrime group galvanized leadership at the highest levels of the Department of Justice, resulting in the aggressive, centralized task-force approach now anchored in Texas.

The Fine Line of Ransomware Negotiation
Dubrovsky’s arrest brings to light complex ethical and legal questions surrounding the multi-billion-dollar incident response and cyber insurance industries. In his published work, Cyber Extortion Strategic Response, Dubrovsky explicitly addressed the nuances of communicating with criminal actors:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
While corporate incident response firms routinely utilize these tactical frameworks to manage crises, buy time for forensic teams, and legally navigate regulatory obligations, federal prosecutors are increasingly scrutinizing whether certain intermediaries cross the legal threshold from advisory services into active conspiracy, facilitation, or material support of cyber extortion.
Official Statements and Responses
The federal government has maintained a tightly controlled information flow regarding the specifics of the ongoing prosecution.
- FBI Director Kash Patel: Released a brief statement via X (formerly Twitter acknowledging the apprehension of the Canadian national in Pennsylvania on suspicion of aiding ShinyHunters, though the post omitted specific names due to the ongoing nature of the unsealed filings.
- The Federal Bureau of Investigation: Formally declined to comment on the specifics of Dubrovsky’s indictment or the broader status of the Texas-led task force, citing active and sensitive grand jury proceedings.
- Cypfer Spokesperson: Issued a clarifying statement addressing public records and professional histories, noting that while Dubrovsky served as a managing director until his departure in November 2025, he was never a founder or co-founder of the enterprise.
Future Outlook: Industry Fallout and Regulatory Horizon
The arrest of Edward Dubrovsky is expected to send profound shockwaves through the cybersecurity, cyber insurance, and incident response industries. For years, the boundary between legitimate ransomware negotiation—often sanctioned by insurers to minimize operational downtime and asset loss—and illicit ransom facilitation has remained a regulatory gray zone.
As the Eastern District of Texas takes command of the prosecution, legal scholars and risk management professionals anticipate several key developments:
- Heightened Scrutiny on Negotiators: Incident response firms and independent advisors will likely face rigorous compliance audits regarding how they handle communications, cryptocurrency transactions, and tactical engagements with designated cybercriminal enterprises.
- Expansion of Federal Indictments: Sources familiar with the investigation indicate that charges against principals at other security and negotiation entities could be forthcoming as federal investigators comb through devices seized from recent European and domestic arrests.
- Stricter Policy Frameworks: Insurance carriers may soon be forced to re-evaluate policies covering extortion payments, potentially leading to tighter integration with law enforcement notification mandates before any corporate dialogue with threat actors begins.
As this fast-moving story continues to develop, the outcome of the federal case against Dubrovsky will likely establish a critical legal precedent defining the boundaries of corporate crisis management in an era where cyber extortion syndicates routinely target the highest levels of national security.