Executive Overview
In a decisive move targeting the financial architecture supporting Russia’s wartime operations, the United Kingdom has levied sweeping economic sanctions against Cryptomus, a highly adaptable and illicit cryptocurrency payment processor. Long flagged by blockchain analytics firms and cybersecurity investigators as a premier conduit for ransomware payouts, darknet narcotics markets, and state-sanctioned financial evasion, Cryptomus has operated as a critical financial lifeline helping Moscow bypass international sanctions.
The U.K. Foreign, Commonwealth & Development Office action, formally enacted on October 8, freezes all domestic assets tied to Cryptomus and legally bars British entities, institutions, and individuals from engaging in any commercial or virtual transactions with the platform. Alongside Cryptomus, the U.K. government targeted a cluster of associated virtual payment conduits, including VexPay, TokenSpot, and the Tsunami Payments service.
Industry experts view the British intervention as a watershed moment in international cryptocurrency enforcement. Unlike previous civil monetary penalties—such as a record-shattering CAD $176 million fine issued by Canada that ultimately proved uncollectible—economic sanctions possess the legal teeth required to severely disrupt, if not entirely dismantle, operational payment infrastructure. Furthermore, the sanctions mark a historic precedent: the first known instance of a "Five Eyes" intelligence-sharing nation (Australia, Canada, New Zealand, the United Kingdom, and the United States) directly sanctioning a virtual asset operation incorporated within another Five Eyes jurisdiction.
Detailed Chronology of an Illicit Empire
The Genesis and Evolution of Certa Payments
Cryptomus’s journey into the dark underbelly of cybercrime began quietly in 2022 under its original corporate banners, Certa Payments and Xeltox Enterprises. While presenting itself to the public as a standard, high-efficiency payment gateway for digital commerce, the platform immediately positioned itself as a haven for illicit actors.
By late 2024, investigative reports—most notably from Krebs on Security—exposed Cryptomus as the foundational payment processor underpinning dozens of Russian cryptocurrency exchanges and underground marketplaces hawking malware-as-a-service, stolen credentials, and hacking tools. Behind its slick user interface lay an intricate web of shell companies and false identities. Investigators discovered that the sole shareholder of Certa Payments was a 25-year-old Ukrainian national. Concurrently, she directed several other dubious enterprises, including the WS Management and Advisory Corporation.
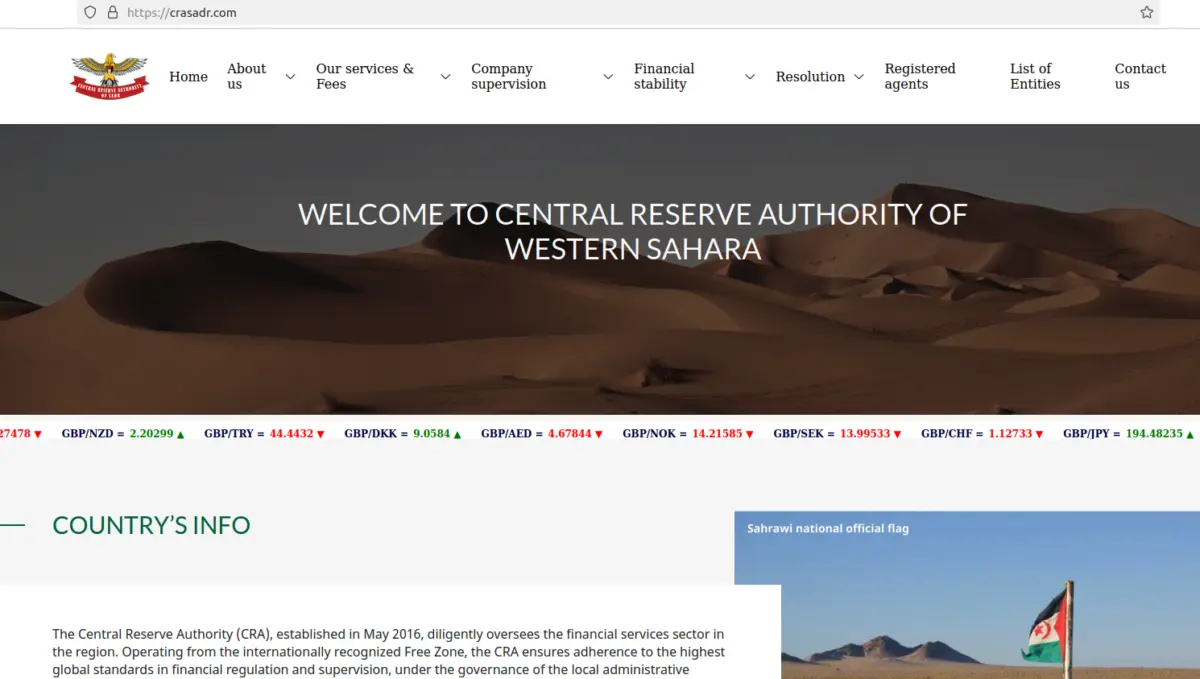
This corporation acted as a faux-regulatory body purportedly overseeing licenses for cryptocurrency, forex, and online gambling businesses incorporated in the disputed northwest African territory of Western Sahara. Operating via domains like crasadr.com—the self-proclaimed Central Reserve Authority of the Western Sahara—the network manufactured fraudulent legitimacy, providing shell companies with the superficial appearance of legal compliance while they funneled billions in illicit funds.
The Canadian Fine and the Birth of "Heleket"
As transaction volumes ballooned, the platform attracted intense scrutiny from global regulators. In October 2025, Canadian authorities brought the hammer down, levying a staggering CAD $176 million administrative monetary penalty against Cryptomus for egregious violations of anti-money laundering (AML) and know-your-customer (KYC) regulations.
Faced with mounting pressure and billions in historical transaction volume, Cryptomus executed a classic chameleonic maneuver. Rather than folding or paying the fine, the platform appealed the penalty while simultaneously launching a parallel, no-KYC processing service dubbed Heleket. While initial KYC implementations caused a temporary dip in Cryptomus’s transaction metrics, Heleket seamlessly absorbed the overflow of unregulated, high-risk capital, ensuring that ransomware gangs, human traffickers, and Russian sanctions-evaders experienced zero downtime.

The U.K. Intercession
By mid-2026, the cumulative threat posed by Cryptomus and its spin-off infrastructure prompted direct intervention from London. The October 8, 2026 sanctions shattered the illusion of operational impunity. Within hours of the announcement, user-facing infrastructure—such as Telegram support bots for both Cryptomus and Heleket—began issuing frantic error messages, confirming that the platform was suddenly paralyzed and unable to process transactions or communicate effectively with its user base.
Supporting Context & Metrics: The Scale of the Enterprise
To fully grasp why Western intelligence and blockchain analytics firms prioritized Cryptomus, one must examine the staggering volume of illicit capital the platform processed.
According to data compiled by blockchain forensics leader TRM Labs in April 2026, Cryptomus handled upwards of $7 billion in transactions from its inception in 2022 through early 2026. This massive volume was not limited to traditional financial crimes; TRM Labs’ tracing identified funds linked directly to vendors of child sexual abuse material (CSAM), international terrorist financing networks, and large-scale human trafficking rings.
Chainalysis, another prominent blockchain intelligence firm, emphasized that Cryptomus and its iterations effectively dwarfed traditional obfuscation tools. In an October 8, 2026 analytical brief, Chainalysis noted:
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity. Together, these services received more illicit funds across tracked categories than the mixers in our dataset, and the number of illicit counterparties surged to more than 900 in a single month in late 2025."
The platform’s business model relied on acting as a bridge between western digital assets and cash liquidity inside Russian financial institutions. As detailed in cross-border financial investigations, Cryptomus routinely converted cryptocurrency extortion proceeds—extorted via ransomware strains deployed against Western critical infrastructure, hospitals, and municipal governments—into clean fiat currency accessible within the Russian banking ecosystem. This mechanism directly supported the Kremlin’s broader economic resilience in the face of international wartime sanctions.
Official Statements and Analyst Perspectives
The international enforcement community has universally lauded the U.K. sanctions, drawing a sharp distinction between symbolic civil monetary penalties and kinetic economic restrictions.
Richard Sanders, a veteran blockchain investigator who spent months mapping out Cryptomus’s labyrinthine payment infrastructure and interacting directly with its illicit customer base, underscored the necessity of moving beyond fines.

"A fine doesn’t stop a cryptocurrency payment processor from processing payments," Sanders wrote in a public analysis following the announcement. "Sanctions kill the operation. The distinction matters."
Sanders pointed out the unique jurisdictional hurdles that previously allowed Cryptomus to thrive. Because the platform originally established roots within a "Five Eyes" partner country (Canada)—sharing a nominal Vancouver office suite with dozens of other phantom money-transfer businesses—law enforcement faced bureaucratic gridlock. Canada’s record fine, while notable in size, lacked the global enforcement mechanisms required to freeze decentralized crypto-node infrastructure. By contrast, U.K. financial sanctions carry extraterritorial weight, threatening secondary sanctions and severe criminal penalties for any global entity caught interacting with Cryptomus’s remaining liquidity pools.
Furthermore, Chainalysis and TRM Labs highlighted that the takedown of Cryptomus validates the evolving maturity of blockchain forensics. Modern cryptographic investigators no longer merely track individual wallet addresses; they map corporate shell networks, regulatory fictions, and Telegram-based customer support chains that unmask the human actors steering these criminal enterprises.
Future Outlook: The Death of Chameleonic Crypto Platforms?
The implementation of U.K. sanctions against Cryptomus, Heleket, TokenSpot, and VexPay signals a paradigm shift in how Western governments intend to police the intersection of cryptocurrency and state-sponsored geopolitical conflict.
As regulatory compliance tightens across traditional jurisdictions, illicit payment processors have increasingly relied on "chameleonic" corporate strategies—rapidly rebranding, shifting domains, spinning off no-KYC sister services (like Heleket), and fabricating regulatory bodies in unrecognized territories (such as Western Sahara). However, the swift crippling of Cryptomus’s Telegram support bots and the freezing of its associated institutional touchpoints demonstrate that these tactics have an expiration date.
Moving forward, cybersecurity analysts expect international law enforcement to expand collaborative targeting against remaining Eastern European and offshore payment gateways that facilitate Russian sanctions evasion. While decentralized networks and privacy-enhancing technologies will continue to attract rogue actors, the destruction of centralized, high-volume fiat-to-crypto bridges like Cryptomus deals a severe, compounding blow to the operational capabilities of global cybercrime syndicates and the wartime economy of the Russian state.