Executive Overview
In a landmark collaborative operation between industry giants and cybersecurity researchers, Google announced today that it has successfully dismantled a massive, highly sophisticated botnet comprising more than 1.3 million compromised Android TV set-top boxes. The malicious infrastructure—anchored by a core component dubbed “XCPE”—secretly co-opted unsuspecting consumers’ residential internet connections, turning everyday streaming hardware into silent proxies for cybercriminals to conduct advertising fraud, launch distributed attacks, and route anonymous web traffic.
According to findings released by the Google Threat Intelligence Group (GTIG), the botnet’s creation was traced back to Videostrong Technology Co., a Chinese hardware manufacturer that systematically embedded backdoor malware directly into the firmware of its Android-based devices. The infection routine executed automatically the moment a user booted up their device for the first time.
Cybersecurity experts involved in the takedown estimate that this enforcement action has severed the botnet’s downstream access to upwards of 10 million additional compromised Internet of Things (IoT) devices. The sweeping contagion extended far beyond standard living-room streaming boxes, infecting specialized hardware such as telehealth terminals, karaoke machines, and digital signage displays.
By taking legal action to seize command-and-control (C2) domains and severing ties with offending manufacturers, Google and its partners have landed a historic blow against the illicit monetization of residential proxies. However, the operation has also cast a harsh spotlight on the murky supply chains of cheap smart-home hardware, the vulnerabilities of automated software development kits (SDKs), and the powerful role that social media influencers play in unwittingly marketing compromised tech to millions.
Detailed Chronology: Unraveling the XCPE Operation
The dismantling of the XCPE botnet is the culmination of months of meticulous cross-industry investigations, tracking how cheap, factory-infected streaming boxes managed to infiltrate global households undetected.
The Foundation of a Threat: Factory-Level Backdoors
For years, budget-friendly Android TV set-top boxes have flooded global markets, offering consumers thousands of channels and streaming libraries for a low, one-time fee. Unbeknownst to buyers, manufacturers like Videostrong Technology Co. leveraged these devices as Trojan horses. Google’s rigorous compatibility and security testing standards were bypassed by Videostrong, which managed to deploy its malicious payload during the initial device boot sequence.
Once active, the XCPE malware established continuous contact with external control servers. It converted the host devices into residential proxy exit nodes, quietly routing third-party web traffic through the user’s home network. Videostrong commercialized this access by selling the backdoors to a variety of criminal affiliates, who loaded additional malicious modules onto the boxes.
Industry Discovery and the Role of Startups
The unraveling of the XCPE infrastructure accelerated significantly over the course of 2026. In January 2026, security startup Synthient published landmark research detailing the rapid proliferation of the Kimwolf botnet, which had been hammering global networks with record-breaking Distributed Denial-of-Service (DDoS) attacks. Synthient’s analysis exposed how Kimwolf infected millions of Android set-top boxes virtually overnight, exploiting vulnerabilities in residential proxy networks to pivot and compromise other connected IoT devices on local residential subnets.
The resulting industry pressure forced numerous residential proxy networks to patch their systems, fracturing Kimwolf into smaller, manageable fragments. This breakthrough attracted the attention of the Motion Picture Association (MPA), representing major Hollywood studios. The MPA partnered with Synthient to physically acquire and reverse-engineer popular Android TV boxes, laying the groundwork for the ultimate exposure of Videostrong and its network of partners.
The Coordinated Takedown
Armed with intelligence from Synthient, Plume Security Labs, Black Lotus Labs, TrendAI, and other cybersecurity entities, Google moved aggressively. GTIG severed commercial and ecosystem relationships with Videostrong and executed legal takedowns targeting the infrastructure and domains used to manage the botnet.
Simultaneously, researchers identified other major brands tied to the same supply chain. In a comprehensive report published today, Synthient examined popular pre-infected TV boxes sold under the MECOOL brand by the publicly traded Chinese company Skyworth Technology. The report concluded that MECOOL boxes also bundled Videostrong’s malware, alongside integrated components from prominent residential proxy networks.

Supporting Context & Metrics: The Mechanics of Residential Proxies
To fully grasp the magnitude of the XCPE threat, one must understand the booming economy of residential proxy services. While legitimate proxy networks serve valid commercial purposes—such as web scraping, ad verification, and market research—a sprawling dark market has weaponized these services to mask illicit digital activities.
The Profit Motive of Proxy Monetization
Residential proxies allow paying customers to route their internet traffic through genuine home IP addresses, making their actions appear as ordinary residential users rather than automated data scrapers or malicious actors. This anonymity is highly prized for:
- Account Takeover (ATO) Attacks: Bypassing security controls by staging login attempts from trusted residential IPs.
- Advertising Fraud: Generating artificial impressions and clicks on digital ads to siphon revenue.
- Mass Content Scraping: Harvesting data for large language models (LLMs) and AI training projects without authorization.
The GTIG report and concurrent independent investigations highlighted a web of residential proxy providers whose Software Development Kits (SDKs) were frequently discovered inside devices infected by the XCPE botnet. These included:
- AppSalt / Honeygain: Developed by Oxylabs (Vilnius, Lithuania), which recently reorganized under an umbrella entity named Source following a $130 million funding round from Warburg Pincus valuing the business at $3.6 billion.
- NetNut: Operated by Alarum Technologies, a publicly traded Israeli firm. (In July 2026, the FBI seized hundreds of domains linked to NetNut for running a separate TV-box proxy botnet known as Popa).
- Other Noted Providers: EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, GaGaNode, and Grass.
Scale of the Infection
While Google formally confirmed the direct dismantling of 1.3 million active Android TV boxes tied to the XCPE core, experts emphasize that this figure is merely the tip of the iceberg.
Ben Brundage, founder of Synthient, described the 1.3 million figure as "highly conservative."
"The scale of affected devices is likely way higher," Brundage noted in an interview with KrebsOnSecurity. "This is probably the largest operation against backdoored TV boxes that we’ve seen."
Because Videostrong’s affiliates maintained diversified distribution channels outside of XCPE, the total downstream footprint of compromised systems—including secondary IoT devices on home networks—is estimated to exceed 10 million units globally.
Official Statements and Industry Accountability
The fallout from the XCPE takedown has forced proxy providers and hardware distributors to address how backdoors slip into consumer electronics.
Google’s Stance
In its official advisory, the Google Threat Intelligence Group condemned the actions of the hardware manufacturers, stating:
"A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors."
Oxylabs Responds
Following initial publication of the findings, Oxylabs issued a formal statement addressing the integration of its SDKs within backdoored firmware. The company asserted that its architecture is explicitly designed to require explicit user consent before a device can operate as a proxy exit node. However, investigators discovered that rogue developers had successfully faked these consent signals.

"We have been conducting regular audits of the applications provided by our partners," Oxylabs stated. "However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application."
Oxylabs clarified that it had no direct corporate record of Videostrong Technology Co., but identified a malicious external malware loader domain (com.abc[.]nexus) mentioned in the GTIG report among its suppliers.
"As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry. This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves."
The Role of Social Media: Influencers and the Pipeline of Deception
One of the most concerning revelations of the XCPE investigation is how these compromised devices successfully penetrate consumer homes on a mass scale. Rather than relying solely on traditional retail channels, brands like Superbox and MECOOL capitalized on digital word-of-mouth through social media platforms like TikTok and YouTube.
Influencers frequently praised these budget boxes for offering hundreds of premium pay-TV channels and streaming services for a single, low fee—an appealing pitch that often masks copyright infringement and pirated content.
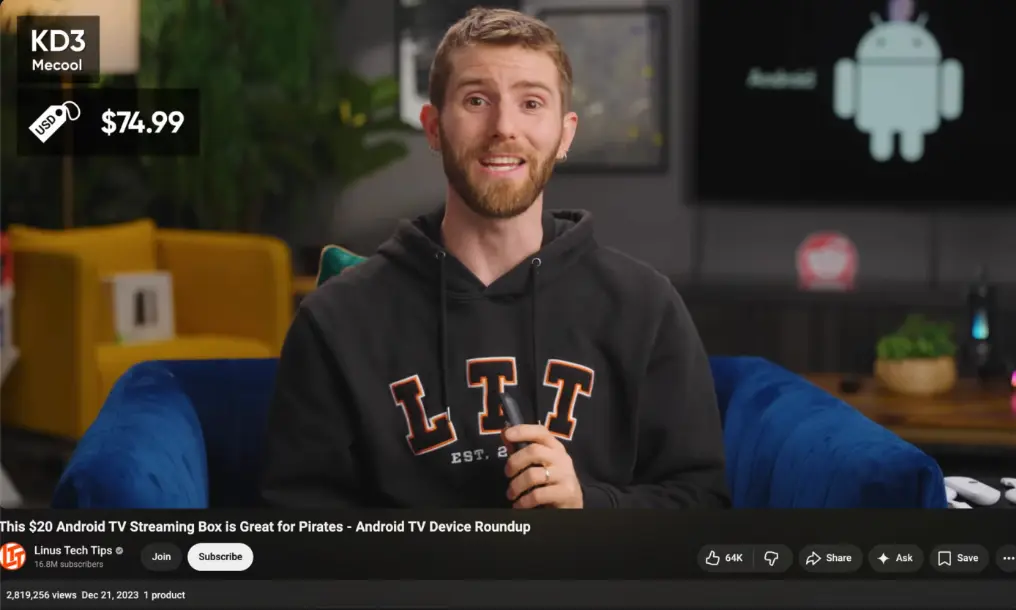
For instance, MECOOL set-top boxes experienced an explosive surge in sales following a 2023 feature on the prominent YouTube channel Linus Tech Tips, which boasts nearly 17 million subscribers. Following disclosures by security researchers, Linus Tech Tips updated its historical coverage to explicitly frame the product as a security risk and scam, purging all associated affiliate links from its channel.
Similarly, researchers from Censys previously uncovered that Superbox streaming devices bundled residential proxy software from providers like Grass, though the proxy operators consistently denied direct affiliations with the hardware vendors.
Future Outlook: Securing the IoT Ecosystem
The dismantling of the XCPE botnet marks a monumental victory for cybersecurity defenders, but it also exposes persistent structural vulnerabilities in global hardware supply chains. When trust is fundamentally compromised at the manufacturing level—before a device even reaches retail shelves—traditional endpoint security tools deployed by end-users are largely powerless.
Moving forward, industry experts recommend several critical safeguards:
- Stricter Supply Chain Audits: Major operating system developers like Google must implement cryptographic verification steps to ensure that firmware modifications cannot be silently introduced post-compilation.
- Proxy SDK Vetting: Residential proxy networks must face stricter regulatory and technical oversight, specifically regarding how third-party SDKs are integrated into consumer applications and hardware.
- Consumer Awareness: Buyers should remain deeply skeptical of ultra-cheap streaming hardware promising unlimited premium content for a one-time fee, as these devices often exact a heavy toll on personal network security and bandwidth.
As collaborative intelligence-sharing continues between tech titans, startups, and law enforcement agencies, the takedown of XCPE serves as both a blueprint for future botnet disruptions and a sobering reminder of the hidden costs embedded in the modern Internet of Things.