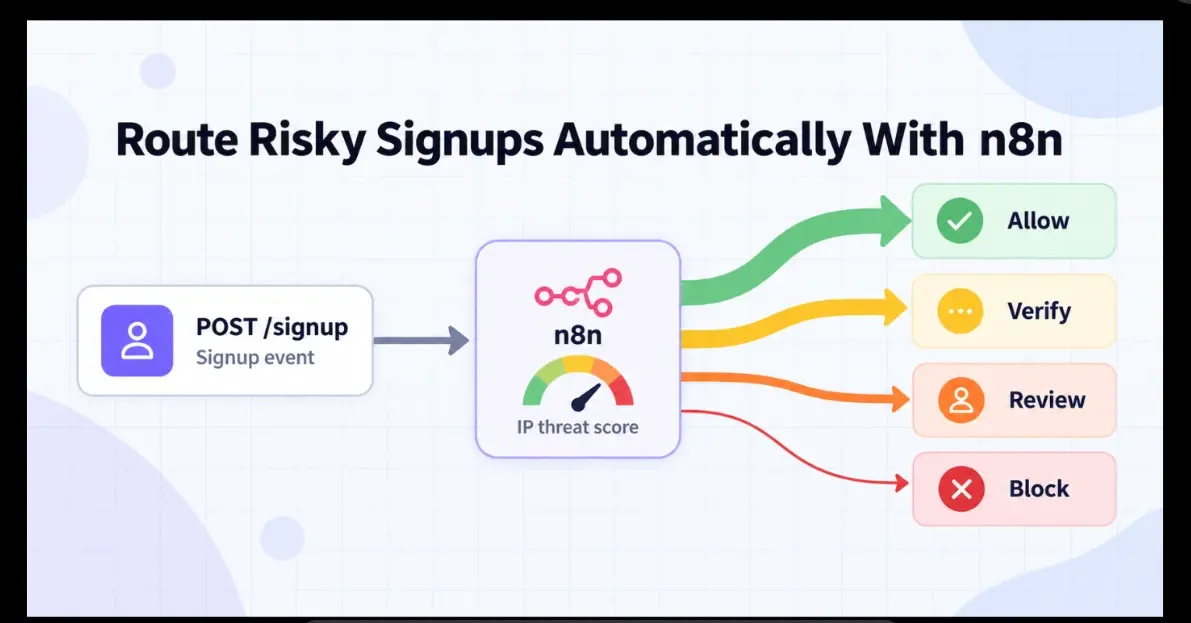
Executive Overview
In the realm of automated user onboarding and digital security, convenience is frequently the primary vector for exploitation. Platforms that streamline user registration via workflow automation tools like n8n often fall victim to a deceptively simple architectural trap: the binary evaluation node.
A standard setup typically reduces signup security to a single logical question on a visual canvas: If the incoming IP address indicates a Virtual Private Network (is_vpn), block the request.
While this approach appears intuitive and yields a clean visual workflow, it fundamentally misunderstands the nuance of modern IP intelligence. In practice, this binary approach fails in both directions with alarming frequency. It aggressively blocks legitimate B2B buyers whose corporate security infrastructure routes all workforce traffic through standardized enterprise gateways. Simultaneously, it completely misses modern privacy relays like iCloud Private Relay, and it routinely waves through sophisticated residential proxies that happen to bypass basic VPN classifications.
The root of the issue is not a shortage of data points, but a failure of logic. A single boolean flag tells an automation engine what an IP address is, but it fails to dictate what the system should do.
Building a robust, enterprise-grade signup security pipeline requires shifting away from primitive pass/fail conditions. Instead, engineers must adopt a multi-tiered scoring matrix backed by granular contextual signals—such as confidence scores, corporate gateway overrides, and bot categorization parameters. This architectural blueprint examines how to construct a resilient, four-branch evaluation workflow in n8n that eliminates false positives, respects legitimate enterprise traffic, and maintains a deterministic, auditable path for security decisions.
Detailed Chronology: The Evolution and Failure of Binary Fraud Detection
To understand why contemporary fraud detection workflows fail, one must trace the evolution of perimeter defense tools. Early web security operated on a rudimentary binary ledger: "good" residential IPs versus "bad" datacenter ranges. As commercial VPN services proliferated, security engineers introduced simple boolean filters to detect and block known VPN exit nodes.
However, the internet’s routing architecture evolved much faster than these static heuristics.
The Corporate Gateway Blind Spot
As remote and hybrid workforces expanded, major enterprises centralized their network security. Organizations increasingly route all employee web traffic through Secure Web Gateways (SWGs) managed by providers like Zscaler or Netskope.
When an enterprise employee evaluates a B2B SaaS platform from inside their corporate network, their request originates from a concentrated handful of enterprise egress IPs. Consider an IP address such as 87.58.66.106: it registers a low threat score of 5, carries an is_corporate_gateway: true flag, and identifies its provider as Zscaler. Crucially, its is_anonymous property remains false.
A naive is_vpn check frequently flags or drops this traffic because it mimics the shared-infrastructure footprint of consumer privacy tools. In reality, blocking this IP does not stop a malicious actor; it successfully locks out a prospective corporate buyer.
The Privacy Relay Loophole
Simultaneously, major consumer technology ecosystems have integrated native privacy routing into their operating systems. Services like iCloud Private Relay and Cloudflare WARP do not categorize their traffic under traditional VPN parameters. Instead, they trigger the is_relay flag.
An n8n workflow engineered solely around is_vpn remains completely blind to these requests. While catching privacy relays might seem desirable from a strict paranoia standpoint, doing so automatically alienates millions of mainstream iOS and consumer software users who never consciously opted into specialized anonymization tooling.
The Residential Proxy Threat
Conversely, advanced threat actors leverage residential proxies to bypass legacy datacenter filters. An address such as 145.223.7.7 may register on an Autonomous System Number (ASN) legally registered to a standard Internet Service Provider.
Under a superficial datacenter-range check, this IP sails straight through unhindered. A dedicated is_vpn check might catch it—if and only if the specific proxy provider also operates a commercial VPN service. However, if the underlying network is exclusively a residential proxy network linked to multiple scrapers, spam sources, and known attacker databases, it can easily command a severe threat score of 90 while slipping past single-variable filters.
Supporting Context & Metrics: Deconstructing the IP Security Object
To build an effective routing matrix, developers must stop relying on trimmed payloads and instead ingest and parse comprehensive IP security telemetry. A production-grade security object contains dozens of discrete fields, each offering critical context for risk assessment.
  "ip": "145.223.7.7",
  "security":
    "threat_score": 90,
    "is_tor": false,
    "is_proxy": true,
    "proxy_provider_names": ["NetNut", "ProxyScrape", "Oxy Labs", "DataImpulse"],
    "proxy_confidence_score": 99,
    "proxy_last_seen": "2026-09-01",
    "is_residential_proxy": true,
    "is_vpn": true,
    "vpn_provider_names": ["SurfShark VPN", "Ishaan VPN"],
    "vpn_confidence_score": 99,
    "vpn_last_seen": "2026-07-31",
    "is_relay": false,
    "relay_provider_name": "",
    "is_anonymous": true,
    "is_known_attacker": true,
    "is_bot": false,
    "bot_confidence_score": 0,
    "bot_operator_name": "",
    "bot_type": "",
    "is_known_good_bot": false,
    "bot_last_seen": "",
    "is_spam": true,
    "is_cloud_provider": true,
    "cloud_provider_name": "Brander Group Inc.",
    "is_corporate_gateway": false,
    "corporate_gateway_type": "",
    "corporate_gateway_provider_name": ""
Critical Signals That Shape Workflow Architecture
- Confidence Scores: Independent metrics such as
proxy_confidence_scoreandvpn_confidence_scoregrade detection accuracy on a scale from 0 to 100. A high-confidence detection (e.g., 99) corroborated by recent network observations commands a much stronger response than a low-confidence flag. This distinction dictates whether an automated system should introduce minor friction—such as a One-Time Password (OTP)—or execute a hard system block. - Contextual Override Flags: The
is_corporate_gatewayandis_relayproperties serve as crucial overrides. Corporate gateways represent identifiable, authenticated enterprise architectures rather than anonymous threat vectors. Relays represent consumer privacy utilities. Neither should trigger an automatic block based solely on their existence. They must be evaluated after checking explicit attacker indicators to prevent unnecessary user friction. - Granular Bot Classification: A binary
is_botflag treats benevolent indexing engines (like Googlebot) identically to aggressive credential-stuffing scripts. Utilizing thebot_typefield—which distinguishes betweensearch_engine,ai_crawler,scraper,brute_force, andcredential_stuffing—allows security engineers to seamlessly permit authorized automated tools while dropping malicious actors.
The Four-Tier Routing Matrix
Rather than executing a binary block, enterprise security architectures map threat scores to standardized operational bands:
| Threat Score Band | Published Guidance | Workflow Branch | Practical Execution |
|---|---|---|---|
| 1–19 | Allow with standard controls | Allow | Provision the account immediately; log telemetry. |
| 20–44 | Combine with auxiliary signals | Verify | Require email address verification prior to primary access. |
| 45–79 | Introduce risk friction | Review | Create account in a flagged status; hold trial resources. |
| 80–100 | Block or issue hard challenge | Block | Reject registration, trigger security alerts, log audit trail. |
Architectural Implementation: Building the n8n Workflow
Designing this architecture inside n8n requires careful attention to data flow, error handling, and API integration.
1. Capturing the Client IP App-Side
An architectural anti-pattern is attempting to determine a user’s true IP address from inside the n8n webhook node. Behind standard load balancers, reverse proxies, or CDNs, the incoming request IP will map to the proxy layer rather than the end-user device.
Applications must capture the client’s true IP address within their own backend infrastructure—respecting trusted proxy headers—and pass it explicitly within the webhook payload as $json.body.ip .
2. Integrating the IP Security Lookup
Within the n8n node panel, teams can integrate verified security lookup integrations (such as IPGeolocation, Greip, AbuseIPDB, or MaxMind). Using the Get IP Security action, engineers submit the client IP.
While free geolocation tiers provide basic ASN data, comprehensive threat scoring, provider name resolution, and confidence metrics require security-tier API access. This unified approach eliminates the need for multiple cascading API calls.
3. Implementing the Override Layer
Before passing the threat score into a switch node, developers must insert an intermediary IF node evaluating explicit override conditions:
$json.security.is_corporate_gateway == true OR $json.security.is_relay == true- True Output: Routes directly to the Allow branch. This explicitly relaxes per-IP rate limits and disables IP-based deduplication keys, ensuring that dozens of legitimate employees sharing a corporate gateway are not falsely flagged as a distributed botnet attack.
- False Output: Proceeds downstream to the core evaluation switch.
4. Configuring the Switch Node
Downstream from the override filter, configure a Switch node operating in Rules mode with four distinct numerical outputs tied to $json.security.threat_score :
- Output 1 (Allow): Score
< 20 - Output 2 (Verify): Score
20to44 - Output 3 (Review): Score
45to79 - Output 4 (Block): Score
≥ 80
Crucially, define a reliable fallback output pointing directly to the Verify branch. If an API outage or malformed payload returns an unexpected or missing score, forcing a user through an email verification step represents an acceptable operational friction point, whereas silently approving an unscored request introduces severe security vulnerability.
Official Industry Perspectives & Expert Warnings
Industry veterans emphasize that automated fraud engineering requires strict determinism. A common architectural pitfall is offloading core security decisions to Large Language Models (LLMs).
While modern automation platforms prominently feature LLM nodes, routing raw threat telemetry to a generative model to "assess risk" introduces unacceptable non-determinism, significant latency, and unpredictable API costs. Furthermore, it completely destroys enterprise auditability. When a legitimate customer inquires why their corporate signup was rejected, "an artificial intelligence model calculated high risk" fails to satisfy regulatory compliance standards or basic customer support requirements.
Core Principle: Score deterministically. Branch deterministically. Reserve generative artificial intelligence strictly for secondary tasks, such as translating technical security telemetry into plain-English Slack notifications for on-call security teams.
Handling Infrastructure Failures (Fail-Open vs. Fail-Closed)
External API dependencies inevitably experience downtime. Configuring the node’s On Error settings requires a strategic policy decision based on business context:
- For Signups and Registrations: Fail open. Route connection errors to the verification queue and log the event. An unreachable scoring provider should never completely halt customer acquisition.
- For Financial Transactions and Payouts: Fail closed. Hold payment and transfer operations for manual review. In financial workflows, the cost of processing an unscored transaction drastically outweighs the temporary friction of delayed processing.
Future Outlook
As automated fraud vectors become increasingly sophisticated—leveraging generative AI scripts, rotating residential proxy pools, and automated device fingerprint spoofing—static security rules will become entirely obsolete.
The future of signup fraud protection lies in adaptive, multi-signal telemetry pipelines that combine IP intelligence with behavioral biometrics, device posture analysis, and cryptographic identity attestation. However, the foundational lesson remains immutable: security automation is only as effective as its orchestration logic. By abandoning naive binary checks in favor of nuanced, context-aware routing matrices, organizations can successfully balance impenetrable perimeter defense with frictionless user acquisition.