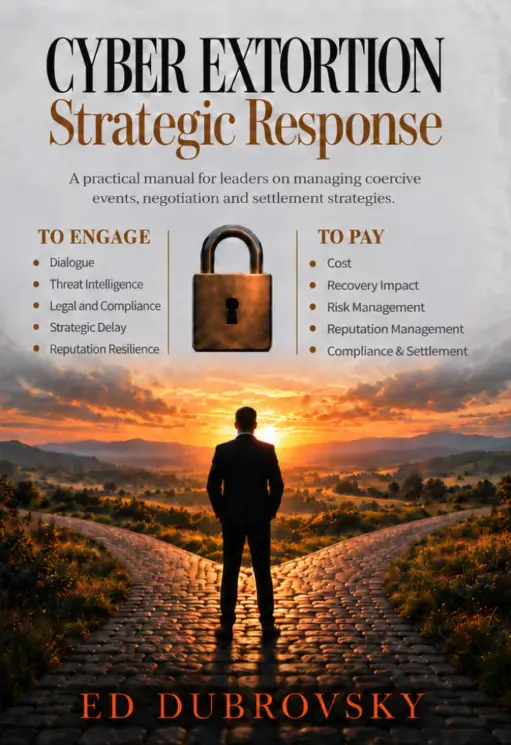
In a stunning escalation of a high-stakes cyber warfare saga, federal law enforcement agents have arrested a prominent Canadian cybersecurity executive in connection with the notorious ShinyHunters cybercrime syndicate. The suspect, identified in federal court records as Edward Dubrovsky—a seasoned threat response expert, author, and principal at the Canadian security firm CyberSteward—was apprehended in Pennsylvania while attending a prominent industry conference.
The arrest marks a dramatic intersection between the formal cybersecurity incident-response industry and the shadowy underworld of cyber extortion. According to multiple sources close to the investigation, Dubrovsky’s detention is directly tied to a sprawling, centralized federal probe into ShinyHunters, a gang responsible for extorting more than $70 million from corporate and government victims in 2026 alone.
Most damagingly, the syndicate recently humiliated federal law enforcement by breaching an online FBI recruitment portal, exfiltrating sensitive data—including unit specializations, operational assignments, and even confidential medical and psychiatric records—pertaining to thousands of federal agents.
As the investigation shifts its epicenter to a federal field office in Texas, the fallout from Dubrovsky’s arrest threatens to send shockwaves through the lucrative, often opaque ecosystem of ransomware negotiation and digital extortion advisory firms. With federal prosecutors unsealing charges that accuse the executive of cyber extortion and conspiracy, this developing case blurs the line between those who defend against ransomware and those who may cross ethical—and legal—boundaries in the pursuit of settlements.
Detailed Chronology: From the Loews Philadelphia Hotel to Federal Custody
The sequence of events leading to Edward Dubrovsky’s arrest highlights the meticulous, cross-border coordination of federal law enforcement agencies tracking the ShinyHunters collective.
The Cyber Risk Summit (October 5 – October 7, 2026)
Dubrovsky traveled to Philadelphia, Pennsylvania, to participate in the annual Cyber Risk Summit, hosted by NetDiligence at the Loews Philadelphia Hotel. Publicly available conference materials indicate that Dubrovsky, representing the Canadian security firm CyberSteward (and formerly associated with prominent ransomware advisory firm Cypfer), was slated to engage in high-level discussions regarding global ransomware strategy, extortion advisory, and compliance-driven settlement negotiations.
Weeks prior to the event, Dubrovsky had taken to LinkedIn to express enthusiasm for the conference panels, writing:
"Looking forward to continuing conversations around strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services that are global and truly agnostic."
Unknown to conference organizers and attendees, federal investigators were closing a net around the cybersecurity veteran.

The Arrest and Initial Court Appearances (October 8 – October 9, 2026)
On October 8, Federal Bureau of Investigation agents moved in, arresting Dubrovsky in Pennsylvania. Federal court documents—some of which remain sealed, though key details were indexed via CourtListener—reveal that the defendant was booked under the slightly misspelled name "Edward Dobrovsky." He faces severe federal counts, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money and interference with commerce by threats.
Following his apprehension, initial inmate locator records from the U.S. Bureau of Prisons placed the 54-year-old executive at a federal holding facility in Philadelphia. However, a rapid legal maneuver on October 9 transferred jurisdiction of the case to the Eastern District of Texas, which sources confirm has now become the nerve center for the overarching multi-agency ShinyHunters investigation.
As of press time, Dubrovsky remains unrepresented in court dockets, with no private defense counsel or public defender formally assigned to his defense.
Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To fully grasp the gravity of Dubrovsky’s arrest, one must examine the operational blueprint and recent escalation of the ShinyHunters threat group, as well as the broader ecosystem of ransomware response.
Modus Operandi and Financial Impact
ShinyHunters has long operated as a sophisticated data-extortion machine. The group typically leverages targeted phishing campaigns, compromised credentials, and vulnerabilities in software-as-a-service (SaaS) provider environments to siphon proprietary databases from corporate giants. Rather than deploying traditional file-encrypting ransomware across endpoints, the syndicate relies on pure exfiltration: threatening to dump sensitive customer data, source code, and internal communications onto public forums unless a lucrative cryptocurrency ransom is paid.
According to federal tracking metrics, ShinyHunters has successfully extorted more than $70 million from global victims throughout 2026.
The FBI Data Breach and the Rise of "Rey"
The intensity of the federal response was catalyzed by an unprecedented operational security failure within the Bureau itself. Following the September 2026 Dutch police arrest of reformed-turned-active hacker Pepijn van der Stap—a key figure tied to the ShinyHunters apparatus—the leadership vacuum within the cybercriminal group was swiftly filled by an operative known online as "Rey."
Stepping into the commander’s seat, Rey began taunting federal authorities. The group successfully breached an online FBI recruitment portal, stealing dossiers containing sensitive personal and professional data of thousands of agents, including psychiatric evaluations, medical histories, and specific unit assignments.
Subsequent international journalistic and law enforcement efforts quickly unmasked "Rey" as a teenager named Saif Al-din Khader. Khader was swiftly detained and is reportedly cooperating with federal investigators. His apprehension came on the heels of an attempted extortion campaign targeting a digital aviation and navigation unit recently divested by aerospace giant Boeing in late 2025.

The Insider Dilemma: Ransomware Advisory Firms Under Scrutiny
The arrest of a high-profile ransomware negotiator introduces a deeply unsettling narrative to the cybersecurity sector. Firms specializing in cyber extortion negotiations often walk a tightrope between lawful incident response and facilitating illicit transactions with sanctioned threat actors.
Dubrovsky himself literally wrote the manual on the subject, authoring the 252-page volume Cyber Extortion Strategic Response. In promotional material for the book, Dubrovsky emphasized the tactical nuances of handling threat actors:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, investigators are increasingly probing whether certain advisory personnel crossed the boundary from legally permitted crisis management into active criminal collaboration, profit-sharing, or the facilitation of extortion payouts that violate international sanctions.
Official Statements and Industry Reactions
As the news broke, institutional stakeholders scrambled to respond to the implications of an active industry leader sitting in federal custody on extortion charges.
- The Federal Bureau of Investigation: FBI Director Kash Patel acknowledged ongoing operations via social media channels, celebrating international and domestic cooperation, though the Bureau officially declined to comment on the specifics of Dubrovsky’s indictment due to ongoing, unsealed proceedings.
- Cypfer Corporate Response: Following initial reports linking Dubrovsky to Canadian security firm Cypfer, a corporate spokesperson issued a clarifying statement on October 10. The company forcefully distanced itself from the accused executive, clarifying that Dubrovsky was never a founder or co-founder—contrary to claims on his professional profiles—and had merely served as a managing director prior to his resignation in November 2025.
- CyberSteward: Representatives for CyberSteward, the firm Dubrovsky was associated with at the time of his arrest, have not yet released an official statement. Industry peers note that the firm’s leadership is conducting internal reviews regarding its active engagements and conference sponsorships.
Future Outlook: A Turning Point in Cyber Extortion Enforcement
The indictment of Edward Dubrovsky signals a profound paradigm shift in how law enforcement approaches the cybercrime supply chain. Historically, federal agencies focused predominantly on the core threat actors—the hackers deploying malware, maintaining infrastructure, and directly operating extortion blogs.
By expanding the scope of criminal liability to include individuals and entities operating within the auxiliary ecosystem of threat response, negotiation, and mediation, the Department of Justice is sending an unambiguous warning message to the cybersecurity industry: complicity, facilitation, or unethical maneuvering under the guise of incident response will be met with federal prosecution.
As the legal proceedings formally transition to the Eastern District of Texas, legal scholars and cybersecurity analysts alike will be monitoring the docket closely. With sources indicating that additional charges against principals at other ransomware negotiation firms may be forthcoming, the fall of 2026 may be remembered as the moment the walls closed in not just on the hackers, but on the entire gray-market economy built around paying them off.
This is a developing story. Further updates, official court filings, and institutional responses will be added as verified information becomes available.