Executive Overview
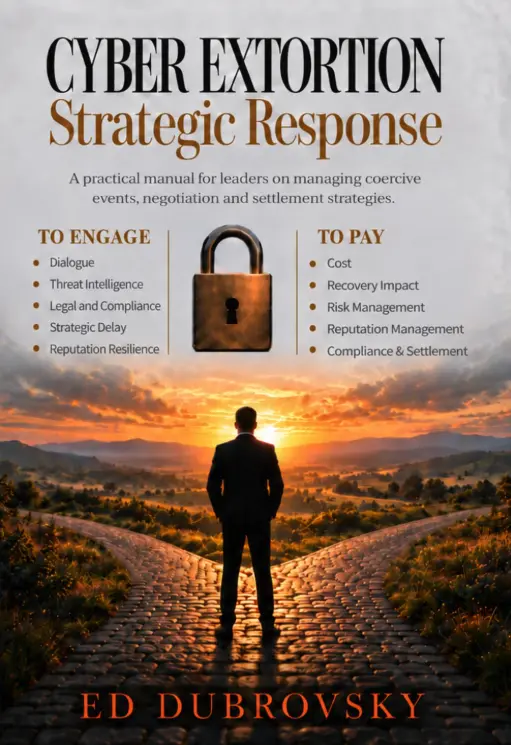
Federal Bureau of Investigation (FBI) agents have taken a high-profile Canadian cybersecurity executive into custody in Pennsylvania, marking a dramatic escalation in the transnational dragnet targeting the notorious ShinyHunters cybercrime syndicate. The arrest of Edward Dubrovsky—a prominent figure in the specialized niche of ransomware negotiation and the author of Cyber Extortion Strategic Response—sends shockwaves through the corporate security sector.
According to multiple intelligence sources and unsealed federal court filings, Dubrovsky’s arrest directly intersects with an aggressive, centralized federal investigation into ShinyHunters. The collective is widely believed to have recently infiltrated FBI infrastructure, siphoning sensitive personnel dossiers containing the units, specializations, and confidential medical and psychiatric records of thousands of federal agents.
The suspect, who was visiting the United States to attend the annual Cyber Risk Summit in Philadelphia, now faces grave federal charges, including conspiracy to commit cyber extortion and interference with commerce by threats. As the epicenter of the investigation shifts decisively to the Eastern District of Texas, the case lays bare an uncomfortable and increasingly blurred line within the cybersecurity industry: the precarious ethical and legal boundaries separating professional incident response, extortion mediation, and alleged complicity with digital racketeers.
Detailed Chronology of an Operation
The sequence of events leading to the dramatic apprehension of Edward Dubrovsky highlights a meticulously coordinated international law enforcement effort designed to dismantle the operational and financial layers of the ShinyHunters organization.
October 5 – October 7, 2026: The Trap in Philadelphia
Edward Dubrovsky arrived in the United States to participate in the high-profile NetDiligence Cyber Risk Summit, hosted at the Loews Philadelphia Hotel. As a senior executive associated with CyberSteward—and formerly a managing director at Cypfer, one of the summit’s principal corporate sponsors—Dubrovsky’s presence at the conference was publicly advertised on professional networking platforms. Attendees anticipated discussions regarding compliance-driven coercive advisory and global ransomware settlement strategies. Instead, federal authorities were closing in.
October 8, 2026: Arrest and Initial Charges
Federal agents intercepted and arrested Dubrovsky in Pennsylvania. Court documents filed in the U.S. District Court for the Eastern District of Pennsylvania—under a slight misspelling of his surname as Dobrovsky—charged the 54-year-old executive with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
October 9, 2026: Jurisdictional Shift to Texas
While the U.S. Bureau of Prisons inmate locator confirmed Dubrovsky’s detention at a federal facility in Philadelphia, court records revealed an immediate administrative pivot. A formal notice filed on October 9 transferred the case file to the Eastern District of Texas. Intelligence sources indicate that federal control over all core investigations pertaining to ShinyHunters has been systematically centralized within the FBI’s field offices in Texas, signaling an expansive multi-jurisdictional prosecution strategy.
Corporate Distancing and Legal Status
In the wake of the arrest, corporate entities rushed to clarify their associations with the accused executive. Cypfer issued a definitive corporate statement clarifying that Dubrovsky was never a founder or co-founder—contrary to legacy claims on his professional profiles—but rather served as a managing director prior to his resignation in November 2025. At the time of his initial court appearances, Dubrovsky remained unrepresented by private counsel, with formal public defender assignments pending.

Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To understand the gravity of Dubrovsky’s arrest, one must examine the operational blueprint and financial footprint of the ShinyHunters hacking collective, alongside the broader macroeconomic realities of the ransomware negotiation industry.
Modus Operandi and Financial Impact
ShinyHunters has historically specialized in targeting software-as-a-service (SaaS) providers and major corporate entities. By deploying sophisticated credential-stuffing campaigns, social engineering, and targeted phishing frameworks, the syndicate routinely siphons monumental volumes of proprietary data from corporate cloud repositories. The group then leverages this intellectual property and customer information against victims, threatening widespread public disclosure unless exorbitant cryptocurrency ransoms are satisfied.
According to federal law enforcement estimates, the collective’s relentless extortion campaigns have successfully extracted more than $70 million from corporate and institutional victims globally over the course of 2026 alone.
The Broader Intermediary Ecosystem
The multibillion-dollar ransomware economy has birthed a specialized shadow industry of third-party negotiators, crisis management firms, and digital incident response providers. These entities are routinely retained by victim organizations to communicate with threat actors, vet data exfiltration claims, and negotiate downward adjustments to ransom demands.
However, law enforcement agencies are increasingly scrutinizing whether certain negotiation firms cross the legal threshold from defensive mitigation into active facilitation—or worse, financial circularity with cybercrime syndicates. Dubrovsky’s own published literature, Cyber Extortion Strategic Response, explicitly highlights this delicate operational tightrope:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors are now tasked with proving whether the defendant’s advisory engagements remained within the bounds of lawful crisis management or crossed into the realm of criminal conspiracy.
The Domino Effect: International Arrests and Internal Breaches
Dubrovsky’s arrest does not occur in a vacuum; it represents a critical node in an accelerating series of law enforcement triumphs and humiliating security compromises for federal intelligence agencies.

The Dutch Connection and the Van Der Stap Raid
In September 2026, international cooperation yielded a major breakthrough when Dutch police apprehended Pepijn van der Stap, a reformed hacker suspected of playing a foundational role within the ShinyHunters infrastructure. Investigators immediately set to work exploiting physical and digital hardware seized during the raid. Sources confirm that the forensic analysis of Van der Stap’s digital devices provided the evidentiary roadmap that led federal investigators straight to Dubrovsky, and points toward impending charges against principals at other ransomware negotiation firms.
The Rise and Fall of "Rey"
The apprehension of Van der Stap triggered an immediate and aggressive backlash from within the hacker collective. An operator styling himself "Rey" assumed operational control of ShinyHunters. Seeking to inflict maximum humiliation on United States law enforcement, Rey launched a retaliatory cyber assault against the FBI itself, breaching the bureau’s online recruitment portal.
This audacious breach exposed the personal identifiers, operational units, specializations, and deeply sensitive medical and psychiatric dossiers of thousands of federal agents.
The hubris of the collective’s new leadership proved to be its undoing. Investigative journalism by Reuters and independent reporting by security analysts identified "Rey" as a teenage hacker named Saif Al-din Khader. Khader was swiftly tracked down and detained by authorities. Pressure from federal investigators quickly turned the young cybercriminal into a cooperative asset, culminating in a failed extortion attempt against a navigation and digital aviation unit recently divested by Boeing in late 2025—an operation that provided the final pieces of intelligence needed to dismantle the core network.
Official Statements and Institutional Silence
The response from official government bodies has been characterized by tightly guarded statements and calculated strategic silence.
- FBI Director Kash Patel: Released a brief statement acknowledging the initial apprehension of the Canadian national on social media platform X (formerly Twitter), praising the cross-agency coordination without divulging specific investigative targets or operational methodologies.
- The Department of Justice and Federal Bureau of Investigation: Both entities have declined to provide expansive commentary regarding the specifics of Dubrovsky’s indictment, citing the ongoing, fluid nature of the multi-state conspiracy investigation.
- Corporate Responses: Representatives from CyberSteward and Cypfer have maintained a defensive posture, emphasizing that corporate governance frameworks remain intact and fully cooperative with federal inquiries as the fallout from the summit-adjacent arrest reverberates through the cyber insurance community.
Future Outlook: A Watershed Moment for Cyber Incident Response
The arrest of Edward Dubrovsky serves as a watershed moment for the global cybersecurity and cyber insurance industries. As federal prosecutors in the Eastern District of Texas build their case against the veteran strategist, several critical long-term implications are already emerging:
- Scrutiny of Ransomware Negotiators: The unspoken "gray market" of ransomware negotiation firms can no longer operate under the assumption of absolute immunity. Law enforcement agencies are establishing a clear precedent: assisting criminal syndicates in structuring extortion payments or facilitating access channels—regardless of corporate justifications—will invite intense federal scrutiny and potential criminal indictment.
- Hardening of Federal Cyber Infrastructure: The brazen infiltration of FBI recruitment databases by ShinyHunters has forced an aggressive internal security audit across all federal intelligence and law enforcement apparatuses. Expect heightened vetting, zero-trust network architectures, and aggressive counter-offensive operations against syndicates that dare target federal personnel files.
- Cascading Indictments: With digital forensics from Dutch police raids and the cooperation of teenage hacker Saif Al-din Khader ("Rey") flowing into federal databases, legal experts anticipate a wave of supplementary indictments. These are expected to target not only technical operators within the ShinyHunters framework but also corrupt intermediaries across the international corporate security landscape.
As this fast-moving investigative narrative continues to develop, the boundary between legitimate threat intelligence advisory and criminal enterprise has been irrevocably redrawn. Federal authorities have signaled that no sector—not even the specialized corporate negotiation firms designed to manage digital extortion—operates beyond the reach of the law.