Executive Overview
Federal Bureau of Investigation (FBI) agents have arrested a prominent Canadian cybersecurity executive in Pennsylvania, marking a dramatic escalation in the ongoing, multi-national investigation into the notorious ShinyHunters cyber extortion syndicate. The suspect, identified in federal court records as Edward Dubrovsky—a 54-year-old security professional, author, and senior figure within the Canadian ransomware response ecosystem—was taken into custody on October 8, 2026.
The arrest comes at a humiliating time for America’s premier law enforcement agency. Just weeks prior, ShinyHunters managed to breach federal systems, relieving the FBI of sensitive, highly classified personnel data encompassing thousands of active agents. This trove included unit assignments, specializations, and confidential medical and psychiatric records.
Dubrovsky’s apprehension occurred while he was visiting Philadelphia to attend the high-profile NetDiligence Cyber Risk Summit. While initial public statements from the FBI and mainstream reports initially withheld the suspect’s identity, investigative reporting and court filings have since pieced together a web of connections linking ransomware advisory firms, international police operations, and an accelerating federal probe now centralized in the Eastern District of Texas.
As federal prosecutors move to unseal indictments and transfer proceedings southward, the case threatens to expose murky intersections between commercial incident response firms, extortion negotiators, and elite cybercrime syndicates. With over $70 million allegedly extorted by ShinyHunters this year alone, the fallout from Dubrovsky’s arrest promises to reshape how corporate America, insurance companies, and law enforcement interact with the shadowy multi-million-dollar economy of ransomware negotiation.
Detailed Chronology: From Philadelphia Conference to Federal Custody
The NetDiligence Cyber Risk Summit
The sequence of events leading to Dubrovsky’s arrest unfolded in early October 2026. According to conference schedules and registration records, the annual Cyber Risk Summit was held at the Loews Philadelphia Hotel from October 5 to October 7. The event drew hundreds of professionals from the cyber insurance, legal, and incident response communities.
Among the primary sponsors of the event was Cypfer, a Canadian cybersecurity firm specializing in ransomware mitigation and extortion negotiations. Dubrovsky, whose LinkedIn profile and professional biography long cited him as an "ex-founder" of Cypfer (though a Cypfer spokesperson later clarified that he served merely as a managing director before resigning in November 2025), was slated to attend the summit representing his new venture, CyberSteward, another Canadian security firm and conference sponsor.
Only one month prior to the event, Dubrovsky had taken to LinkedIn to express enthusiasm for the summit, writing:
"Looking forward to continuing conversations around strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services that are global and truly agnostic."
Those conversations were cut short. On October 8, federal agents moved in, arresting Dubrovsky in Pennsylvania on charges of cyber extortion and conspiracy.
Court Filings and Jurisdictional Shifts
Federal court documents filed under the slightly misspelled name Edward Dobrovsky reveal gravity-heavy charges, including "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."

While the core complaint and foundational evidentiary documents remain heavily sealed, snippets of the docket indexed on CourtListener.com confirm the nature of the federal government’s case. Following his booking, Dubrovsky was temporarily processed into a federal facility in Philadelphia, as logged by the U.S. Bureau of Prisons inmate locator.
However, jurisdictional control of the case shifted rapidly. On October 9, a formal notice moved the docket to the U.S. District Court for the Eastern District of Texas, which sources close to the investigation confirm has become the central operational hub for the comprehensive federal probe into ShinyHunters. As of writing, court records indicate Dubrovsky has not yet retained private counsel or been formally assigned a public defender, and he has declined or been unable to issue immediate public comments.
Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
Who is ShinyHunters?
ShinyHunters is not a traditional, monolithic ransomware gang. Rather, the collective operates as a sophisticated, agile cybercriminal enterprise specializing in data theft extortion. Their preferred modus operandi involves weaponizing stolen credentials, executing targeted phishing campaigns, and breaching Software-as-a-Service (SaaS) providers and corporate repositories. Once inside, they siphon gigabytes of proprietary data, intellectual property, and customer records, demanding massive cryptocurrency ransoms under the threat of public leaks.
According to internal FBI tracking metrics, the group has experienced a hyper-lucrative year, successfully extorting upwards of $70 million from corporate victims globally throughout 2026.
The Breach of the FBI’s Recruitment Portal
The urgency of the federal response is directly tied to an unprecedented security breach suffered by the Bureau itself. In late 2025 and early 2026, ShinyHunters infiltrated an online recruitment portal maintained by the FBI.
The compromised data trove was devastatingly intimate. It included:
- Detailed rosters of active field agents.
- Specific unit deployments and tactical specializations.
- Highly confidential medical histories and psychiatric evaluation records.
The acquisition of this data gave the hackers immense psychological and operational leverage over federal investigators, setting the stage for a bitter digital cat-and-mouse game.
International Arrests and the Rise of "Rey"
Dubrovsky’s arrest does not occur in a vacuum; it is the latest domino in a coordinated international crackdown.
- The Dutch Raid: In September 2026, Dutch police executed raids resulting in the arrest of Pepijn van der Stap, a reformed hacker suspected of deep operational ties to ShinyHunters. Seized digital devices from Van der Stap’s residence have provided FBI forensic investigators with a goldmine of communications, transaction logs, and infrastructure blueprints.
- The Rise and Fall of "Rey": Immediately following Van der Stap’s arrest, an anonymous high-ranking ShinyHunters member operating under the online handle "Rey" assumed tactical control of the group. Rey began taunting federal authorities on X (formerly Twitter) and Telegram regarding the stolen FBI personnel files.
- The Identification of Saif Al-din Khader: Investigative journalism by Reuters and independent researchers pinpointed "Rey" as a teenage cybercriminal named Saif Al-din Khader. Khader was subsequently detained and began cooperating with federal authorities. On October 7—just one day before Dubrovsky’s arrest—details emerged regarding Khader’s apprehension as the group attempted to shake down a digital aviation navigation unit recently divested by Boeing in late 2025.
Official Statements and Industry Impact
The official silence from federal leadership contrasts sharply with the frantic behind-the-scenes activity. FBI Director Kash Patel acknowledged the general crackdown via a terse statement on X, though he omitted specific names. Similarly, the FBI field office in Texas has maintained a strict "no comment" policy as prosecutors prep for expansive indictments.
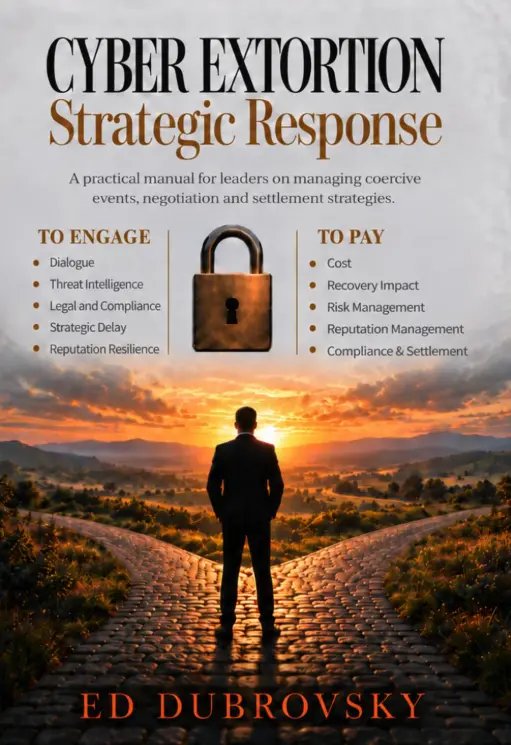
However, the ripple effects across the commercial cybersecurity landscape are profound. Dubrovsky is a well-known figure in the niche ecosystem of ransomware response. Beyond his executive roles at Cypfer and CyberSteward, he is the author of Cyber Extortion Strategic Response, a 252-page textbook billed as a definitive guide for organizations navigating corporate digital hostage situations.

Ironically, passages from Dubrovsky’s own work now read with grim prescience. In the book’s Amazon synopsis, he wrote:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors in Texas now aim to determine whether Dubrovsky’s professional engagement crossed the blurry, heavily regulated legal line separating legitimate third-party crisis negotiation from active collusion, extortion facilitation, or money laundering on behalf of cybercriminal cartels.
Future Outlook: A Turning Point in Ransomware Prosecutions
The arrest of Edward Dubrovsky signals a fundamental and aggressive shift in how the United States Department of Justice and the FBI approach the multi-billion-dollar ransomware ecosystem. For years, the commercial incident response and cyber insurance sectors operated in a legal gray zone. Companies struck by ransomware routinely hired specialized consulting firms to discreetly mediate, negotiate, and—when deemed necessary—facilitate cryptocurrency payouts to criminal actors to minimize brand damage and operational downtime.
By targeting an executive within the negotiation ecosystem, federal authorities are sending an unmistakable message: the firewall protecting third-party fixers is crumbling.
As the Eastern District of Texas prepares to unseal further indictments, legal analysts predict turbulent waters ahead for the cyber insurance and incident response industries. Sources close to the investigation hint that Dubrovsky may not be the last executive from a ransomware mitigation firm to face federal scrutiny.
For ShinyHunters, the relentless pressure from international law enforcement—compounded by the flip of teenage ringleader Saif Al-din Khader and the seizure of Pepijn van der Stap’s infrastructure—has severely fractured the syndicate’s operational security. Yet, as history has shown with decentralized cybercrime rings, the vacuum left by arrested leaders is often rapidly filled by new actors.
For now, all eyes remain fixed on the federal courtrooms in Texas, where the legal battle over the boundaries of digital extortion will set monumental precedents for years to come.
This is a developing story. Further updates, court filings, and official statements will be appended as new information becomes available.