In a decisive maneuver to dismantle the financial infrastructure propping up Moscow’s wartime economy, the United Kingdom has levied sweeping economic sanctions against Cryptomus, a chameleonic cryptocurrency platform. According to leading blockchain intelligence firms and international investigators, Cryptomus has operated as a critical, high-volume conduit for illicit funds—facilitating ransomware payouts, narcotics distribution, darknet market transactions, specialized cybercrime services, and sanction-evasion schemes designed to shield Russia from Western financial restrictions.
Announced on October 8, the U.K. Treasury’s sanctions freeze any assets held by Cryptomus within British financial institutions and legally bar UK-based companies, individuals, and virtual asset service providers from engaging in business dealings with the platform. Alongside Cryptomus, the U.K. targeted a broader constellation of shadow payment networks, including VexPay, TokenSpot, and the Tsunami Payments service.
The crackdown represents a watershed moment in international financial policing. Beyond merely penalizing a digital ledger, the UK’s actions expose a complex corporate labyrinth stretching from Vancouver shell companies to fraudulent regulatory bodies operating in disputed geopolitical territories. Furthermore, industry experts note this is the first known instance of a "Five Eyes" intelligence-sharing nation (Australia, Canada, New Zealand, the United Kingdom, and the United States) directly sanctioning a cryptocurrency entity incorporated within another Five Eyes jurisdiction.
While previous regulatory actions—such as a record-shattering $176 million fine levied by Canada—failed to halt the platform’s operations due to jurisdictional enforcement gaps, the U.K. sanctions aim for the jugular. As blockchain investigator Richard Sanders succinctly observed: "A fine doesn’t stop a cryptocurrency payment processor from processing payments. Sanctions kill the operation. The distinction matters."
Detailed Chronology of an Illicit Empire
To understand how Cryptomus evolved into a multi-billion-dollar juggernaut for global cybercrime and Russian sanctions evasion, one must trace its operational lifecycle, tactical rebrandings, and evasion strategies over the past four years.
2022: Emergence and Early Growth
Cryptomus burst onto the digital finance ecosystem in 2022, operating initially under names such as Certa Payments and Xeltox Enterprises. Positioned ostensibly as a standard crypto payment gateway for e-commerce, the platform quickly gained traction among dozens of Russian cryptocurrency exchanges and underground websites hawking illicit cybercrime-as-a-service tools.
During its formative years, Cryptomus operated with virtually non-existent "Know Your Customer" (KYC) compliance. Investigators discovered that its parent company, Certa Payments, shared a physical address in Vancouver, British Columbia, with dozens of other foreign currency dealers and money-transfer businesses—none of which maintained a genuine physical presence at the location. By prioritizing anonymity and rapid settlement, Cryptomus carved out a lucrative niche as a premier payment processor for threat actors operating across Eastern Europe and beyond.
Late 2024: The Net Tightens
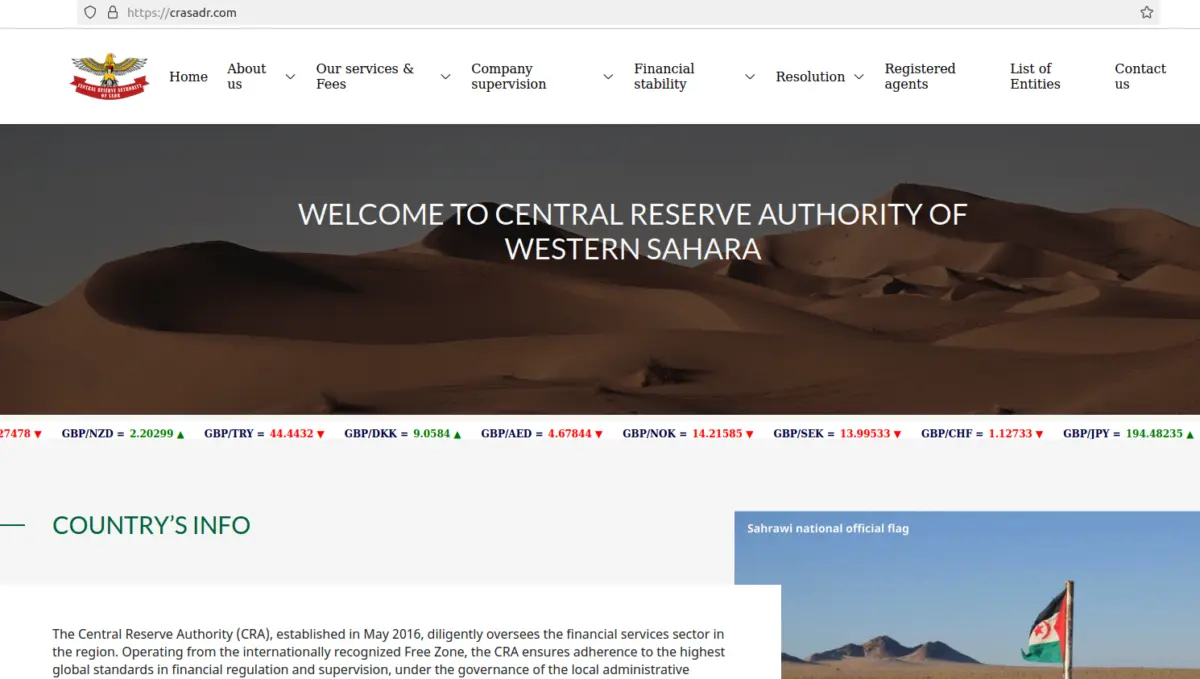
By late 2024, independent investigative reporting by cybersecurity researcher Brian Krebs illuminated the mechanics of how Cryptomus bridged the gap between unregulated digital currencies and hard cash within Russian traditional banking networks. The investigation uncovered astounding operational details, notably that the sole shareholder of Certa Payments was a 25-year-old Ukrainian national who simultaneously headed several other corporate entities. Among these was the WS Management and Advisory Corporation, a self-proclaimed regulatory body purporting to license crypto and forex businesses in the disputed northwest African territory of Western Sahara.
Despite mounting public scrutiny and accumulating blockchain telemetry linking the platform to criminal proceeds, Cryptomus continued to scale its processing volume, acting as a financial life raft for entities cut off by traditional international banking bans.
Late 2025: Canadian Penalties and the Birth of "Heleket"
The regulatory pressure reached a fever pitch in October 2025, when Canadian authorities hit Cryptomus with a historic administrative monetary penalty of CAD $176 million for severe violations of anti-money laundering (AML) and counter-terrorist financing (CTF) regulations.
Faced with a crippling domestic fine, Cryptomus executed a classic chameleonic maneuver. Rather than complying with Canadian regulatory mandates, the platform launched a parallel service named Heleket, designed to quietly absorb its legacy merchant base and continue processing high-risk, zero-KYC transactions. Meanwhile, Cryptomus officially appealed the Canadian penalty.
However, because the multi-million-dollar fine proved largely uncollectible across international borders, the platform’s underlying operational infrastructure remained fully functional. Heleket seamlessly stepped into the breach, maintaining active support channels on Telegram where customer service agents brazenly—and falsely—denied any operational or corporate affiliation with Cryptomus, even as blockchain analytics proved otherwise.
October 2026: The U.K. Drops the Hammer
The cat-and-mouse game came to a crashing halt on October 8, 2026. Recognizing that civil fines were wholly insufficient against resilient, cross-border criminal operations, the United Kingdom deployed targeted economic sanctions against Cryptomus, Heleket, and associated nodes like VexPay and TokenSpot.
Within hours of the announcement, user support bots for Cryptomus and Heleket on Telegram began notifying panicked merchants that the platform was suddenly unable to process inbound or outbound transactions. Blocked from accessing British financial institutions and prohibited from interfacing with UK partners, the enterprise suffered an immediate operational seizure.
Supporting Context & Metrics: The Scale of the Enterprise
The sheer volume of capital processed by Cryptomus and its spin-off entities underscores why Western governments were forced to escalate their response from monetary fines to total economic sanctions.
Multi-Billion-Dollar Throughput
According to forensic data published by blockchain analysis firm TRM Labs in April 2026, Cryptomus had processed more than $7 billion in cumulative cryptocurrency transactions since its inception in 2022. While a portion of this volume represented legitimate e-commerce, a staggering percentage was directly tied to high-severity illicit categories. TRM Labs identified transactional flows connected to:
Global ransomware syndicates laundering extortion payments.
Vendors trafficking in child sexual abuse material (CSAM).
State-aligned and independent terrorist financing networks.
International human trafficking operations.
Chainalysis Metrics on Wartime Evasion
In its analysis of the October 2026 sanctions, blockchain data-crunching firm Chainalysis emphasized that Cryptomus and Heleket had become foundational pillars for Russia’s wartime economy, allowing sanctioned entities to bypass SWIFT blocks and trade restrictions.
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity," Chainalysis detailed in an advisory published on October 8. The firm’s telemetry revealed that during peak operational periods in late 2025, the combined services received more illicit funds across tracked categories than traditional cryptocurrency mixers. Furthermore, the monthly count of distinct illicit counterparties interacting with the platform surged to more than 900 in a single month, illustrating an aggressive expansion of its criminal clientele.
Official Statements and Industry Analysis
The international response to the takedown of Cryptomus highlights a growing consensus among intelligence agencies and blockchain analytics firms: shadow crypto platforms are no longer viewed merely as technical nuisances, but as direct threats to national security and global financial stability.
The Regulatory Realities of "Five Eyes" Jurisdictions
Richard Sanders, a veteran blockchain investigator who spent months mapping Cryptomus’s labyrinthine infrastructure and transacting directly with its customer base, stressed the unique legal precedent set by the U.K. Treasury.
Writing on LinkedIn immediately following the sanctions, Sanders noted that Canada’s CAD $176 million penalty, while symbolically important, exposed the severe limitations of domestic monetary fines in the decentralized digital asset space.
"A fine doesn’t stop a cryptocurrency payment processor from processing payments," Sanders wrote. "Sanctions kill the operation. The distinction matters."
Sanders also underscored the geopolitical significance of the action, noting that this marks the first known instance of one "Five Eyes" intelligence alliance member sanctioning a corporate entity officially domiciled within the territory of another Five Eyes partner. This cross-jurisdictional enforcement shatters the illusion that corporate shell companies registered in Western democracies can operate with impunity if they cater exclusively to hostile foreign actors.
Chainalysis on the Broader Infrastructure
Chainalysis echoed these sentiments, framing the U.K. sanctions not as an isolated event, but as a critical blow to the broader shadow financial infrastructure supporting Russian state-sponsored cybercrime and economic sanctions evasion. By targeting secondary nodes like TokenSpot, VexPay, and the Tsunami Payments service, Western regulators are signaling a zero-tolerance policy for payment processors that serve as bridges between Western digital economies and sanctioned Russian financial networks.
The Phantom Regulator: Tracing the Roots of Pseudo-Legitimacy
One of the most bizarre and illuminating revelations emerging from the investigations into Cryptomus is the origin of its operational authority. How do unregistered, anonymous crypto processors acquire the veneer of legitimacy required to fool compliance officers and secure banking relationships?
The answer points toward a surreal nexus of fake financial oversight, shell corporations, and disputed territories.
The Western Sahara Connection
During the comprehensive 2024 investigation into Cryptomus’s parent firm, Certa Payments, researchers uncovered that the company’s sole shareholder was a 25-year-old Ukrainian woman. Beyond managing Certa Payments, she also headed the WS Management and Advisory Corporation.
This entity marketed itself as an official regulatory body possessing exclusive jurisdiction to issue operational licenses for cryptocurrency exchanges, foreign exchange (forex) brokers, and online gaming platforms incorporated within the Western Sahara—a disputed region in northwest Africa that lacks widespread international recognition as a sovereign nation.
The Digital Blueprint of a Shell Empire
The operational infrastructure of this pseudo-regulator reads like a playbook for digital fraud:
The Regulatory Portal: The entity operated a website under the domain crasadr.com, purporting to represent the Central Reserve Authority of Western Sahara, complete with official-looking directories of licensed entities.
Shared Infrastructure: Technical analysis revealed that Certa Payments’ former web domain (certa.website) shared a single physical server with 12 other distinct domains. Among them was rasd-state.ws, a digital property explicitly tied to the fake Central Reserve Authority.
By inventing a regulatory body in a lawless or disputed zone, the architects of Cryptomus engineered a self-contained bureaucratic loop. They created their own licensing authority, granted themselves permission to operate as a financial institution, and used that fraudulent status to establish banking relationships and hoodwink compliance watchdogs across multiple continents.
Future Outlook: The Death Knell for Chameleonic Gateways?
The U.K.’s targeted sanctions against Cryptomus and its sibling platforms signal a permanent shift in how Western governments intend to police the intersection of cryptocurrency and geopolitical warfare.
As blockchain forensic tools become more sophisticated, the ability of bad actors to evade detection simply by rebranding—transforming from Certa Payments to Cryptomus, and subsequently to Heleket—is rapidly diminishing. The coordinated intelligence sharing among Five Eyes nations ensures that corporate shell games, fake regulatory authorities in disputed territories, and Vancouver virtual office fronts can no longer obscure the ultimate beneficiaries of illicit cash flows.
For the cybercrime ecosystem, the fall of Cryptomus serves as a stark warning. While decentralized technologies promise financial autonomy, the centralized cash-out ramps required to convert digital extortion payments into fiat currency remain acutely vulnerable to targeted state power. As international regulators continue to choke off shadow payment processors, the cost of doing illicit business in the global cryptographic underground has never been higher.