Executive Overview: White House Network Compromised by Commercial Residential Proxy Services
In a startling cybersecurity oversight, multiple computers and mobile devices connected to the dedicated network of the Executive Office of the President have been actively operating as residential proxy nodes. Security experts revealed that these devices—reportedly utilized by White House staffers—have effectively rendered their secure internet addresses available for rent on the open market.
This startling breach of network hygiene means that anyone willing to pay a nominal fee can route internet traffic through the heart of the United States government’s administrative infrastructure.
The security firms Layer3 Intel and Synthient independently detected this activity, tracing it directly to the autonomous system block reserved for the White House (AS2650). Among the providers identified operating within the secure network is Infatica, a controversial residential proxy service founded by Vladimir Fomenko—a Russian national whose previous web-hosting outfit, King Servers, served as the staging ground for Russian state-sponsored cyberattacks against state election systems in Arizona and Illinois in 2016.
The implications of this discovery stretch far beyond standard corporate compliance failures. Residential proxies allow external users to mask their true geographic locations and route malicious traffic through innocent victims’ IP addresses. Because the traffic appears to originate from the White House, any malicious operations, credential stuffing attacks, financial frauds, or data scraping conducted via these nodes would be traced directly back to executive government assets.
Security researchers emphasize that this is not an isolated high-tech intrusion or an advanced persistent threat (APT) state-sponsored hack; rather, it is a glaring byproduct of lax device management, unvetted software downloads, and the pervasive monetization of everyday desktop and mobile applications through shady software development kits (SDKs).
Detailed Chronology: Uncovering the White House Proxy Leak
The exposure of the Executive Office of the President’s network began as a matter of routine telemetry analysis before mutating into a major national security concern.
The October to November Window
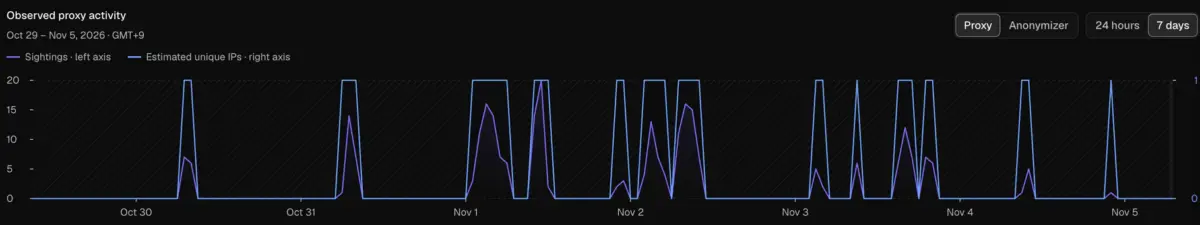
Between October 5 and November 3, security researchers at Layer3 Intel monitoring global residential proxy networks noticed persistent beaconing emanating from the IP address space explicitly designated for the White House (AS2650). During this intensive 30-day monitoring window, Layer3 documented 236 separate instances where proxy traffic successfully exited through the White House network.
The traffic did not appear to be an intermittent glitch. Layer3 Intel reported that proxy exit nodes originating from White House infrastructure were active on 26 out of 30 days. Crucially, the telemetry revealed a distinct temporal pattern: the vast majority of this unauthorized proxy activity occurred during off-hours, specifically between 5:00 p.m. and midnight, pointing heavily toward personal device usage or employee-owned hardware brought into the workplace and connected to internal networks.
The Infatica Connection
Concurrently, proxy-tracking platform Synthient published findings on social media platforms highlighting that a significant portion of the traffic observed exiting AS2650 was tied to Windows 11 installations running Infatica.
Infatica is a commercial residential proxy program frequently bundled inside seemingly innocuous "free" mobile apps and desktop browser extensions. App developers integrate Infatica’s software development kits (SDKs) into their products to monetize user bases, generating passive revenue per installation while turning user devices into monetized exit nodes.
For cybersecurity veterans, the association with Infatica immediately raised red flags due to its founder, Vladimir Fomenko. A decade prior, Fomenko’s hosting company, King Servers, was identified by U.S. intelligence and cybersecurity investigators as the infrastructure provider behind six of the eight IP addresses utilized by Russian state intelligence services to breach voter registration databases in Arizona and Illinois ahead of the 2016 U.S. presidential election.
A Flood of Resellers
While Infatica caught early attention due to its founder’s background, deeper investigation revealed an even more alarming reality. Layer3 Intel analysts quickly realized that Infatica was merely one piece of a much larger puzzle.
Upon conducting a broader audit of global proxy availability for the AS2650 block, Layer3 discovered that 28 separate residential proxy services possessed active exit nodes traversing the White House network.
"This is public access," the Layer3 Intel research team stated in an advisory. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
Supporting Context & Metrics: The Global Threat of Residential Proxies
To fully grasp the gravity of the White House incident, one must understand the architecture and booming underground economy of residential proxy networks.
How Residential Proxies Weaponize Everyday Devices
Residential proxies differ fundamentally from traditional data-center proxies. Data-center IP addresses are easily flagged and blocked by websites because they clearly belong to cloud providers or hosting companies. Residential proxies, however, utilize legitimate home broadband or mobile IP addresses assigned by Internet Service Providers (ISPs) to everyday consumers.
To build these massive pools, proxy companies often partner with sketchy app developers, offering them monetization opportunities via SDK embeds. When an unsuspecting user downloads a free VPN, a screensaver app, a mobile game, or a utility extension, they inadvertently agree to terms of service that turn their device into a proxy relay server.
Once installed, the proxy network can route third-party internet traffic through the user’s local network. From the perspective of target websites, banks, or corporate systems, the traffic appears to be a legitimate user sitting in a residential living room, rendering traditional IP-blocking defenses useless.
The Economics of Exploitation
The commercialization of residential bandwidth has created a thriving, largely unregulated cybercrime ecosystem. Proxy providers and their resellers frequently market bandwidth for as low as $0.60 to $1.00 per gigabyte.
"That means for less than a dollar you can gain access into some of the most confidential and trusted networks," Ben Brundage, founder of Synthient, told KrebsOnSecurity. "The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
This lack of vetting makes residential proxy networks a primary vector for a wide array of cybercrimes, including:
- Account Takeovers (ATO): Bypassing rate limits and geographic security blocks to execute credential-stuffing campaigns against banking and retail portals.
- Ad Fraud: Automatically generating fake ad impressions and clicks while hiding behind trusted enterprise or government IPs.
- Mass Content Scraping: Harvesting protected data, intellectual property, and copyrighted material to train artificial intelligence (AI) models without detection.
Local Network Risks: The Kimwolf Precedent
Beyond turning victim devices into unwitting accomplices for outbound traffic attacks, residential proxy software introduces profound inbound security threats.
In late 2025, researchers uncovered widespread vulnerabilities in residential proxy applications that allowed cybercriminals to execute remote probes against the local networks of devices running the software. By January 2026, dozens of proxy services were forced into emergency patching cycles after Synthient exposed how threat actors—exemplified by botnets like "Kimwolf"—were exploiting these architectural flaws to pivot from infected endpoints directly into corporate and home local area networks (LANs).
If a staffer brings an infected laptop or personal tablet into a high-security government facility, connects it to agency Wi-Fi, and runs a proxy application, that device can act as a bridge, potentially exposing internal routers, printers, and sensitive adjacent computers to external threat actors.
Pervasive Corporate and Government Penetration
The exposure at the White House is emblematic of a systemic failure across global enterprises and public sector networks. Residential proxy software frequently finds its way onto corporate endpoints via employee shadow IT, BYOD (Bring Your Own Device) policies, and casual downloading habits.
Data compiled by telemetry firms paints a sobering picture of how deeply entrenched these services are within critical infrastructure:
- Government Networks: In a January 2026 industry briefing, proxy-tracking service Spur revealed it had detected active residential proxies running within nearly 300 government-owned and operated networks.
- Critical Utilities: Spur’s telemetry identified active nodes inside 318 utility companies.
- Healthcare & Finance: The tracking service found proxy activity across 166 healthcare organizations and 141 banking and financial institutions.
- Broad Enterprise Exposure: Security firm Infoblox reported earlier this year that an astonishing 65% of its entire enterprise customer base had internal endpoints querying known residential proxy-related domains.
Official Statements and Immediate Fallout
As the technical details of the White House proxy leaks circulated within the cybersecurity community, institutional reactions remained tightly controlled.
At the time of publication, the White House has not officially responded to multiple media requests for comment regarding the Layer3 Intel and Synthient disclosures. The silence from the Executive Office of the President underscores the sensitivity of the incident, leaving federal IT and cybersecurity agencies scrambling internally to identify the specific personnel, hardware assets, and applications responsible for the breach.
Federal standards for endpoint security normally mandate strict limitations on software installations, device management, and the prohibition of unauthorized external tunneling applications. However, the presence of 28 distinct proxy services operating across AS2650 demonstrates that existing Mobile Device Management (MDM) and Endpoint Detection and Response (EDR) protocols deployed on White House networks failed to catch or block these applications during onboarding or routine operations.
Cybersecurity policy analysts note that this incident will likely trigger immediate congressional inquiries into White House IT security practices, hardware procurement, and staff cybersecurity hygiene training.
Future Outlook: Remediation and the Path Forward
The discovery of commercial proxy exit nodes within the Executive Office of the President serves as a stark wake-up call for public and private sector organizations alike. Securing modern perimeters requires far more than traditional perimeter firewalls; it demands granular visibility into endpoint behavior and aggressive enforcement against shadow IT and monetized SDK applications.
To mitigate the escalating threat posed by residential proxy networks, enterprise security architects recommend the following technical countermeasures:
- Strict DNS and Domain Filtering: Organizations must implement robust Domain Name System (DNS) filtering to block outbound connection attempts to known residential proxy command-and-control servers, API endpoints, and broker domains (such as those tied to Infatica and competing services).
- Enhanced EDR and Application Whitelisting: Endpoint Detection and Response (EDR) solutions must be configured to flag and terminate unauthorized background processes, particularly unknown browser extensions, free VPN clients, and utilities suspected of embedding monetization SDKs.
- Rigorous BYOD and Asset Segregation: Personal devices brought into sensitive workplaces must be strictly barred from connecting to internal enterprise networks. Any Bring Your Own Device policies must require mandatory security posture assessment before granting Wi-Fi access.
- Zero-Trust Network Access (ZTNA): Shifting away from implicit trust based on network geography is vital. Even traffic originating from dedicated government IP blocks must be continually authenticated, monitored, and inspected for anomalous proxy behaviors.
As residential proxy operators continue to innovate new ways to monetize consumer bandwidth, the line between innocent user application and active cybercrime infrastructure has blurred dangerously. For the White House—and the thousands of corporate and government networks similarly exposed—closing this loophole is no longer a matter of basic network hygiene, but an urgent imperative of national security.