Executive Overview
In a startling cybersecurity oversight within the highest levels of the United States government, security experts have uncovered that multiple staff members within the Executive Office of the President have been utilizing computers and mobile devices connected to commercial residential proxy networks. This dangerous configuration inadvertently renders official government internet Protocol (IP) addresses available for rent to anonymous third parties across the globe.
The alarming finding, first brought to light by threat intelligence firm Layer3 Intel and corroborated by proxy-tracking specialists Synthient, reveals that sensitive government network infrastructure has been co-opted into lucrative global proxy pools. Most concerningly, among the nearly 30 distinct proxy networks operating out of the White House network space (AS2650) is Infatica, a service founded by Vladimir Fomenko,
a Russian national whose web-hosting enterprise previously served as the command-and-control backbone for cyberattacks targeting state election databases in Illinois and Arizona during the 2016 U.S. presidential election.
The implications of this exposure extend far beyond standard IT hygiene failures. By permitting residential proxy software to operate on machines connected to secure government networks, users have effectively punched an unmonitored, external backdoor straight into institutional perimeters. For as little as sixty cents a gigabyte, any malicious actor, foreign intelligence service, or financial fraudster could rent a pristine White House IP address to mask their activities. This alarming lapse underscores a broader, systemic corporate and governmental vulnerability: the insidious spread of monetized software development kits (SDKs) embedded in seemingly benign mobile and desktop applications.
Detailed Chronology of the Discovery
The discovery of White House network assets acting as commercial proxy exit nodes was not the result of a targeted espionage probe, but rather a byproduct of routine, expansive global scanning by security researchers monitoring the underground proxy ecosystem.
October 5 to November 3: Persistent Beaconing Detected
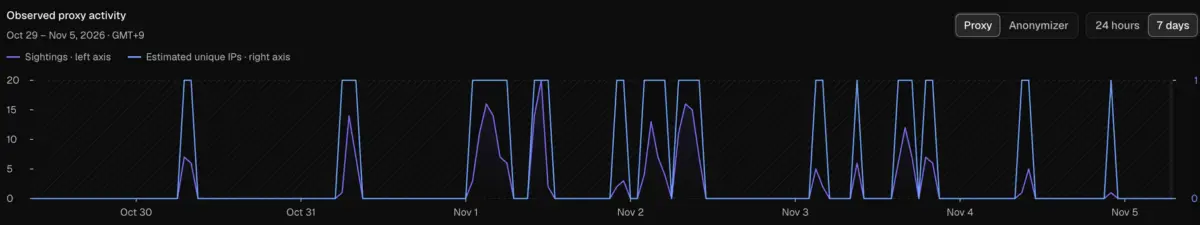
According to telemetry data released by Layer3 Intel, anomalous proxy traffic originating from the dedicated internet address block reserved for the Executive Office of the President (AS2650) was logged persistently between October 5 and November 3. During this crucial 30-day window, Layer3’s automated probes recorded 236 distinct instances where residential proxy networks successfully routed external web traffic out through the White House network infrastructure.
Further compounding the gravity of the findings, Layer3 reported that these proxy exit nodes materialized across six unique government IP addresses on 26 of the 30 monitored days. Temporal analysis of the traffic revealed a distinct behavioral pattern: the vast majority of proxy relay activity spiked during evening hours, specifically between 5:00 p.m. and midnight. This temporal distribution strongly suggests the involvement of personal devices, bring-your-own-device (BYOD) hardware, or government-issued equipment being utilized by staffers during off-hours, during which users may be interacting with consumer software, gaming applications, or streaming platforms harboring hidden proxy monetization modules.
Social Media Validation and Attribution
As telemetry data was corroborated across threat intelligence communities, Synthient published real-time findings on X (formerly Twitter) confirming that the traffic exiting through AS2650 directly mapped to multiple Windows 11 installations running Infatica. Synthient’s technical breakdown illustrated how Infatica’s background services had hooked into the operating systems of devices stationed within the White House ecosystem, transforming corporate and executive-level hardware into monetized traffic relays.
Layer3 Intel researchers emphasized the sheer accidental nature of their discovery in an official technical post:
"This is public access. Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
The Threat Landscape: Mechanics of Residential Proxies and Historical Parallels
To fully grasp the magnitude of the White House network exposure, one must understand how modern residential proxy networks operate and the murky geopolitical affiliations underpinning them.
How Residential Proxies Work
Residential proxies differ fundamentally from traditional data-center proxies. While data-center IPs are easily flagged and blocked by website security filters because they originate from known cloud hosting providers (such as Amazon Web Services or DigitalOcean), residential IPs belong to consumer Internet Service Providers (ISPs) assigned to residential homes, corporate offices, and—in dangerously misconfigured cases—government facilities.
Commercial proxy providers build vast botnets or opt-in peer-to-peer networks by integrating Software Development Kits (SDKs) into free applications, browser extensions, VPNs, mobile games, and utility software. Unsuspecting users download these apps, unknowingly agreeing to terms of service that permit the developer to route third-party internet traffic through the user’s local connection.
Consequently, when a cybercriminal or data scraper routes a web request through a proxy provider, the target website sees the traffic as originating directly from a legitimate resident or, in this unprecedented case, a secure federal government facility.
The Shadow of Infatica and Vladimir Fomenko
The involvement of Infatica injects an immediate counterintelligence dimension into the incident. Infatica was founded by Vladimir Fomenko, a Russian developer whose previous enterprise, King Servers, gained notoriety in the wake of the 2016 U.S. elections. According to federal investigators and cybersecurity firms, King Servers provided the infrastructure for six of the eight IP addresses utilized by Russian state-sponsored actors to execute breaches against voter registration databases in Arizona and Illinois.
While commercial residential proxy providers routinely claim that their services are utilized legitimately for market research, search engine optimization (SEO) monitoring, and ad verification, security researchers have repeatedly demonstrated that the lack of rigorous Know Your Customer (KYC) protocols makes them indispensable tools for transnational cybercrime syndicates.
Twenty-Eight Services Deep
Perhaps the most shocking revelation from Layer3 Intel’s investigation is that Infatica was merely one piece of a much larger puzzle. Layer3 discovered that 28 separate residential proxy services possessed the capability to route traffic and exit through the White House network space. This indicates a systemic, multi-vector penetration of employee endpoints by diverse proxy ecosystems, highlighting a complete breakdown in endpoint security monitoring and software inventory control within the Executive Office.
Supporting Context, Vulnerabilities, and Empirical Metrics
The White House incident is not an isolated anomaly, but rather a high-profile symptom of a sweeping enterprise security crisis. Over the past several years, residential proxies have evolved from a nuisance utilized for ad fraud into a primary vector for advanced cybercrime and local network reconnaissance.
Local Network Exploitation and Malware Delivery
In late 2025 and early 2026, the intersection of residential proxies and enterprise security reached a boiling point. Security researchers uncovered that malicious actors were weaponizing structural vulnerabilities inherent in proxy software architectures. In January 2026, proxy services were forced into emergency patching cycles after Synthient Founder Ben Brundage exposed how criminal hackers were exploiting residential proxy nodes to scan, probe, and infiltrate the local local-area networks (LANs) of devices connected behind the proxy endpoints.
Speaking to KrebsOnSecurity, Brundage emphasized the alarming affordability and accessibility of these pathways:
"Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte; that means for less than a dollar you can gain access into some of the most confidential and trusted networks. The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
This vulnerability allows bad actors to pivot from an infected consumer laptop or a misconfigured office desktop directly into adjacent enterprise or government systems, bypassing traditional perimeter defenses by piggybacking on trusted local network trust relationships.
Macro-Level Metrics: A Corporate and Government Epidemic
Empirical data collected across the cybersecurity industry demonstrates that residential proxy software has thoroughly infiltrated the highest echelons of global infrastructure. Comprehensive scanning initiatives undertaken by proxy-tracking firms paint a sobering picture of corporate and governmental exposure:
- Spur’s Government & Critical Infrastructure Audit (January 2026): During a comprehensive webinar, proxy-tracking service Spur revealed that residential proxy nodes were actively beaconing out from nearly 300 government-owned and operated networks. Furthermore, Spur identified proxy installations across 318 utility companies, 166 healthcare institutions and hospitals, and 141 financial and banking entities.
- Infoblox Enterprise Study: Security firm Infoblox published research indicating that a staggering 65% of its entire enterprise customer base was actively querying one or more residential proxy-related domains from within corporate perimeters.
These figures illustrate that the presence of residential proxy SDKs on government networks is part of an industry-wide blind spot. Employees routinely bring personal laptops into secure work environments, connect corporate hardware to public Wi-Fi networks, or install productivity and entertainment applications on work-issued mobile devices, inadvertently importing proxy monetization frameworks directly into secure institutional zones.
Official Responses and Immediate Institutional Silence
As technical details of the breach circulated throughout the global cybersecurity community, the official response from institutional authorities remained notably delayed.
At the time of publication, the White House had not immediately responded to multiple formal requests for comment regarding the Layer3 Intel and Synthient disclosures. The absence of an immediate public statement reflects the delicate nature of national security incidents involving Executive Office communications networks.
Federal IT and cybersecurity agencies, including the Cybersecurity and Infrastructure Security Agency (CISA) and the Office of the Director of National Intelligence (ODNI), face mounting pressure to initiate sweeping forensic audits across AS2650 and other federal civilian networks. Cybersecurity analysts anticipate that emergency directives may soon be issued to federal agencies requiring the implementation of advanced Endpoint Detection and Response (EDR) agents capable of identifying and blocking residential proxy SDKs, alongside strict enforcement of BYOD prohibitions on sensitive government hardware.
Future Outlook: Remediation and Long-Term Implications
The revelation that the White House network has been functioning as an unwitting proxy relay for foreign-linked and criminal networks marks a watershed moment for federal cybersecurity policy. Moving forward, government security architects must confront several structural challenges to ensure institutional integrity.
1. Zero Trust Architecture and Endpoint Hardening
Traditional perimeter defense models are rendered obsolete when trusted internal endpoints voluntarily establish outbound tunnels to external proxy coordinators. Federal agencies must aggressively accelerate Zero Trust Architecture (ZTA) frameworks, ensuring that continuous validation of device posture, software inventories, and behavioral monitoring is maintained across every connected machine.
2. Elimination of Unvetted SDKs and BYOD Loopholes
Institutional IT policies must evolve to strictly prohibit the installation of consumer software, browser extensions, and mobile applications on any hardware touching classified or sensitive government networks. Enterprise Mobile Device Management (MDM) solutions must be deployed to actively scan for and strip unauthorized applications harboring proxy monetization libraries.
3. Regulatory and Legal Action Against Proxy Resellers
The unfettered commercialization of residential bandwidth—particularly by entities with historical ties to state-sponsored offensive cyber operations—demands rigorous international regulatory intervention. Law enforcement agencies and intelligence communities must target the financial pipelines and legal loopholes exploited by proxy brokers who bypass standard Know Your Customer verifications.
Conclusion
The compromise of White House IP addresses by commercial proxy networks serves as an urgent wake-up call for public and private sector organizations alike. In an interconnected digital economy where bandwidth can be purchased for pennies, the security perimeter is only as strong as the most distracted user’s personal device. Until rigorous software supply-chain controls and aggressive endpoint monitoring are universally enforced across government networks, institutional infrastructure will remain dangerously vulnerable to exploitation by anonymous adversaries.