For years, cybersecurity professionals, law enforcement agencies, and consumer watchdog groups have issued increasingly urgent warnings regarding the hidden dangers of generic, unbranded streaming devices. Marketed heavily across mainstream e-commerce platforms like Amazon, Best Buy, and Newegg, these cheap, uncertified Android TV boxes and streaming sticks promise consumers a tempting shortcut: unlimited access to premium content, live sports, and global television networks for a single, low, up-front fee, entirely bypassing subscription paywalls.
However, beneath the polished user interfaces of these unauthorized devices lies a much darker reality. Security experts have long documented that these boxes secretly monetize their users by routing malicious traffic through their home networks, essentially turning residential internet connections into commercial proxies for anonymous third parties.
Now, groundbreaking new threat intelligence reveals that the exploitation goes far deeper than simple proxy rental. A comprehensive, deep-dive analysis by threat researchers at the cybersecurity firm Bitsight has exposed a sprawling, highly sophisticated ad fraud syndicate. This global operation leverages tens of thousands of popular "H96" streaming devices—widely sold online—to systematically defraud online merchants and advertising networks.
By spoofing their hardware profiles to masquerade as mobile phones built by leading manufacturers such as Samsung, Vivo, Huawei, and Xiaomi, these compromised TV boxes execute automated, precision-crafted ad clicks on a vast network of artificial intelligence (AI)-generated websites. Driven by low-code development frameworks and advanced computer vision systems, the entire architecture operates as a streamlined criminal enterprise. Generating an estimated $50,000 daily from just a fraction of its known infrastructure, this scheme exposes the staggering vulnerabilities hidden inside millions of living rooms worldwide and highlights the dangerous convergence of consumer Internet of Things (IoT) hardware, artificial intelligence, and global digital ad fraud.
Detailed Chronology: Unraveling the H96 Ad Fraud Ecosystem
The investigation into this global botnet did not begin with a traditional malware sample or a random phishing email. Instead, it started with a stroke of investigative luck and sharp threat-hunting methodology executed by Pedro Falé, a threat researcher at Bitsight.
The Expired Domain Breakthrough
The breakthrough occurred when Falé successfully registered an expired domain name that had previously been utilized for telemetry by a popular brand of generic streaming devices known as H96. Historically, this domain served as a silent reporting post, periodically collecting comprehensive hardware diagnostics and a full inventory of every installed application from tens of thousands of H96 streaming sticks deployed in households across the globe.
Upon taking control of the domain, Falé gained an unprecedented window into the operational telemetry of a vast ad fraud network. As the compromised H96 devices continued to check in, expecting their routine communication channel to be active, they flooded the researcher’s infrastructure with data packets. It was during the initial inspection of this inbound traffic that Falé uncovered a glaring, anomalous contradiction.
The Mobile Phone Imposters
"We noticed something was wildly wrong," Falé explained in an interview detailing the discovery. "Multiple devices reporting to this factory Android TV Box backdoor were ‘phones.’"
Upon closer inspection, virtually every single TV box connecting to the domain was transmitting metadata claiming to be a mobile smartphone rather than a stationary, mains-powered Android television accessory. The devices were aggressively spoofing their hardware identifiers, masquerading as popular smartphone models manufactured by industry giants including Samsung, Vivo, Huawei, and Xiaomi.
Further analysis of the applications embedded within these devices exposed the mastermind behind the operation. Every single compromised H96 stick reported having the exact same two pre-installed applications. Code analysis revealed these applications were engineered by Zhejiang Fengwo IoT Technology Ltd, an entity founded in 2019 in mainland China that operates an extensive ad-publishing and software portfolio under the corporate umbrella of the Fengwo Group.
Bitsight’s tracking systems—specifically their proprietary TRACE platform—subsequently traced the financial monetization conduits of the operation through a web of single-person legal shell identities, shell corporations, and financial hubs spanning Hong Kong and Singapore, ultimately leading directly back to the Fengwo Group in mainland China.
The Automated Ad Fraud Machine
Once the connection between the H96 hardware, the spoofed mobile identifiers, and the Fengwo Group was established, Bitsight researchers mapped out the exact mechanics of the ad fraud cycle. The pre-installed applications act as orchestrators, transforming the idle TV boxes into captive, automated traffic generators.
These devices are commanded to visit a sprawling network of AI-generated websites operated by the Fengwo Group. A deep inspection of these web properties revealed a staggering display of automated content creation: the sites feature thousands of machine-generated news articles, blog posts, and digital graphics spanning diverse categories, including finance, health, education, gaming, music, and food culture.
Crucially, Bitsight discovered a strict conditional logic built into these sham web properties: none of the sites would display advertisements unless the visiting browser environment successfully matched the spoofed mobile device profile transmitted by the H96 streaming sticks. By forcing the web servers to believe they were serving ads to genuine mobile phone users browsing on cellular or mobile hardware, the Fengwo Group artificially inflated engagement metrics and fraudulently harvested payouts from unsuspecting digital advertising networks.
Supporting Context & Metrics: Architecture of the Syndicate
To understand the sheer scale and industrial efficiency of the Fengwo Group’s operations, one must examine the technological stack that powers it. The syndicate has successfully automated almost every layer of its cybercriminal enterprise, dramatically reducing operational overhead while maximizing yield.
"AI Digital Humans" and Corporate Facades
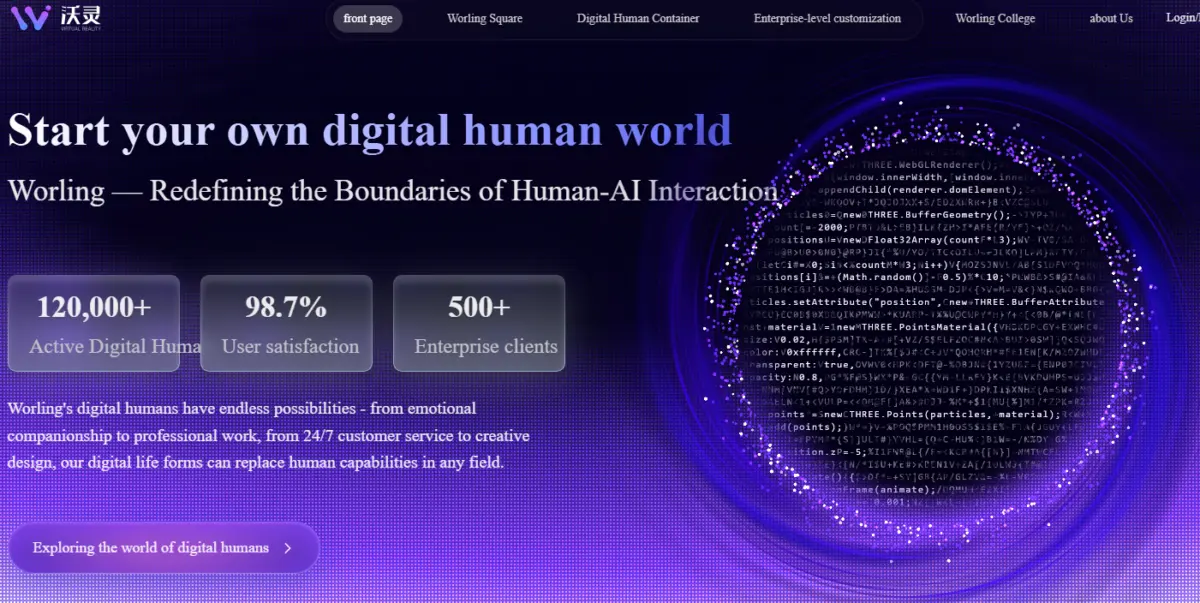
The primary public-facing portal for the enterprise is hosted at the domain fwgcloud[.]com. According to its polished marketing copy, the website claims to be "redefining the boundaries of human-AI interaction," boasting a massive inventory of over 120,000 "AI digital humans" available for rent. These virtual personas are supposedly capable of handling everything from emotional companionship and creative design to 24/7 customer service.
However, security researchers view these grand claims with deep skepticism. Bitsight’s report concludes that the "digital human" ecosystem is likely a sophisticated corporate smoke screen designed to mask the true, illicit nature of the enterprise and divert regulatory or law enforcement scrutiny.
"Historically, when dealing with proxy services or DDoS, we sometimes see these websites undertake inconspicuous facades, so as not to advertise their DDoS capability or botnet size," Falé wrote in the analysis. "This could also be the case here."
Low-Code Crime: The Blockly Integration
Perhaps the most innovative—and alarming—aspect of the Fengwo Group’s infrastructure is its approach to software development and task execution. Infrastructure analysis revealed that the corporate domain shared SSL certificate data with domains tied directly to the phone-spoofing applications found on the H96 devices. Furthermore, an internal wiki platform discovered by Bitsight linked the Fengwo Group directly to a proprietary implementation of Blockly, an open-source visual programming language originally developed by Google to teach children how to write basic software code.
Instead of employing large teams of expensive, highly skilled software engineers to write custom botnet control scripts, the Fengwo Group utilizes Blockly to empower low-skilled operators. By providing a drag-and-drop graphical user interface, the system allows internal operators to assemble complex fraud routines simply by dragging visual blocks of code together—requiring zero deep understanding of the underlying JavaScript or network protocols.
"An operator can drag blocks together in their Blockly editor to define each fraud routine, given a task type," Bitsight’s report details. "Once the routine is saved, it gets exported as JavaScript and uploaded to the S3 buckets. An operator doesn’t need as much understanding of the underlying technicalities, as it is all set in place for ease of use."
Internal developer commentary uncovered by Bitsight confirmed the brilliance of this cost-cutting strategy. One Fengwo developer remarked that "only a small number of highly-skilled developers are needed to build the template execution-unit images," while "developers who create execution units from those templates have significantly lower technical requirements, greatly reducing the company’s operating costs."
Advanced Computer Vision and Human-Like Automation
To bypass modern, sophisticated anti-fraud detection systems employed by ad networks, simple automated script clicks are no longer sufficient. To solve this, the Fengwo Group integrated an advanced automation pipeline that fuses three distinct vision and reasoning systems into a single interface.
When an H96 device receives a task module via its Blockly backend, it silently launches a headless web browser, navigates through multi-page articles, manages browser tabs, and identifies advertisements on the page with human-like precision. The integrated vision systems allow the automated bots to visually locate ad banners, differentiate organic content from sponsored placements, and execute natural mouse movements or screen taps, effectively tricking automated verification filters into validating the fraudulent engagement.
TV On? Proxy. TV Off? Ad Fraud.
One of the most fascinating behavioral patterns uncovered by Bitsight is the duality of the H96 device’s operation. Researchers observed that individual TV boxes never performed residential proxy routing and ad fraud simultaneously. Instead, the devices exhibited a precise, context-aware operational schedule:
When the TV is Powered On: If the hardware detects an active HDMI signal from an attached television—signalling that the human owner is actively using the device to stream media—the box pivots to functioning primarily as a residential proxy, quietly renting out the user’s internet bandwidth to anonymous third parties.
When the TV is Powered Off: The moment the television is turned off, the streaming stick instantly drops its proxy duties and switches over to intensive ad fraud execution, running background browser instances and clicking on AI-generated web advertisements.
Researchers concluded that this resource allocation is a necessary survival mechanism. Ad fraud routines involving headless browsers, computer vision processing, and automated tab management are intensely resource-heavy. If executed while a user was actively trying to stream a high-definition movie or live broadcast, the severe lag, CPU throttling, and bandwidth congestion would immediately alert the owner that something was fundamentally wrong with their device.
Financial Estimates and Scale
By monitoring approximately 38,000 active H96 TV boxes phoning home to a single expired telemetry domain globally, Bitsight calculated a conservative revenue baseline. Based strictly on this limited sample size, the ad fraud network is estimated to haul in approximately $50,000 every single day—a figure that completely excludes the substantial parallel revenues generated by renting out residential proxy bandwidth.
When asked for comment regarding these findings, KrebsOnSecurity attempted to reach the Fengwo Group by emailing the contact address listed on fwgcloud[.]com. The inquiry bounced back immediately with an automated rejection notice: "Your message couldn’t be delivered to postmaster@fwgcloud[.]com. Their inbox is full, or it’s getting too much mail right now."
Supporting Context: The Broader Consumer IoT Crisis
The exposure of the Fengwo Group ad fraud operation underscores a much wider, systemic crisis within the global consumer electronics market. Despite repeated, high-profile warnings issued by the Federal Bureau of Investigation (FBI) and cybersecurity leaders regarding the inherent security risks of cheap, uncertified IoT hardware, major e-commerce platforms continue to enable the distribution of these dangerous devices.
+-----------------------------------------------------------------------+
                THE THREAT LIFECYCLE OF CHEAP STREAMING BOXES
+-----------------------------------------------------------------------+

   [Uncertified Android TV Box] Purchased via Amazon/Newegg/Best Buy
                 |
                 +---> Pre-installed Malware & Backdoors
                 |
                 +---> TV ON (HDMI Active)    ---> Residential Proxy
                 |                                  (Rents IP to Others)
                 |
                 +---> TV OFF (HDMI Inactive) ---> AI Ad Fraud
                                                    (Spoofs Phones,
                                                     Clicks Ads, Generates
                                                     $50,000+ Daily)
+-----------------------------------------------------------------------+
The E-Commerce Blind Spot
Retail giants such as Amazon, Best Buy, and Newegg continue to host hundreds of third-party vendors selling unbranded, dirt-cheap streaming boxes bundled with unofficial, modified builds of the Android operating system. Propelled by online influencers and marketed as cost-effective "jailbroken" solutions to bypass cable bills and streaming subscriptions, these devices find their way into millions of homes.
Once plugged into a home network, these devices present a severe security hazard. Because they are universally shipped without proper security hardening, lack firmware update mechanisms, and are bereft of basic authentication protocols, they serve as wide-open gateways for cybercriminals. In January, proxy tracking service Synthient documented how aggressive botnets, such as the infamous Kimwolf botnet, successfully enslaved millions of similar TV boxes by weaponizing overlapping vulnerabilities in pre-installed residential proxy software and underlying device firmware.
Beyond streaming sticks, security researchers warn that the infection vector extends across the entire ecosystem of cheap consumer smart devices. Digital photo frames, smart home hubs, and budget security cameras from obscure manufacturers have all been routinely found pre-loaded with residential proxy modules and malicious backdoors.
Future Outlook and Recommendations
As threat actors increasingly blend automation, artificial intelligence, and consumer hardware, the digital advertising industry and everyday consumers face a formidable challenge. The ability of operations like the Fengwo Group to weaponize standard household electronics for automated fraud demonstrates that the perimeter of corporate enterprise networks now extends directly into the living room.
Industry and Regulatory Pressure
Pressure is mounting on major e-commerce platforms to institute stricter vetting processes for consumer hardware, particularly devices running modified or uncertified operating systems. Security advocates argue that marketplaces must take active responsibility for policing third-party vendors who dump insecure, pre-infected IoT hardware onto consumers.
Concurrently, major consumer electronics brands are beginning to take defensive action. For instance, companies like LG have recently announced sweeping policy changes—such as banning residential proxy software integration from smart TV application ecosystems—in an effort to curtail the unauthorized monetization of consumer bandwidth.
Actionable Guidance for Consumers
To mitigate the risks posed by compromised streaming boxes and IoT hardware, security experts offer several critical recommendations:
Stick to Reputable Brands: Consumers should strictly avoid unbranded or obscure streaming sticks purchased via third-party online marketplaces. When buying smart TV hardware, stick to established name brands (such as Apple TV, Google TV, Roku, or certified Amazon Fire devices).
Verify OS Certification: Google provides official documentation enabling consumers to verify whether an Android TV device is built with legitimate, secure Android TV OS and Play Protect certification. Uncertified boxes should be disconnected immediately.
Consult Threat Intelligence Lists: Security researchers maintain public resources to help identify compromised hardware. For example, Synthient maintains a continuously updated public registry of known IoT product names and brands that have been documented shipping with pre-installed proxy software and malicious applications.
Isolate IoT Devices: If budget IoT devices or smart home gadgets must be used, network administrators should isolate them onto a restricted guest VLAN (Virtual Local Area Network) completely separate from primary computers, NAS drives, and sensitive personal devices.
The exposure of the Fengwo Group’s AI ad fraud empire serves as a stark reminder: when a consumer hardware product is offered at a price that seems too good to be true, the user is not the customer—they, and their home network, are the product.