Executive Overview
In a stunning escalation of a high-stakes federal cyber investigation, Federal Bureau of Investigation (FBI) agents have arrested a prominent Canadian cybersecurity and ransomware negotiation executive on federal extortion and conspiracy charges. The suspect, identified as 54-year-old Edward Dubrovsky, was taken into custody in Pennsylvania while attending a prominent industry conference.
The arrest is directly tied to an expansive, rapidly evolving federal probe into ShinyHunters, a notorious cybercriminal syndicate that has plagued global enterprises and recently achieved the unprecedented feat of breaching the FBI itself. According to federal court documents and multiple independent sources, ShinyHunters managed to exfiltrate sensitive personal, medical, and operational data concerning thousands of federal law enforcement agents.
The federal investigation—now centralized within an FBI field office in Texas—is widening rapidly. It highlights a murky, high-risk intersection in the cybersecurity sector where firms specializing in ransom negotiations, incident response, and cyber insurance intersect with the very threat actors they are hired to neutralize. With court documents heavily sealed, key suspects cooperating, and international law enforcement agencies actively seizing hardware across jurisdictions, the unfolding scandal threatens to expose structural vulnerabilities within the multi-billion-dollar ransomware advisory industry.
Detailed Chronology: From the Philadelphia Summit to Federal Custody
The Arrest in Pennsylvania
The sequence of events leading to Dubrovsky’s apprehension began during the early days of October 2026. Dubrovsky, a well-known figure in the Canadian cybersecurity community and an authority on cyber extortion, traveled to Philadelphia, Pennsylvania, to participate in the annual Cyber Risk Summit held at the Loews Philadelphia Hotel from October 5 to October 7.
The conference, hosted by NetDiligence, drew a wide array of cyber insurance professionals, risk assessors, and security executives. Among the premier sponsors of the event was Cypfer, a Canadian security firm specializing in ransomware advisory services, alongside CyberSteward, another boutique Canadian security firm with which Dubrovsky was recently affiliated.
On October 8—just one day after the conclusion of the summit—federal agents moved in. Court records indicate that an individual named Edward Dobrovsky (with a minor spelling variation in the last name) was arrested and booked into a federal detention facility in Philadelphia.
Shifting Jurisdictions and Charges
Initial filings in federal court charged the defendant with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." While the primary core complaint and several supporting documents remain sealed by the court, a docket summary indexed via CourtListener reveals the gravity of the charges.
On October 9, U.S. judicial authorities executed a procedural transfer, moving the case file to the Eastern District of Texas. According to multiple knowledgeable sources, the Texas federal court has been designated as the central epicenter for the nationwide, multi-jurisdictional investigation into the ShinyHunters hacking ring. As of this writing, Dubrovsky is being held in a federal facility in Philadelphia, and public records indicate he has yet to retain legal counsel or have a public defender formally appointed.

Corporate Disclaimers and Professional Background
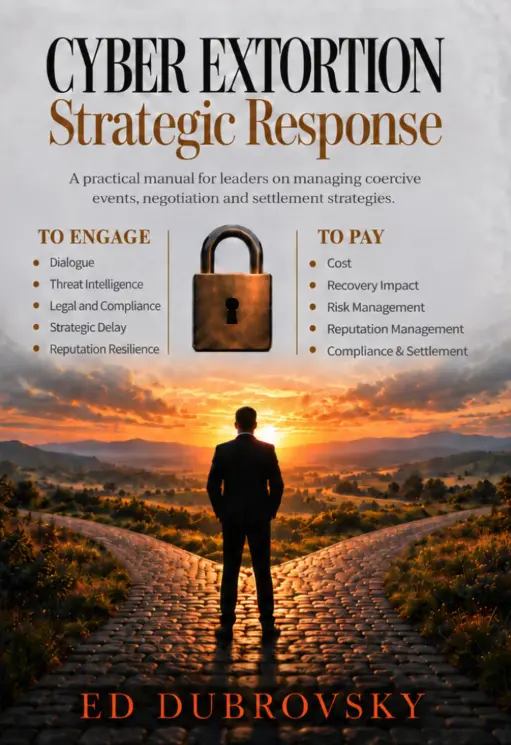
Dubrovsky’s arrest sent shockwaves through the tightly knit community of incident response professionals. Prior to his arrest, Dubrovsky maintained a visible public profile, frequently commenting on strategies for handling coercive cyber threats and authoring a 252-page manual titled Cyber Extortion Strategic Response. The book purported to guide organizations through the complex nuances of communicating with malicious actors without crossing legal boundaries or committing to illegal ransom payouts.
On LinkedIn, Dubrovsky was listed as an "ex-founder" of Cypfer, though that claim quickly drew corporate pushback. On October 10, a spokesperson for Cypfer issued a clarifying statement asserting that Dubrovsky was never a founder or co-founder of the firm, but rather served in the capacity of managing director prior to his resignation in November 2025. Following his departure from Cypfer, Dubrovsky transitioned to CyberSteward, where he continued to consult on global extortion advisory services and planned promotional appearances at the Philadelphia risk summit.
Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To fully understand the gravity of Dubrovsky’s arrest, one must examine the operational blueprint and recent trajectory of the ShinyHunters syndicate.
Modus Operandi and Financial Impact
ShinyHunters has long operated as one of the cybercriminal underground’s most disciplined and damaging data-extortion syndicates. The group typically relies on sophisticated spear-phishing campaigns, credential stuffing, and the systematic theft of active login credentials from corporate accounts at software-as-a-service (SaaS) providers. Once inside a network, the group exfiltrates vast repositories of proprietary and personally identifiable information (PII), subsequently leveraging public data-leak sites to coerce corporate leadership into paying exorbitant ransoms.
Federal estimates underscore the staggering financial toll exacted by the group. According to official FBI data, ShinyHunters and its associated cells have successfully extorted more than $70 million from corporate and institutional victims globally over the course of the year alone.
The Breach of the FBI
What elevates the ShinyHunters investigation from a standard corporate extortion case to a national security crisis is the group’s audacious targeting of federal law enforcement infrastructure. Last month, sources confirmed that the syndicate successfully compromised an online recruitment portal maintained by the FBI.
The stolen cache included deeply sensitive records belonging to thousands of active agents and applicants. Compromised fields reportedly detailed:
- Specific operational units and specialized law enforcement credentials.
- Detailed personal backgrounds, including confidential medical records.
- Psychiatric evaluations and clearance documentation.
This brazen theft not only compromised the personal security of federal personnel but also invited an unprecedented, all-hands-on-deck response from the U.S. intelligence and law enforcement apparatus.

International Raids and the Fall of "Rey"
The dragnet catching Dubrovsky is part of a broader, synchronized international offensive against cybercrime syndicates.
- The Dutch Arrests: In late September 2026, Dutch national police executed a series of raids resulting in the arrest of Pepijn van der Stap, a reformed hacker and cybercriminal linked directly to the ShinyHunters infrastructure. Law enforcement agencies immediately began poring over digital devices and hardware seized during Van der Stap’s arrest.
- The Rise and Fall of "Rey": Following Van der Stap’s capture, leadership within the volatile syndicate shifted. A hacker operating under the alias Rey assumed operational control of ShinyHunters. "Rey" quickly made headlines by aggressively taunting FBI Director Kash Patel and federal investigators on social media regarding the bureau’s compromised personnel records.
- Identification of the Teenager: Investigative journalism by Reuters, corroborated by specialized cybersecurity tracking, unmasked "Rey" as a teenager named Saif Al-din Khader. On October 7, federal investigators apprehended Khader as the syndicate attempted to orchestrate an extortion campaign against a digital aviation and navigation unit recently divested by aerospace giant Boeing. Reports indicate that Khader is currently cooperating with federal authorities, providing a wealth of intelligence that is accelerating secondary arrests—including, potentially, individuals within the ransomware negotiation sector.
Official Statements and Industry Fallout
The arrest of a high-profile cybersecurity executive on extortion charges has exposed a troubling undercurrent within the multi-billion-dollar incident response industry. For years, critics have raised ethical and legal questions regarding the unregulated ecosystem of third-party negotiators who act as intermediaries between Fortune 500 companies and cybercriminal gangs.
While federal authorities—including FBI Director Kash Patel—have confirmed major developments via brief public statements on social media platforms like X (formerly Twitter), the broader apparatus of the Department of Justice has maintained a tight-lipped posture. The FBI officially declined to comment on the specifics of Dubrovsky’s indictment, citing the ongoing, fluid nature of the multi-district investigation.
Industry groups, cyber insurance underwriters, and incident response firms are now grappling with the fallout. The realization that individuals trusted with corporate crisis management or extortion advisory services may have crossed ethical and legal boundaries threatens to prompt stringent regulatory oversight. Compliance-driven frameworks governing ransom payments, third-party broker disclosures, and mandatory reporting are expected to undergo severe legislative scrutiny in the wake of these revelations.
Future Outlook: What Lies Ahead
As this high-profile case moves through the federal court system, several critical trajectories will define the coming weeks and months:
- Further Indictments Anticipated: Multiple sources close to the investigation indicate that the charges against Dubrovsky are unlikely to be isolated. Federal prosecutors in the Eastern District of Texas are reportedly preparing additional indictments targeting principals and operatives at other boutique firms specializing in ransomware negotiation and alternative dispute resolution.
- Exploitation of Cooperative Intelligence: With both Saif Al-din Khader ("Rey") and potentially other detained affiliates cooperating with federal handlers, the FBI possesses an unprecedented roadmap of the ShinyHunters financial ledger, communication channels, and money-laundering networks.
- Litigation and Defense Strategy: Once Dubrovsky is formally arraigned and defense counsel is appointed, legal battles will undoubtedly center on the interpretation of "negotiation versus extortion," testing the boundaries of how federal anti-extortion statutes apply to commercial intermediaries operating in high-stakes cyber crisis environments.
This remains a rapidly developing, fast-moving story. As court seals are lifted and additional indictments are unsealed, further updates will follow.