Executive Overview
In a dramatic escalation of one of the most high-profile federal investigations in recent memory, federal law enforcement agents have arrested a prominent Canadian cybersecurity executive on charges tied to the notorious ShinyHunters cybercrime syndicate. The bust comes on the heels of a humiliating security breach that saw the hacking collective siphon sensitive, classified data belonging to thousands of Federal Bureau of Investigation (FBI) personnel.
The suspect, identified in unsealed federal documents as 54-year-old Edward Dubrovsky, was apprehended in Pennsylvania while attending a high-profile cyber insurance conference. Dubrovsky, a well-known figure in the specialized ecosystem of ransomware mitigation and extortion advisory, stands accused of cyber extortion and conspiracy. His arrest offers a rare, unsettling glimpse into the shadowy intersection where corporate incident response firms, ransomware negotiators, and elite cybercriminal enterprises collide.
The investigation—now heavily centralized within a specialized FBI field office in Texas—underscomes a profound structural shift in how federal authorities are targeting the international cyber extortion economy. Rather than merely chasing the teenagers and initial access brokers deploying phishing links, federal prosecutors are increasingly casting a wider net, scrutinizing the ecosystem of intermediaries, advisors, and corporate negotiators who manage multi-million-dollar ransom payouts. With the ShinyHunters collective pulling in upwards of $70 million in illicit extortions this year alone, the arrest of a veteran ransomware advisor signals that the Department of Justice is treating the broader auxiliary economy of cybercrime as an active co-conspirator to extortion.
Detailed Chronology: From Philadelphia to the Federal Courts
The sequence of events leading to Dubrovsky’s apprehension reads like a modern techno-thriller, moving rapidly from academic panels on cyber risk management to the austere halls of a federal detention facility.
The Cyber Risk Summit: A Miscalculated Appearance
Between October 5 and October 7, 2026, the Loews Philadelphia Hotel played host to the annual Cyber Risk Summit, a premier gathering for professionals in the cyber insurance, risk mitigation, and incident response sectors. The conference featured numerous industry heavyweights and corporate sponsors, most notably Cypfer, a Canadian security company specializing in handling ransomware negotiations, alongside another participating firm, CyberSteward.
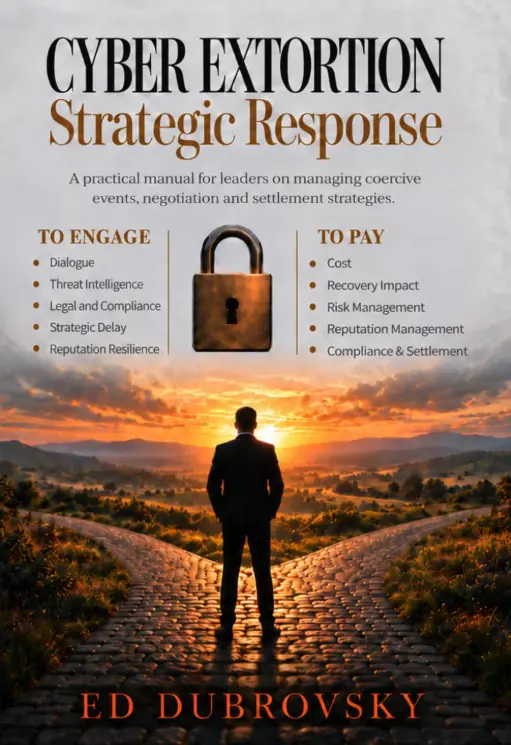
Dubrovsky, a veteran of the Canadian cybersecurity circuit and the author of a comprehensive 252-page manual titled Cyber Extortion Strategic Response, was in attendance. Having previously held a leadership role at Cypfer—though company representatives later clarified his exact corporate lineage, noting he served as a managing director before resigning in November 2025—Dubrovsky had promoted his attendance on LinkedIn weeks prior. He wrote enthusiastically about continuing industry conversations concerning "strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services."
The Arrest and Legal Maneuvering
Unbeknownst to Dubrovsky and his peers, federal agents had been closing in. On October 8—just as the Philadelphia summit concluded—federal court records show that an individual under the name Edward Dobrovsky (reflecting a slight typographical error in early filings) was taken into custody by FBI agents in Pennsylvania.
Initial court documents, though heavily redacted and largely sealed, paint a striking picture of the charges. A summary indexed via legal transparency platform CourtListener charges the executive with:
- "Conspiracy to threaten to impair the confidentiality of information with the intent to extort money"
- "Interference with commerce by threats"
Following his arrest, Dubrovsky was temporarily processed and held at a federal facility in Philadelphia, according to the U.S. Bureau of Prisons inmate locator. However, legal maneuvering by the government was swift. On October 9, a formal notice was filed transferring jurisdiction of the case to the Eastern District of Texas, which sources close to the investigation confirm has become the epicenter and nerve center for the sprawling, multi-jurisdictional federal crackdown on the ShinyHunters network.

As of press time, Dubrovsky has not secured private legal representation, nor has the court officially appointed a public defender to manage his defense. Requests for comment directed to executives at CyberSteward and Dubrovsky’s professional network went unanswered.
Supporting Context & Metrics: The Reign and Reach of ShinyHunters
To understand the gravity of Dubrovsky’s arrest, one must contextualize the sheer operational scale and brazenness of the ShinyHunters hacking collective, alongside the mounting pressures facing federal law enforcement.
The FBI Data Heist and the Rise of "Rey"
The friction between ShinyHunters and the FBI reached a fever pitch in the weeks prior to the operation. Following the September arrest of reformed hacker Pepijn van der Stap by Dutch law enforcement in connection with the ShinyHunters probe, leadership of the hacking group shifted. A shadowy figure operating under the moniker "Rey" assumed operational control.
Rather than running for cover, Rey and his associates launched a retaliatory digital offensive against federal authorities. The group successfully breached the FBI’s online recruitment portal, extracting deeply sensitive dossiers containing:
- Personnel unit alignments and specialized training data
- Internal security clearance metrics
- Confidential medical and psychiatric records of thousands of agents
The psychological and operational impact on the Bureau cannot be overstated. The breach of federal agent data by a hostile syndicate forced an aggressive, all-hands-on-response, mobilizing federal resources on an unprecedented scale.
Identifying "Rey": The Fall of Saif Al-din Khader
The hubris of the collective’s new leadership proved to be its undoing. Investigative reporting by Reuters and specialized cybersecurity publications revealed that "Rey" was actually a teenager named Saif Al-din Khader. Khader’s operational downfall was cemented when the group attempted a high-stakes extortion campaign targeting a navigation and digital aviation unit recently divested by aerospace giant Boeing in late 2025.
Federal authorities quickly closed the net on Khader, who was detained and is reportedly cooperating extensively with FBI investigators. The data recovered from devices seized during the Van der Stap raid in the Netherlands, combined with Khader’s digital footprint and subsequent cooperation, provided investigators with the forensic breadcrumbs that ultimately connected external threat actors to the corporate advisory ecosystem—paving the way for Dubrovsky’s arrest.
The Economics of Extortion
ShinyHunters has historically specialized in sophisticated phishing campaigns, credential theft, and unauthorized data exfiltration from Software-as-a-Service (SaaS) providers. Once corporate or institutional data is safely in their possession, the group leverages public shaming sites to pressure executives into meeting multi-million-dollar ransom demands under the threat of public disclosure.
According to preliminary intelligence metrics released by federal law enforcement, the economic footprint of the collective is staggering:

- Total Extortion Yield (2026 YTD): Estimated to exceed $70 million across various corporate and institutional victims.
- Primary Vectors: SaaS environment compromises, credential stuffing, and supply-chain digital intrusions.
- Target Scope: Ranging from commercial aviation suppliers to federal law enforcement recruitment databases.
Official Statements and Industry Fallout
The silence from official federal channels has been deafening, interspersed with brief, calculated confirmations. While FBI Director Kash Patel acknowledged the general apprehension of suspects assisting the ShinyHunters network via social media statements, the Bureau has officially declined to comment on the specifics of Dubrovsky’s ongoing prosecution, citing the active, fluid nature of the grand jury proceedings.
Meanwhile, the cybersecurity and incident response sectors are experiencing an existential reckoning. Firms that specialize in ransomware negotiation have long operated in a murky ethical and legal grey zone. While companies market themselves as compliance-driven advisors helping distressed organizations minimize downtime, recover operational assets, and safely navigate complex extortion events, critics have long warned that the multi-billion-dollar ransom negotiation industry inadvertently fuels the criminal business model.
In his published work, Cyber Extortion Strategic Response, Dubrovsky famously drew a sharp semantic line between communication and capitulation. An excerpt from the book’s marketing material notes:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Prosecutors, however, appear poised to challenge the boundaries of these theoretical frameworks in a court of law. Investigators are actively examining whether certain advisory personnel crossed the legal threshold from objective crisis management into active facilitation, financial laundering, or collusion with criminal enterprises.
Future Outlook: A Turning Point in Cyber Enforcement
The arrest of Edward Dubrovsky is unlikely to be an isolated incident. Sources close to the federal probe have indicated that as the Eastern District of Texas spearheads the consolidated investigation, additional criminal charges against principals at other ransomware negotiation and incident response firms may be forthcoming.
This development signals a profound paradigm shift in global cyber law enforcement. For decades, the conventional strategy focused almost exclusively on tracking down the physical hackers—often young individuals hidden behind VPNs in foreign jurisdictions with little to no extradition treaties with the United States. By moving upstream to target the financial, advisory, and corporate intermediaries who populate the ransomware negotiation pipeline, the Department of Justice is systematically dismantling the infrastructure that makes cyber extortion profitable and viable.
As this fast-moving, high-stakes story continues to develop, the global cybersecurity community watches with bated breath. The trial of Edward Dubrovsky—and the broader fallout from the ShinyHunters FBI data breach—will likely establish critical legal precedents regarding the liabilities of corporate incident responders, redefining the rules of engagement for companies caught in the crosshairs of digital extortion.
This is a developing story. Updates, court filings, and official statements will be appended as new information becomes available.