Executive Overview
In a stunning escalation of an already unprecedented federal investigation, the Federal Bureau of Investigation (FBI) has apprehended a prominent Canadian cybersecurity executive in Pennsylvania on federal cyber extortion and conspiracy charges. The arrest is tied directly to the sprawling, high-stakes federal probe into ShinyHunters, a notorious cybercrime collective that recently pulled off one of the most embarrassing breaches in law enforcement history—siphoning sensitive personnel records, security clearances, and psychiatric profiles of thousands of FBI agents.
The suspect, identified in federal court records as Edward Dubrovsky (spelled "Dobrovsky" in initial filings), is a veteran figure in the cybersecurity industry. A prolific author, conference speaker, and former executive at prominent Canadian security firms specializing in ransomware negotiations, Dubrovsky was taken into custody while attending a major cyber insurance conference in Philadelphia.
The operation marks a critical inflection point in the U.S. government’s retaliation against the extortion ring. Over the past year, ShinyHunters has amassed over $70 million in ransom payments through aggressive cloud-siphoning operations, culminating in a direct digital assault on the Bureau itself. As the investigation consolidates under the Eastern District of Texas, federal authorities are signaling that the boundaries between legitimate incident response firms and the cybercrime underworld may be blurred, raising profound compliance and ethical questions for the global cyber-insurance and ransomware negotiation sector.
Detailed Chronology of Events
The Philadelphia Summons: October 5–7, 2026
The operational net began to tighten in early October during the annual Cyber Risk Summit hosted at the Loews Philadelphia Hotel. The event brought together global leaders in cyber insurance, legal compliance, and incident response. Among the major sponsors was Cypfer, a Canadian security firm, and CyberSteward, a boutique consultancy associated with Dubrovsky.
Dubrovsky had publicly announced his attendance on LinkedIn weeks prior, promoting panels focused on "strategy and compliant-driven coercive (ransomware, extortion) advisory, negotiations, and settlement services." However, unknown to conference attendees, federal law enforcement had already laid the groundwork for his apprehension.
The Arrest and Legal Maneuvering: October 8–9, 2026
On October 8, 2026, federal agents executed the arrest. Court documents filed in Pennsylvania under the name Edward Dobrovsky charged the 54-year-old executive with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
While the core complaint and major evidentiary affidavits remain heavily redacted or completely sealed, public dockets indexed via CourtListener illuminate the severity of the charges. Initially detained at a federal facility in Philadelphia under the U.S. Bureau of Prisons inmate locator, Dubrovsky’s case was swiftly transferred on October 9 to the U.S. District Court for the Eastern District of Texas—the newly minted epicenter of the nationwide ShinyHunters task force. As of press time, Dubrovsky has not secured private legal counsel, and a public defender has yet to be formally appointed by the court.

The Broader International Sweep
Dubrovsky’s arrest does not occur in a vacuum; it is part of a synchronized international dragnet targeting the core infrastructure and facilitators of ShinyHunters.
- The Dutch Raid: In September 2026, Dutch national police arrested reformed hacker and cybercriminal Pepijn van der Stap in connection with the ShinyHunters probe. Investigators immediately began combing through physical and digital devices seized during the raid, seeking links between the group’s leadership and external advisory firms.
- The Fall of "Rey": Immediately following Van der Stap’s detention, a volatile faction leader using the handle "Rey"—later identified by Reuters and security researchers as a teenager named Saif Al-din Khader—assumed operational control of ShinyHunters. In a brazen display of defiance, Rey began taunting FBI Director Kash Patel and agency officials online regarding the theft of deep intelligence from the Bureau’s recruitment portal.
- The Boeing Spinoff Extortion: Khader’s digital reign was short-lived. On October 7, security analysts detailed how Rey was apprehended by law enforcement as the group attempted to execute an extortion campaign against a major digital aviation and navigation unit recently divested by Boeing in late 2025. Khader is currently cooperating with federal investigators.
Supporting Context & Metrics: The Mechanics of ShinyHunters
To understand the gravity of Dubrovsky’s alleged involvement, one must examine the operational modus operandi of ShinyHunters and the booming, multi-billion-dollar economy of ransomware negotiation.
The Threat Matrix
ShinyHunters relies primarily on sophisticated phishing campaigns, credential harvesting, and compromised API keys to breach corporate environments, Software-as-a-Service (SaaS) providers, and cloud repositories. Once inside, they exfiltrate massive volumes of proprietary intellectual property and personal identifiable information (PII), threatening public exposure unless exorbitant cryptocurrency ransoms are fulfilled. According to intelligence compiled by federal law enforcement, the group has successfully extorted over $70 million from corporate and institutional victims globally in 2026 alone.
The FBI Data Breach
The group crossed a critical red line when they successfully compromised the FBI’s online recruitment infrastructure. The stolen cache included:
- Detailed unit assignments and tactical specializations of active-duty agents.
- Highly sensitive medical histories and psychiatric evaluations.
- Security clearance verification data.
This breach prompted an unprecedented mobilization of federal cyber-units, shifting the investigation from a routine criminal probe to a matter of national security.
The Suspect’s Profile and the "Negotiation" Grey Zone
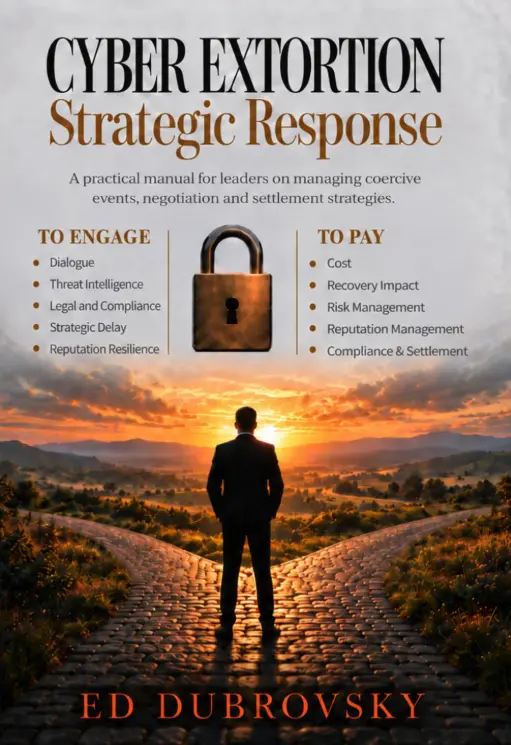
Edward Dubrovsky was widely recognized as an authority in the niche field of ransomware mediation. He authored Cyber Extortion Strategic Response, a 252-page volume marketed as a manual to help organizations navigate the psychological and tactical labyrinth of criminal extortion.
An excerpt from the book’s marketing material highlights the delicate legal tightrope walked by incident responders:

"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, federal prosecutors appear to believe Dubrovsky’s activities crossed the legal divide separating legitimate incident response advisory from active criminal conspiracy, material support, or money laundering—a frontier that investigators are increasingly scrutinizing across the entire cyber-incident response industry.
Official Statements and Institutional Reactions
Official commentary regarding the arrest has been tightly guarded, reflecting the sensitivity of an active, multi-jurisdictional national security investigation.
- The FBI: FBI Director Kash Patel acknowledged the ongoing crackdown via social media platform X (formerly Twitter), celebrating operational milestones without naming specific defendants. The Bureau’s press office has officially declined to comment on the specifics of the Dubrovsky indictment, citing the ongoing judicial proceedings in the Eastern District of Texas.
- Corporate Responses: Following initial media reports linking the arrest to conference attendees, corporate distancing was swift. A spokesperson for Cypfer formally clarified Dubrovsky’s employment history, pushing back against LinkedIn claims that he was a foundational co-founder, clarifying instead that he served purely as a managing director prior to his resignation in December 2025. Representatives for CyberSteward, the firm Dubrovsky joined post-Cypfer, have not yet issued a public statement regarding the arrest of their associate.
Future Outlook: Industry Fallout and Regulatory Realities
The arrest of a high-profile ransomware negotiation executive marks a seismic shift for the cybersecurity and cyber-insurance sectors. For years, the industry operated in a regulatory grey zone, where paying ransoms through third-party intermediaries was viewed as a pragmatic, if unsavory, business necessity to mitigate catastrophic operational downtime.
As the Department of Justice and the FBI centralize the ShinyHunters investigation in Texas, legal experts predict several major developments in the near term:
- Increased Scrutiny on Incident Response Firms: Federal authorities are actively reviewing the digital trails and financial transactions of multiple boutique ransomware negotiation firms. Sources indicate that additional charges against principals at other advisory companies may be forthcoming.
- Stricter Compliance Mandates: Insurance carriers and corporate boards will likely face intensified regulatory pressure regarding how ransomware payments are authorized, tracked, and reported to the Treasury Department’s Office of Foreign Assets Control (OFAC).
- The Erosion of Anonymity in Extortion: With key threat actors like Saif Al-din Khader cooperating and critical intermediaries sitting in federal detention facilities, the structural anonymity that once protected international cybercrime syndicates is rapidly eroding.
As this fast-moving story continues to develop, the intersection of cybersecurity defense, corporate extortion advisory, and federal prosecution will remain at the forefront of the global digital security landscape.
Updates to this developing story will be appended with timestamps as new court documents and official statements become available.