Executive Overview
For years, cybersecurity professionals and intelligence agencies have warned consumers about the hidden costs of cheap, generic TV streaming boxes. Marketed aggressively across mainstream e-commerce platforms—including Amazon, Best Buy, and Newegg—these unbranded or off-brand media players promise “unlimited, free content” and “unlocked” live broadcasts for a single, low, upfront fee. Yet security researchers have long cautioned that these devices secretly act as Trojan horses, commandeering consumer internet connections and renting them out to unknown third parties.
Now, groundbreaking new research exposes a far more sinister and lucrative enterprise. A deep-dive technical analysis conducted by threat researchers at cybersecurity firm Bitsight reveals that these generic streaming sticks do not merely siphon off bandwidth. Instead, they operate as active nodes in a vast, automated ad fraud empire.
Disguising themselves as high-end mobile phones from major manufacturers like Samsung, Huawei, and Xiaomi, tens of thousands of these devices are programmed to silently visit AI-generated web pages and click on digital advertisements. Orchestrated by a mainland Chinese entity known as the Fengwo Group, this sprawling scheme generates an estimated $50,000 every single day from just a fraction of its total footprint.
This comprehensive investigation explores the architecture of the ad fraud network, the clever use of consumer software tools for malicious automation, the dual-action behavior of the botnet hardware, and the systemic regulatory and retail failures that allow these compromised electronics to flood the global market.
Detailed Chronology: Unmasking the H96 Ad Fraud Operation
The unraveling of this global scheme began not with a high-tech government raid, but with a piece of digital real estate: an expired domain name.
The Discovery of the Expired Telemetry Domain
Pedro Falé, a threat researcher at Bitsight, stumbled upon the inner workings of the ad fraud network almost by accident. He managed to register an expired domain name that had previously been utilized for telemetry data collection by a wildly popular brand of generic Android TV boxes known as the H96.

When H96 streaming sticks are plugged into television sets around the globe, they routinely phone home to coordinate updates, check connectivity, and report hardware metrics. By securing the defunct domain, Falé suddenly found himself peering directly into the command-and-control infrastructure of a major botnet.
Upon inspecting the incoming telemetry traffic, Falé noticed an immediate and glaring discrepancy. Thousands of devices reporting into the factory Android TV box backdoor were claiming to be something entirely different: mobile phones.
“We noticed something was wildly wrong,” Falé recalled. “Multiple devices reporting to this factory Android TV Box backdoor were ‘phones.’”
A closer examination revealed that these hardware devices—which physically sat plugged into television HDMI ports—were spoofing device profiles belonging to popular smartphone manufacturers, including Samsung, Vivo, Huawei, and Xiaomi.
Tracing the Culprit: The Fengwo Group
Digging deeper into the payload, Falé identified two pre-installed applications present across all the reporting H96 devices. Metadata and code analysis traced these applications back to a mainland China-based entity founded in 2019: Zhejiang Fengwo IoT Technology Ltd, which operates an extensive portfolio of ad-publishing networks under the umbrella name Fengwo Group.
Subsequent OSINT (Open Source Intelligence) investigations revealed that the Fengwo Group had registered multiple patents matching the exact functional code embedded within the malicious apps found on the streaming boxes.
According to Bitsight’s formal report, the operation was carefully obscured behind a web of legal complexity. The group utilized various single-person shell companies and corporate fronts registered in Hong Kong and Singapore to collect ad monetization revenues, insulating the core mainland Chinese operators from direct liability.

AI-Generated Landing Pages and the Illusion of "Digital Humans"
Once inside the telemetry stream, Bitsight mapped out how the infrastructure functioned. The H96 devices were being used as a captive, un-blockable traffic source to artificially inflate engagement metrics on a network of automated, AI-generated websites operated by the Fengwo Group.
These websites spanned a wide variety of bland, generic niches, ranging from finance and health blogs to music, gaming, and education portals. Built with machine-generated news articles and synthetic graphics, these pages shared a distinct anomaly: they entirely refused to display advertisements unless the visiting browser matched the specific, spoofed mobile profiles transmitted by the H96 TV boxes.
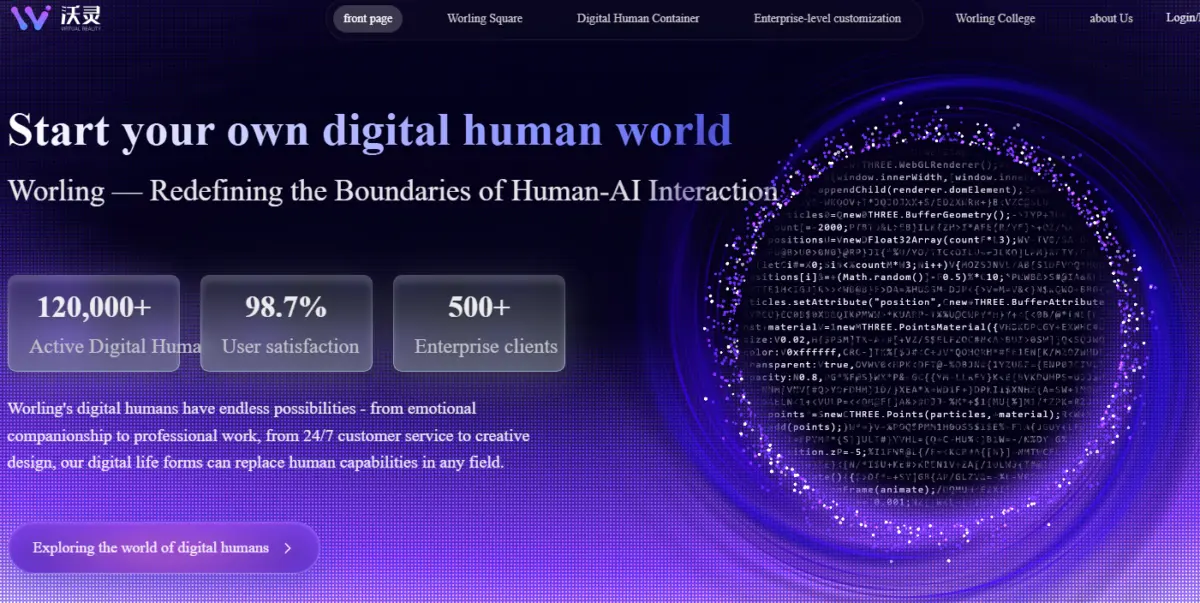
Curiously, the primary corporate domain for the Fengwo Group—fwgcloud[.]com—presented an entirely different face to the public. The homepage claimed that the enterprise was “redefining the boundaries of human-AI interaction,” boasting a portfolio of over 120,000 rentable “AI digital humans” designed for everything from emotional companionship to 24/7 customer service and creative design.
However, Bitsight concluded that this futuristic façade was likely a clever diversion. Historically, botnet operators and proxy services frequently wrap their operations in innocuous corporate skins to obscure the true nature of their underlying infrastructure—whether that is distributed denial-of-service (DDoS) capabilities or massive ad fraud botnets.
Supporting Context & Metrics: Engineering Fraud at Scale
Running a global ad fraud network that spoofs tens of thousands of devices requires sophisticated automation. To minimize labor costs and scale operations efficiently, the Fengwo Group turned to an unexpected tool: children’s programming languages.
Democratizing Malware Construction via Google Blockly
According to Bitsight’s telemetry and internal wiki platform discoveries tied to the Fengwo Group, operators relied on a proprietary implementation of Blockly—a Google-built visual programming language originally designed to teach children how to write code by dragging and dropping visual blocks.
Rather than requiring teams of highly skilled software engineers to write custom exploit routines from scratch, the Fengwo Group used Blockly to build a modular web-app builder. Low-skilled operators could simply drag operational blocks together in a web-based editor to define specific ad-fraud tasks.

- Task Definition: Operators configured workflows that included silently launching background web browsers, navigating through URLs, browsing sub-pages, managing multiple browser tabs, and precisely targeting advertisements.
- Code Export: Once the routine was saved, the visual blocks were automatically exported as executable JavaScript and uploaded to Amazon S3 buckets for distribution.
- Cost Efficiency: As noted by one Fengwo Group developer in internal communications discovered by researchers, this modular architecture meant “only a small number of highly-skilled developers are needed to build the template execution-unit images,” while lower-skilled workers could handle day-to-day operations, dramatically reducing overhead costs.
Computer Vision and Human-Like Interaction
Ad-fraud networks are routinely hunted down by sophisticated anti-fraud algorithms deployed by major advertising networks. To evade detection, automated bots must mimic human behavior with absolute precision.
The Fengwo Group solved this problem by fusing three separate computer vision and reasoning systems into a single interface. When an H96 device was selected for a fraud task, it downloaded the appropriate Blockly module. The system then utilized these vision models to scan the AI-generated web page, accurately identify the physical placement of an ad banner, and execute mouse-like interactions—such as scrolling, pausing, and clicking—just as a real human user would.
Dual-Purpose Hardware: TV On vs. TV Off
One of the most fascinating discoveries made by Bitsight researchers was the operational dichotomy of the H96 streaming sticks. The devices never performed residential proxy relaying and ad fraud simultaneously.
Instead, the botnet operators programmed the hardware to recognize human usage patterns:
- Television ON (HDMI Active): When the box detects an active HDMI signal from the television—signaling that the human owner is actively using the device to stream videos or watch broadcasts—it pauses its resource-intensive ad fraud routines and switches entirely to acting as a residential proxy.
- Television OFF (Standby): The moment the user turns off the television, the box drops its proxy duties and pivots aggressively into running ad-fraud jobs, background browsing, and automated ad-clicking campaigns.
Researchers believe this careful balancing act is designed to prevent the ad fraud scripts from consuming CPU cycles and network bandwidth, which would otherwise degrade streaming performance and alert the owner that something was deeply wrong with their hardware.
Official Statements & Industry Warnings
The exposure of the Fengwo Group ad fraud operation underscores a broader, systemic crisis within the consumer Internet of Things (IoT) marketplace. For years, government agencies and cybersecurity watchdogs have sounded the alarm regarding unverified smart devices.
The FBI Warning on Consumer IoT
In official cybersecurity advisories, the Federal Bureau of Investigation (FBI) has explicitly warned American consumers about the dangers of using unverified home internet-connected devices. The agency highlighted that cheap, unbranded IoT hardware frequently ships pre-infected with malicious software designed to facilitate cybercrime, including distributed proxy networks, credential stuffing attacks, and financial fraud.

Despite these government alerts, major online retailers continue to list and sell thousands of off-brand media players. These devices often bundle unverified, unpatched modifications of Google’s Android operating system, bypassing official security architectures like Google Play Protect.
The Residential Proxy Epidemic
Ad fraud is only half the battle. Universal across these cheap streaming boxes is the pre-installation of residential proxy software. This software rents out the homeowner’s residential IP address to anonymous third-party buyers.
While some buyers are benign market research firms, others include aggressive web-scrapers, digital ticket scalpers, and transnational cybercrime syndicates seeking to route malicious traffic through residential connections to evade geo-blocking and law enforcement blacklists.
Furthermore, because these devices are built cheaply and lack basic authentication protocols, they often suffer from severe, unpatchable vulnerabilities. Earlier this year, proxy-tracking firm Synthient documented how aggressive botnets—such as the infamous Kimwolf botnet—scanned the public internet and rapidly enslaved millions of insecure TV boxes by exploiting vulnerabilities in both the pre-installed proxy applications and the underlying device firmware.
Financial Impact and Global Scale
Quantifying the exact monetary scale of global ad fraud is notoriously difficult, but Bitsight’s telemetry provides a chilling baseline.
By tracking approximately 38,000 active TV boxes globally that were still phoning home to the single expired Fengwo Group telemetry domain, researchers conservatively estimated that this specific branch of the ad fraud network generates close to $50,000 per day in fraudulent ad revenue.
Crucially, this figure does not include:

- Revenues generated through the residential proxy side of the business.
- Traffic routed through other, unexpired infrastructure domains operated by the Fengwo Group.
- Scale achieved by competing botnets operating identical business models on other brands of unvetted TV sticks.
When researchers at KrebsOnSecurity attempted to reach out to the Fengwo Group for comment via the contact address listed on fwgcloud[.]com, the email immediately bounced back with an automated notification:
“Your message couldn’t be delivered to postmaster@fwgcloud[.]com. Their inbox is full, or it’s getting too much mail right now.”
Whether overwhelmed by security inquiries or simply automated to ignore external correspondence, the Fengwo Group offered no defense against the findings.
Future Outlook & Consumer Defense Strategies
The convergence of cheap manufacturing, generative AI, automated visual reasoning tools, and lax e-commerce moderation has created a golden age for cybercriminal syndicates operating large-scale ad fraud empires. As long as unverified IoT devices can be imported and sold en masse without liability to retailers, consumers will remain unwitting accomplices in global cybercrime.
How Consumers Can Protect Themselves
Security experts emphasize that safeguarding home networks against these threats requires a combination of hardware hygiene and vigilance:
- Stick to Reputable Brands: Consumers should avoid purchasing unbranded, heavily discounted streaming sticks from unknown manufacturers promising "unlocked" or "free" premium content. Stick to verified name brands from reputable manufacturers (such as Google TV, Roku, Apple TV, and Amazon Fire TV).
- Verify Play Protect Certification: Google provides official documentation allowing consumers to check whether a device runs an authentic, certified version of Android TV equipped with Play Protect safety measures.
- Audit Installed Applications: Periodically review applications installed on smart TVs and streaming boxes. Remove any unfamiliar apps, particularly those requesting background accessibility permissions or overlay capabilities.
- Consult Threat Research Lists: Organizations like Synthient maintain public databases (such as community-driven GitHub tracking lists) cataloging known IoT product names and hardware brands that have historically shipped with pre-installed residential proxy software or malicious payloads.
- Network Segmentation: For advanced users, placing all IoT devices on an isolated Guest Wi-Fi network or VLAN (Virtual Local Area Network) prevents compromised streaming boxes from pivoting laterally to attack sensitive computers, Network-Attached Storage (NAS), and personal data on the primary home network.
As major technology platforms slowly begin to implement stricter policies—such as LG’s recent announcements banning residential proxy software from smart TV app ecosystems—the pressure on the gray-market hardware industry is mounting. However, until global e-commerce giants and regulatory bodies enforce rigorous baseline security standards for imported electronics, the living room television will remain a prime battleground in the war against automated digital fraud.