WASHINGTON — In what cybersecurity researchers are calling a critical lapse in operational security, multiple government-issued and personal devices utilized within the Executive Office of the President have been discovered running commercial residential proxy software. This oversight inadvertently turns secure federal infrastructure into commercially rentable exit nodes for global internet traffic, granting anonymous third parties open access to network pathways traditionally reserved for the highest levels of American government.
According to telemetry data compiled by threat intelligence firms Layer3 Intel and Synthient, this continuous exposure persisted across multiple weeks, utilizing dedicated IP address allocations assigned exclusively to the White House. Among the services detected operating inside the federal perimeter is Infatica, a proxy network founded by a Russian national whose past infrastructure was directly linked to foreign interference operations targeting state election systems during the 2016 U.S. presidential cycle.
The findings illuminate a pervasive, poorly understood cybersecurity blind spot: the monetization of everyday software development kits (SDKs) that quietly transform corporate, consumer, and high-security government networks into Trojan horses for global cybercrime.
Executive Overview: A Gateway Inside the Executive Office
The alarming reality of the situation is captured by a simple market dynamic: for less than the cost of a cup of coffee, any malicious actor, foreign intelligence service, or script kiddie can rent the exact digital footprint of the White House to mask their web traffic, bypass geolocation blocks, and execute cyberattacks from a seemingly trusted U.S. government IP address.
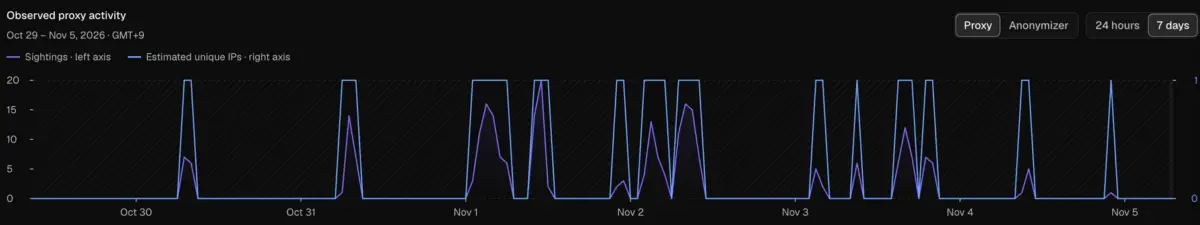
The activity was brought to light when Layer3 Intel analysts—while mapping global rotating proxy infrastructures out of routine operational curiosity—observed multiple residential proxy nodes beaconing outward from Internet Autonomous System AS2650, a network block strictly reserved for the Executive Office of the President.
Subsequent monitoring revealed that between October 5 and November 3, proxy exit traffic routed through the White House network a staggering 236 times across 26 distinct days. The traffic patterns exhibited a distinct temporal profile, concentrating heavily during evening and late-night hours between 5:00 p.m. and midnight, strongly suggesting the activity stems from staff members bringing personal or work-issued mobile devices and laptops inside the secure perimeter, where they connect to local Wi-Fi while running ad-supported or utility applications embedded with proxy SDKs.
Compounding the severity of the discovery, Layer3 Intel identified not just a single rogue application, but 28 separate residential proxy services capable of routing traffic out through the dedicated White House network block.
"This is public access," the Layer3 Intel research team noted in a technical breakdown of the incident. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars, and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
Detailed Chronology and Technical Findings
The exposure within 1600 Pennsylvania Avenue is part of a broader, systemic threat landscape that security researchers have tracked with escalating alarm over the past several years.
The Discovery Phase: October 5 – November 3
During a month-long observation window from early October to early November, Layer3 Intel’s continuous network sweeps flagged AS2650 as an active participant in global residential proxy routing rings. Analysts mapped six distinct internet addresses within the White House network space functioning as active exit nodes.
Simultaneously, proxy tracking and threat intelligence firm Synthient published telemetry data via social media identifying specific software signatures originating from AS2650. According to Synthient, the traffic was tied directly to multiple Windows 11 installations running Infatica, a controversial proxy provider that monetizes its user base by routing external traffic through consumer devices.
The Infatica Connection and the Shadow of 2016
The involvement of Infatica introduces significant geopolitical and counterintelligence concerns. Infatica was founded by Vladimir Fomenko, a Russian national whose web hosting enterprise, King Servers, played a central role in state-sponsored cyber operations nearly a decade ago.
During the 2016 U.S. presidential election cycle, King Servers acted as the infrastructure backbone for malicious actors linked to Russian state security services. Six of the eight internet addresses used to launch sophisticated, direct cyberattacks against voter registration and election administration databases in Arizona and Illinois originated from Fomenko’s hosting firm.
While there is no immediate indication that the current White House proxy exposure is tied to an active, targeted state-sponsored espionage campaign, security experts emphasize that leaving infrastructure open to a commercial network founded by an individual with historic ties to Russian intelligence operations presents an unacceptable national security risk.
Supporting Context & Metrics: The Mechanics of Residential Proxies
To understand how high-security government networks become vulnerable to commercial proxy monetization, one must examine the multi-billion-dollar shadow economy of residential IP leasing.
What is a Residential Proxy?
Unlike data center proxies—which are easily flagged and blocked by website administrators because their IP addresses belong to commercial hosting providers—residential proxies utilize legitimate internet connections assigned to ordinary consumers by Internet Service Providers (ISPs).
Proxy networks acquire access to these residential IPs by embedding monetization code (Software Development Kits, or SDKs) into seemingly innocuous mobile applications, browser extensions, and desktop software—such as free VPNs, weather widgets, QR code scanners, and casual games. When a user installs one of these applications, they often unknowingly agree to a dense End User License Agreement (EULA) that permits the app to utilize their device’s internet connection as a relay node for third-party traffic.
Once integrated, the residential proxy service rents out these endpoints to external customers. To any target website or digital service, traffic routed through a residential proxy appears to come from a legitimate homeowner, corporate employee, or, in this case, a federal staffer sitting inside the White House.
The Criminal Marketplace and the Lack of KYC
The commercial availability of these networks has democratized cybercrime. According to Ben Brundage, founder of Synthient, bandwidth across these networks can be purchased for as little as 60 cents per gigabyte.
"That means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage explained in an interview with security journalist Brian Krebs. "The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
Without rigorous identity verification standards, cybercriminals routinely leverage residential proxies to execute high-profile attacks:
- Account Takeover (ATO): Bypassing rate limits and behavioral fraud detection systems to credential-stuff and hijack user accounts.
- Ad Fraud: Generating artificial impressions and clicks on digital advertisements.
- Large-Scale Data Scraping: Harvesting protected web content, intellectual property, and personal data to fuel unverified Artificial Intelligence (AI) model training datasets.
Local Network Infiltration Risks
Beyond acting as anonymous transit points for external bad actors, residential proxies introduce critical lateral movement vulnerabilities. In late 2025 and early 2026, security researchers uncovered a widespread exploitation campaign targeting vulnerabilities within residential proxy software architectures.
Criminal syndicates—such as those operating the infamous Kimwolf botnet—discovered that they could abuse proxy endpoints to scan the local networks to which the infected host devices were attached. This allowed hackers to pivot from a compromised consumer laptop or mobile device directly into internal corporate, home, or government subnetworks, scanning for unpatched enterprise assets, misconfigured databases, and vulnerable IoT hardware to infect with secondary payloads.
The Broader Threat Landscape: Corporate and Government Vulnerabilities
While the White House breach has captured immediate public attention, security analysts stress that government agencies and Fortune 500 enterprises are grappling with a systemic epidemic of shadow proxy installations. Because these networks rely on employee behavior—such as connecting personal smartphones, tablets, or laptops to secure corporate and government Wi-Fi networks—traditional perimeter defenses frequently fail to detect them.
Data collected by proxy tracking service Spur during a comprehensive industry webinar revealed the staggering scale of the problem across critical infrastructure sectors:
- Government Networks: Nearly 300 government-owned and operated networks were found to harbor active residential proxy nodes.
- Utility Companies: 318 energy, water, and municipal utility networks contained proxy traffic.
- Healthcare & Hospitals: 166 healthcare providers and hospital networks were exposed.
- Banking & Finance: 141 financial institutions showed active residential proxy footprints.
Furthermore, enterprise security firm Infoblox published findings indicating that 65% of its entire global customer base had internal devices querying domains associated with residential proxy services. This proves that network exposure is not isolated to undisciplined or underfunded organizations, but represents a ubiquitous blind spot in modern IT management.
Official Responses and Remediation Challenges
As of press time, the White House has not issued an official public statement or response to inquiries regarding the Layer3 Intel and Synthient disclosures.
Securing the Executive Office of the President against this specific threat vector presents a formidable challenge for federal Chief Information Security Officers (CISOs). Traditional firewalls and intrusion detection systems (IDS) are designed to monitor incoming malicious traffic and block unauthorized inbound connections. However, residential proxy software operates via outbound connections—initiating encrypted TLS sessions outward to command-and-control servers maintained by proxy brokers.
To effectively eliminate this vulnerability, federal IT security teams must implement strict Endpoint Detection and Response (EDR) policies that prohibit the installation of unvetted consumer applications, enforce strict Mobile Device Management (MDM) protocols on all personal and government-issued hardware brought into secure facilities, and continuously monitor egress traffic for known proxy signaling behaviors and AS2650 routing anomalies.
Future Outlook: Regulating the Shadow Proxy Economy
The revelation that the White House network has been functioning as an unwitting proxy relay underscores an urgent need for regulatory intervention and technological adaptation.
Security experts argue that the commercial residential proxy market operates in a legal and ethical gray area that urgently requires legislative scrutiny. Unlike traditional VPN providers, which offer encrypted point-to-point tunnels for privacy, commercial proxy providers explicitly profit by reselling third-party access to unsuspecting users’ internet bandwidth without adequate transparency, consent, or accountability.
Until technology platforms, operating system vendors, and app stores crack down on the inclusion of monetization SDKs, and until governments enforce stringent device hygiene policies within secure facilities, institutions like the White House will remain vulnerable.
As Ben Brundage warned, the democratization of clandestine network access means that the barrier to breaching the world’s most sensitive institutions is no longer sophisticated code or zero-day exploits—it is often just a dollar, a commercial account, and an employee device connected to the office Wi-Fi.