Partners Neutralized a 1.3 Million-Strong Android TV Malware Empire
Executive Overview
In a massive coordinated international takedown, Google—alongside a coalition of cybersecurity firms, threat intelligence teams, and industry stakeholders—successfully dismantled the XCPE botnet. This sprawling, highly insidious criminal infrastructure had compromised more than 1.3 million Android TV set-top boxes right out of the box, converting them into silent participants in advertising fraud and illicit residential proxy networks.
The operation severed critical command-and-control (C2) domains and infrastructure linked to Videostrong Technology Co., a prominent hardware manufacturer based in China. According to investigations by the Google Threat Intelligence Group (GTIG), Videostrong deliberately baked malicious code deep into the firmware of its streaming boxes, weaponizing the devices the moment an unsuspecting consumer powered them up for the first time.
Security experts warn that the 1.3 million actively infected set-top boxes represent only the tip of the iceberg. The fallout from the takedown is expected to cut off botnet access to an estimated 10 million additional secondary systems—including Internet of Things (IoT) hardware such as karaoke machines, digital signage setups, and telehealth appliances—that sat on the same local networks and were routinely commandeered via lateral movement.
By commercializing unauthorized access to consumer internet connections, the operators of the XCPE botnet blurred the lines between legitimate monetization, gray-market residential proxies, and outright malware distribution. This deep-dive investigative report examines the architecture of the XCPE botnet, the hardware supply chain vulnerabilities that enabled its spread, the controversial role of residential proxy providers, and the far-reaching implications for consumer trust in the smart home ecosystem.
Detailed Chronology: Unraveling the XCPE Threat
The exposure and eventual neutralization of the XCPE botnet was not an overnight victory. It was the culmination of months of meticulous reverse engineering, dark web tracking, and cross-industry collaboration between cloud giants, niche threat-hunting startups, and international law enforcement agencies.
Early 2026: The Rise of Kimwolf and the Scrutiny on Smart TV Boxes
The foundation for the XCPE takedown was laid months prior, as researchers began noticing an alarming surge in network-wide disruptions. In January 2026, threat-intelligence startup Synthient published landmark research tracking the rapid horizontal expansion of the Kimwolf botnet. Kimwolf had been hammering enterprise and consumer networks worldwide with record-breaking Distributed Denial of Service (DDoS) attacks, leveraging vulnerabilities native to low-cost Android TV boxes.
Synthient’s tracking revealed a dangerous characteristic: once a single Android set-top box was compromised, it immediately scanned its local area network (LAN), using weaknesses in third-party software development kits (SDKs) to hop across boundaries and infect secondary devices—ranging from smart appliances to enterprise-adjacent healthcare equipment.
The scale of the threat caught the attention of the Motion Picture Association (MPA). Representing major Hollywood studios financially devastated by pirate streaming ecosystems, the MPA partnered with Synthient to physically purchase, disassemble, and analyze dozens of popular, pre-infected Android TV set-top boxes sold on global open-market platforms.
Mid-2026: Law Enforcement Interventions and Supply Chain Exposure
As researchers peeled back the layers of these cheap streaming boxes, they discovered deep architectural flaws. In July 2026, federal authorities—including the FBI—intervened against major residential proxy facilitators, seizing hundreds of domains associated with NetNut, an operation tied to the publicly traded Israeli firm Alarum Technologies. Investigators revealed that NetNut was intimately linked to a parallel streaming box botnet known as Popa.
Despite these enforcement actions, the hardware supply chain remained thoroughly saturated. Threat actors continually updated their payloads, finding ways to evade standard security checks enforced by major platform holders like Google.
November 2026: The GTIG and Synthient Double-Punch
The definitive breaking point arrived in November 2026. In parallel reports published by the Google Threat Intelligence Group and Synthient, investigators formally unmasked the XCPE botnet (named after a core module component) and tied its origins directly to Chinese manufacturer Videostrong Technology Co.

Google announced it had formally severed all business and certification ties with Videostrong. Simultaneously, Google launched coordinated legal actions to seize the domains, external malware-loading portals (such as com.abc[.]nexus), and server clusters used by Videostrong to maintain a persistent backdoor on millions of living-room televisions worldwide.
Supporting Context & Metrics: Anatomy of an Industrial-Scale Malware Operation
To fully comprehend the scale of the XCPE threat, one must understand how modern gray-market hardware monetization works. These are not traditional viruses designed merely to steal passwords or ransom files; they are infrastructure-as-a-service operations built to rent out bandwidth and manipulate global advertising impressions.
The Business Model: Monetizing the Living Room
According to GTIG, Videostrong didn’t just build cheap, feature-rich TV boxes; they transformed every single unit sold into a recurring revenue stream by leasing out consumer bandwidth.
When a user plugged in their new streaming box, a malicious payload executed instantly upon boot-up. This payload tied the user’s domestic internet connection into a global network of residential proxy services. These services allow third-party clients—ranging from corporate data scrapers to criminal syndicates—to route their web traffic through residential IP addresses, successfully masking their true location and identity.
Residential proxies are routinely weaponized for:
- Credential Stuffing & Account Takeovers (ATO): Bypassing rate limits and geographic blocks to brute-force user accounts on banking, gaming, and retail platforms.
- Mass Content Scraping for AI Models: Harvesting copyrighted data, social media profiles, and web content without detection.
- Advertising Fraud: Generating millions of fraudulent ad impressions and clicks to drain corporate marketing budgets.
The Hardware Culprits: MECOOL, Superbox, and "Free TV" Promises
The malware was not distributed through accidental third-party compromise or downloaded via shady browser links; it was baked straight into the device firmware at the factory level.
Synthient’s November 2026 analysis highlighted MECOOL, a popular brand distributed by the publicly traded Chinese firm Skyworth Technology. MECOOL devices—widely praised across social media and YouTube for offering hundreds of pirated pay-TV channels for a single upfront fee—were found to be fully bundled with Videostrong’s XCPE malware and secondary proxy modules.
Similarly, a November 2025 investigation by KrebsOnSecurity in collaboration with Censys uncovered identical behaviors in Superbox streaming devices. These brands relied heavily on social media influencers—particularly on platforms like TikTok and YouTube—to drive massive consumer adoption.
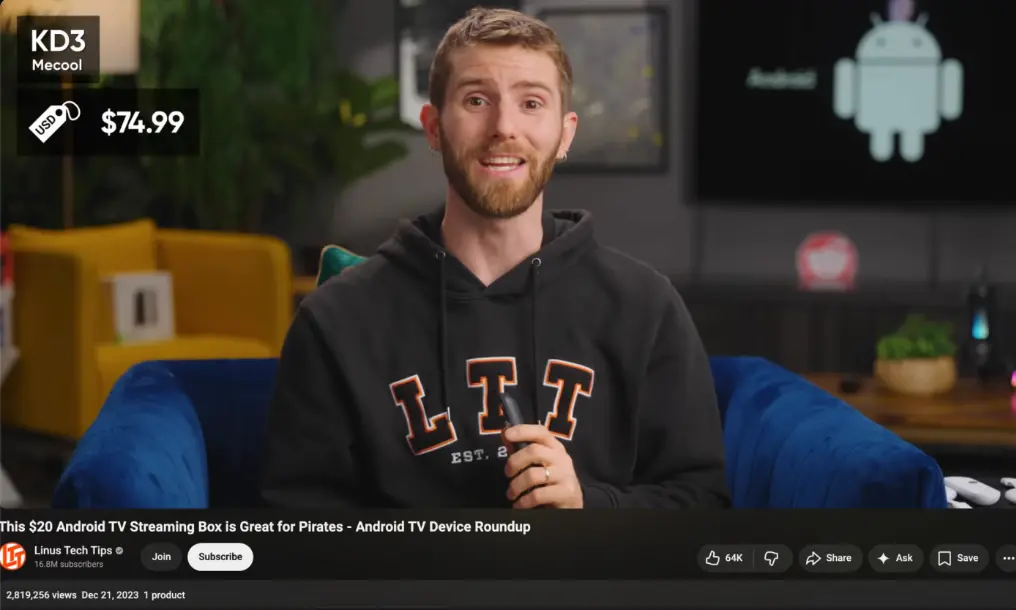
In one notable instance highlighted in the 2026 reports, the massive tech-review YouTube channel Linus Tech Tips (boasting nearly 17 million subscribers) had previously featured MECOOL boxes in historical content. Upon learning of the malware integration, the channel updated the affected videos to explicitly frame the devices as security scams and scrubbed all associated affiliate links.
The Residential Proxy Ecosystem and Complicity
GTIG’s report explicitly called out several residential proxy providers whose Software Development Kits (SDKs) were routinely downloaded and leveraged by XCPE-infected devices. These included:
- AppSalt (Honeygain): Developed by Vilnius, Lithuania-based Oxylabs. In October 2026, Oxylabs and Honeygain were reorganized under an umbrella entity named Source, following a $130 million funding injection from private equity firm Warburg Pincus that valued the business at $3.6 billion.
- Grass: A decentralized proxy network whose software was found pre-bundled on devices like Superbox.
- Other Notable Providers: EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
Official Statements & Industry Accountability
The public disclosure of the XCPE botnet forced residential proxy giants and hardware vendors to address systemic vulnerabilities in how third-party SDKs are vetted and deployed.
Oxylabs Responds to Integration Allegations
In a statement issued shortly after the initial reports went live, Oxylabs defended its operational safeguards while acknowledging glaring oversights in how malicious builders abused their SDKs.

"We have been conducting regular audits of the applications provided by our partners," Oxylabs stated. "However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application."
Oxylabs clarified that it had no direct corporate record of a company named Videostrong Technology Co., but confirmed it had contracted with an external supplier using the domain com.abc[.]nexus—a domain flagged by Google as a primary XCPE malware loader.
"As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry," Oxylabs noted. "This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves."
Google’s Stance on Ecosystem Integrity
Google emphasized that while its baseline Android requirements mandate rigorous compatibility and security testing for all partner devices, rogue manufacturers routinely employ sophisticated evasion techniques to bypass checks during initial factory provisioning.
"A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users," GTIG stated. "Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors."
Google confirmed that it has permanently plugged the firmware loopholes exploited by Videostrong, making it exponentially harder for future hardware gray-market operators to inject unverified code into Android-based set-top boxes at the assembly line.
Future Outlook: Securing the Smart Home Horizon
While the neutralization of the 1.3 million-strong XCPE botnet and the severing of access to over 10 million secondary IoT systems represents a monumental victory for cybersecurity defenders, experts warn that the war against supply chain backdoors is far from over.
The Whack-a-Mole Reality of IoT Malware
Ben Brundage, founder of Synthient, described the confirmed 1.3 million infection figure as "highly conservative."
"The scale of affected devices is likely way higher," Brundage remarked. "This is probably the largest operation against backdoored TV boxes that we’ve seen."
Because the criminal affiliates leveraging Videostrong’s infrastructure maintained diversified distribution channels beyond just the XCPE core, bad actors will inevitably attempt to migrate their modules to new manufacturers, alternative streaming boxes, and unmonitored smart home appliances.
Key Takeaways for Consumers and Network Operators
- Beware "Too Good to Be True" Hardware: Consumers purchasing ultra-cheap, unbranded, or influencer-hyped Android TV boxes promising free access to premium cable networks are frequently paying for the device with their own network security and personal data privacy.
- Network Segmentation: Smart home device owners should utilize isolated Virtual Local Area Networks (VLANs) or guest networks for IoT hardware, preventing compromised streaming boxes from scanning and laterally infecting personal computers, phones, and critical appliances.
- Stricter Supply Chain Audits: Major platform operators like Google must continue to evolve their hardware attestation frameworks, ensuring that devices cannot boot unauthorized binaries without triggering cryptographic alarms.
As regulatory bodies tighten scrutiny on the gray-market residential proxy industry and tech giants aggressively police supply chain compliance, the ecosystem is slowly closing the door on the era of unchecked living-room exploitation. However, vigilance remains the ultimate line of defense for the modern connected home.